
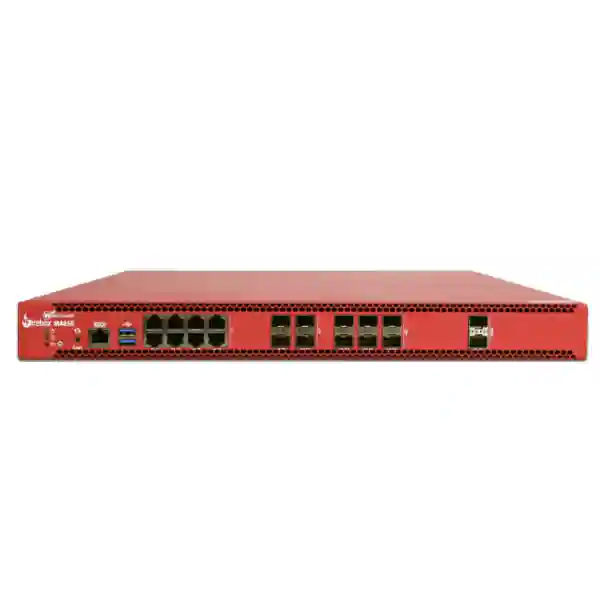
WatchGuard Firebox M4850
The WatchGuard Firebox M4850 is positioned for organizations moving beyond midrange firewall capacity and into a higher-performance rackmount security platform. It combines a 12-core Intel Granite Rapids-D HCC processor, 32 GB DDR5 ECC memory, 128 GB M.2 PCIe SSD storage, a broad mix of copper and fiber interfaces, redundant hot-swappable power supplies and an OCP 3.0 expansion bay. For buyers, the practical value is not a single headline throughput figure; it is the ability to design a firewall around inspected traffic, VPN demand, branch aggregation, segmentation, high-speed uplinks, operational resilience and future network growth.
Before requesting a quote
Prepare your internet bandwidth, expected inspected traffic, interface media, VPN users, branch tunnels, VLAN count, high-availability requirement, preferred security subscription term and deployment location. Those inputs make M4850 sizing and bill-of-material planning much more accurate.
1U rackmount platform designed for secured equipment rooms and data-center style installations.
8 × 1G RJ45, 4 × 1G SFP, 6 × 10G SFP+ and 2 × 25G SFP28.
32 GB DDR5 ECC SODIMM memory with 128 GB M.2 PCIe SSD storage.
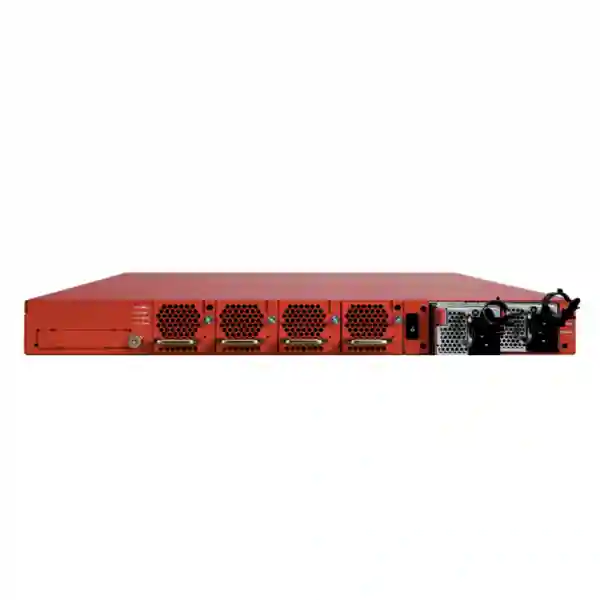
Dual hot-swappable power supplies and four hot-swappable cooling fans support serviceability.
Direct answer: who should evaluate the WatchGuard Firebox M4850?
The M4850 is most relevant to organizations that have outgrown ordinary branch firewalls and need a rackmount gateway for a busy headquarters, campus, regional hub, internet edge or consolidated multi-site environment. It is especially worth evaluating when the design calls for multiple fiber uplinks, 10G server or core connectivity, 25G handoffs, large numbers of simultaneous sessions, substantial VPN traffic, stronger resilience, or security inspection that would place too much load on a smaller appliance. The model can be managed locally through Fireware Web UI or WatchGuard System Manager, or through WatchGuard Cloud when the applicable licensing and management method are selected.
WatchGuard publishes a firewall throughput figure of 66.5 Gbps and a full-scan UTM figure of 19.1 Gbps for the M4850. These figures are useful as reference points, not as guarantees for every production network. Real performance depends on packet sizes, enabled inspection services, TLS decryption, policy complexity, logging, VPN workloads, routing behavior and traffic mix. A sound sizing exercise should therefore begin with measured peak traffic and the security functions you intend to enable, then add growth headroom.
Verified WatchGuard Firebox M4850 hardware details
| Item | WatchGuard Firebox M4850 | Buyer planning note |
|---|---|---|
| Processor | Intel Granite Rapids-D HCC, 12-core, 6th Gen Xeon-class processor | Capacity should still be sized against inspected production traffic, not CPU description alone. |
| Memory | 32 GB DDR5 ECC, 2 × 16 GB SODIMM | ECC memory is appropriate for a rackmount security appliance intended for sustained operation. |
| Storage | 128 GB M.2 PCIe SSD plus 64 MB QSPI flash | Confirm logging and retention architecture separately because cloud and subscription choices affect operational visibility. |
| Network interfaces | 8 × 1G RJ45, 4 × 1G SFP, 6 × 10G SFP+, 2 × 25G SFP28 | Confirm transceiver type, fiber standard, switch compatibility and ISP handoff before ordering optics. |
| Expansion bay | OCP 3.0 PCIe Gen 5 x8 slot | WatchGuard documents optional 4-port 25G SFP28 and 2-port 100G QSFP28 OCP cards for this family. |
| Power | 2 × hot-swappable 600 W power supplies, 100-240 VAC input | Use separate conditioned power feeds where resilience requirements justify it. |
| Cooling | 4 × hot-swappable PWM fans | Maintain clear airflow and suitable rack-room cooling; published operating temperature is 0-40°C. |
| Dimensions and weight | 440 mm deep × 515 mm wide × 44 mm high; 9 kg | Check rack depth, rail fit, cable bend radius and rear service clearance before deployment. |
Security subscription, management and high-availability planning
The appliance decision and the subscription decision should be treated as one procurement exercise. WatchGuard supports Standard Support as well as Basic Security Suite and Total Security Suite licensing paths, with cloud visibility, security-service access, retention and support entitlements depending on the chosen package. Buyers should confirm the exact security functions required during the subscription term instead of selecting a bundle solely from its name. Web filtering, intrusion prevention, malware scanning, advanced threat services, DNS security, reporting, data retention and support level can affect both operational capability and recurring cost.
For organizations using WatchGuard Cloud, the management architecture should also be decided before deployment. Cloud-managed and locally managed Fireboxes have different operational workflows, and teams should confirm administrator roles, logging expectations, configuration ownership, change-control process, backup procedures and incident-response responsibilities. If a FireCluster or high-availability design is required, verify subscription requirements for both members, link design, switch connectivity, power feeds, heartbeat/state synchronization behavior and maintenance procedures. High availability reduces single-device risk only when the surrounding network path is also designed without hidden single points of failure.
FourTeck can support the commercial and technical discovery process. Buyers can review broader firewall service and support options, compare the wider firewall product portfolio, and use the perimeter firewall planning guide to prepare deployment inputs before requesting an M4850 quotation.
Sizing the M4850 around real traffic
Inspection load
Estimate how much traffic will pass through IPS, antivirus, web controls and TLS inspection during peak business periods. Security-enabled throughput is usually the more useful sizing reference than raw firewall throughput.
Interface plan
Map ISP handoffs, core-switch links, server or data-center zones, dedicated management paths and future uplinks. Decide which connections need copper, SFP, SFP+ or SFP28 before optics are ordered.
VPN and branches
Count site-to-site tunnels, remote users, expected encrypted traffic and backup links. A multi-branch hub may have very different requirements from a single-site internet gateway with the same WAN speed.
Growth and resilience
Allow headroom for new circuits, cloud usage, additional branches, increased TLS traffic and policy expansion. If downtime has material business impact, evaluate a correctly engineered high-availability pair rather than a single appliance.
WatchGuard Firebox M4850 Dubai
Organizations searching for a WatchGuard Firebox M4850 in Dubai are typically evaluating a high-capacity perimeter firewall for a headquarters, enterprise office, campus, hospitality group, logistics hub, data-center edge or multi-branch aggregation point. The purchasing discussion should begin with the actual network role. A Dubai office using 1G internet links but heavy TLS inspection, remote-user VPN and many internal zones has different requirements from a data-center environment using multiple 10G uplinks or a 25G core connection. The M4850 offers a useful mix of 1G copper, 1G fiber, 10G SFP+ and 25G SFP28 ports, but the bill of materials must also account for transceivers, patching, rack rails, power feeds, security subscriptions and any high-availability requirement.
For Dubai procurement, ask for the appliance, license term and support entitlement to be stated separately in the quotation. This makes renewal planning easier and avoids comparing an appliance-only price with a bundle that includes security services. Confirm whether the project needs Standard Support, Basic Security Suite or Total Security Suite, and identify which services will actually be enabled. If the M4850 will replace an existing firewall, provide the current model, public IP information, NAT rules, VPN tunnels, VLANs, routing protocols, identity sources and business-critical published services. A migration should redesign weak or obsolete rules instead of copying them blindly.
Dubai installations also need practical rack planning. The M4850 is a 1U appliance with a chassis depth of 440 mm, redundant hot-swappable power supplies and active cooling. The equipment room should provide conditioned power, sufficient rear clearance and an operating environment within the manufacturer’s published limits. For companies with dual ISP links, redundant core switching or strict uptime targets, discuss whether a FireCluster design is appropriate and how switch, power and WAN redundancy will be implemented around it. FourTeck’s Firewall Dubai resource can be used to review broader gateway requirements before a model-specific quote is finalized.
WatchGuard Firebox M4850 UAE
For UAE buyers, the WatchGuard Firebox M4850 is most relevant when a firewall must serve more than a small office. A typical evaluation may involve a main site in Dubai or Abu Dhabi, branch connectivity across the Emirates, private cloud or hosted workloads, remote access for traveling staff, segmented server networks and high-bandwidth internet services. The M4850’s interface mix allows network architects to combine copper access handoffs with fiber uplinks and higher-speed core connections, while its redundant power design supports environments where maintenance and component failure need to be planned rather than treated as emergencies.
A UAE procurement team should request a complete configuration statement. That should include the exact M4850 hardware, security-suite term, support level, optics, rack accessories, high-availability components if applicable, installation scope and any migration services. Organizations often focus on initial purchase price and discover recurring subscription costs later. A cleaner process is to compare one-year, three-year and longer-term commercial options against the expected hardware lifecycle, internal budgeting policy and renewal process. The correct subscription also depends on the security services the company expects to use, the amount of cloud logging or retention required and the operational support model.
Multi-site UAE environments should map traffic before deciding that every branch needs to backhaul through the M4850. Some organizations may centralize internet security, while others use local breakout with site-to-site connectivity. The design choice affects VPN load, latency, resilience and bandwidth. If the M4850 is intended to aggregate branches, include peak encrypted throughput, expected tunnel count, failover behavior and route convergence in the sizing discussion. For broader UAE infrastructure and cybersecurity planning, buyers can also review FourTeck UAE technology solutions. Product availability, lead time and service scope should always be confirmed in the current quotation rather than assumed from a generic web listing.
WatchGuard Firebox M4850 Uganda
In Uganda, organizations considering the WatchGuard Firebox M4850 are likely to be planning a substantial central gateway rather than a small branch device. Suitable scenarios can include a large headquarters, financial or professional-services environment, university or education network, healthcare group, logistics organization, service provider, or enterprise with branches in several cities. The important question is whether the central site has enough traffic, VPN concentration, segmentation or future growth to justify this class of appliance. Buyers should record current internet capacity, expected upgrades, inter-site connectivity, business-critical applications, concurrent users and the amount of traffic that will be inspected.
WAN reliability and power quality deserve special attention in the design. Redundant hot-swappable power supplies are valuable only if they connect to appropriately protected power sources, and high availability is useful only if the surrounding switches and upstream links are also resilient. If branches connect from Kampala, Arua, Mbarara, Gulu or other locations, document primary and backup connectivity for each site, expected tunnel traffic and routing behavior during an outage. This helps determine whether the M4850 should act as a centralized VPN hub, an internet-edge firewall, a segmentation firewall, or a combination of those functions.
Procurement teams should avoid buying optics or fiber accessories until the exact switch and carrier handoffs are confirmed. The M4850 provides 1G SFP, 10G SFP+ and 25G SFP28 connectivity, but transceiver compatibility, fiber type and distance still need to match the network design. Licensing should be quoted as a defined term with clear renewal responsibility. For projects coordinated across East Africa, FourTeck’s Africa technology platform provides a regional point of reference for broader IT requirements. Final availability, delivery arrangements, support scope and warranty handling should be confirmed for the specific Uganda order.
WatchGuard Firebox M4850 Kampala
A WatchGuard Firebox M4850 deployment in Kampala can make sense where a main office or data center needs to consolidate internet security, branch VPNs and high-speed internal networks. Kampala-based organizations may have several service-provider circuits, server VLANs, guest and staff networks, cloud applications, remote users and branch links converging on the same perimeter. The M4850’s mix of copper and fiber interfaces lets architects separate these roles cleanly, but port mapping should be completed before procurement. Identify which links need 1G RJ45, which require SFP or SFP+, and whether 25G connectivity will be used immediately or reserved for future core upgrades.
For a headquarters deployment, sizing should be based on security-enabled traffic. Measure busy-hour throughput, determine how much HTTPS traffic may be decrypted and inspected, and include VPN encryption, logging and policy complexity. If the site hosts public services, review inbound publishing, NAT, DDoS protections available elsewhere in the architecture, server segmentation and administrative access. The firewall should not become the only control protecting every system. Instead, it should work with switching, identity, endpoint security, backups, monitoring and change management.
Kampala procurement teams should also plan the operational handover. Decide who owns firewall administration, how changes are approved, where backups are kept, how firmware updates are tested, and who monitors license expiry. For high-availability deployments, document failover testing and ensure both units, switches and power paths are included in the budget. If the M4850 is replacing an older WatchGuard or another firewall platform, prepare a rule-cleanup exercise before migration. Expired objects, temporary access rules and unused VPN profiles should be reviewed rather than automatically transferred. This produces a cleaner security baseline and reduces troubleshooting after the new appliance goes live.
WatchGuard Firebox M4850 Arua
For Arua, the WatchGuard Firebox M4850 would normally be evaluated for a regional hub, large institutional site or organization that aggregates several networks, rather than for an ordinary small office. A key design question is whether the local site genuinely needs high-rackmount capacity or whether the M4850 is better placed at a central data center while Arua connects securely as a branch. That decision should be based on local user count, WAN bandwidth, server presence, branch relationships, inspection requirements and the need for high-speed internal fiber connections.
Where Arua operates as a regional operations center, remote management and serviceability become important. The M4850 has redundant power supplies and hot-swappable fans, which can reduce the impact of individual component failures, but spare strategy, rack access, conditioned power and cooling should still be planned. A firewall with high performance cannot compensate for unstable upstream connectivity, so the network design should also consider backup WAN options, routing failover and how business-critical applications behave when a primary link is unavailable.
Procurement should separate core hardware, subscriptions, optics and professional services. This is particularly useful for projects where logistics and replacement lead times matter. Buyers should request written confirmation of part numbers, license duration, support entitlement and warranty process, then retain those records with the firewall documentation. If the appliance will terminate site-to-site VPNs from smaller offices, prepare an IP addressing and route plan before deployment. Avoid overlapping branch subnets because they complicate VPN and NAT design. Security policy should also distinguish staff, servers, guest access, cameras, operational devices and management networks where applicable. A structured design reduces future remote-support effort and makes it easier to add new sites without turning the firewall rule base into an unmanageable collection of exceptions.
WatchGuard Firebox M4850 Mbarara
In Mbarara, the WatchGuard Firebox M4850 may be considered by larger commercial, education, healthcare, government or regional enterprise environments that need a central security gateway with substantial growth headroom. The first step is to determine whether the site is a branch, regional hub or primary data location. If it is a branch with moderate bandwidth, a smaller platform may be more economical. If it aggregates multiple facilities, hosts servers, terminates many VPN tunnels or connects to a high-speed core, the M4850 becomes more relevant.
Mbarara buyers should build the sizing worksheet around actual business processes. Include cloud application use, video collaboration, backups, ERP traffic, remote administration, guest internet, CCTV or IoT networks and any services published to the internet. Then decide which traffic requires full security inspection and which paths may use separate controls. This avoids the common mistake of multiplying internet bandwidth by a safety factor without understanding where the inspection load really comes from. The M4850’s published performance should be treated as a vendor test reference, while the production target should include sufficient headroom for traffic growth and new security policies.
Deployment planning should also address rack power, cooling, cabling and fiber optics. The appliance supports 10G and 25G connections, but those interfaces deliver value only when the switching and server environment can use them. If the project requires high availability, budget for the second appliance, corresponding licensing/support, duplicate links and failover testing. For organizations expanding from Mbarara to other Ugandan sites, use consistent VLAN naming, address plans, VPN standards and administrator access controls. A repeatable branch template reduces deployment errors and makes central monitoring easier as the network grows.
WatchGuard Firebox M4850 Gulu
A WatchGuard Firebox M4850 project in Gulu should start with a clear definition of the site’s role. For a large regional office, institutional campus, enterprise hub or consolidated service location, the appliance can provide a high-capacity edge with multiple interface speeds and strong resilience features. For a smaller satellite branch, however, deploying the M4850 locally may create unnecessary cost and operational complexity. In that case, a central M4850 at a headquarters or data center can still support Gulu through site-to-site VPN and centrally governed security policies, subject to the architecture.
If Gulu is selected as a hub, the design should cover internet links, branch tunnels, server zones, wireless networks and management access separately. Build an interface map showing physical ports, VLAN trunks, IP ranges, routing responsibilities and failover paths. This matters because high-speed firewall hardware is often purchased before the switching design is finalized, leading to last-minute changes in optics or port assignments. Confirm SFP/SFP+/SFP28 transceiver compatibility before purchase and retain spare components where business continuity requirements justify it.
Operational readiness is equally important. Create a documented backup routine, administrator access policy, firmware maintenance process and license-renewal calendar. When security services expire, features and cloud visibility can change, so renewal should be treated as an operational dependency rather than a finance-only task. If the firewall is remote from the main IT team, plan secure out-of-band or console-access procedures and identify who can physically attend the site if a hardware intervention is required. The M4850’s hot-swappable power and fan components improve serviceability, but they do not eliminate the need for clear local procedures. A well-documented Gulu deployment is easier to support, migrate and scale than a powerful appliance installed without operating discipline.
WatchGuard Firebox M4850 Kenya
For Kenya, the WatchGuard Firebox M4850 is a candidate for larger enterprises, headquarters, service providers, campus environments and multi-branch organizations that require more than conventional branch-firewall performance. A Nairobi headquarters, for example, may need to aggregate offices, warehouses, retail sites or remote users while protecting cloud access and internal data-center networks. A coastal or regional operation may have different WAN and redundancy requirements. The design should therefore separate internet-edge performance from branch VPN, east-west segmentation and server connectivity rather than treating all traffic as one number.
Kenyan buyers should ask for a bill of materials that identifies the appliance, security suite, support term, optics, HA components, rail kit and professional services. If 10G or 25G connections will be used, document switch models, transceiver types and fiber distances before finalizing the order. Organizations with dual carriers should also define whether failover is active/passive, policy based or load shared and how routing will converge during an outage. The firewall is one element of that design; upstream provider behavior and internal switching are equally important.
Subscription planning matters over the full lifecycle. Compare the required security services, cloud visibility, support level and retention needs with the chosen bundle, then assign a named owner for renewal. Where the M4850 will replace an existing firewall, run a migration discovery that lists public services, NAT, site tunnels, user VPN, authentication, routing, VLANs and security exceptions. This avoids discovering undocumented dependencies during cutover. If the Kenyan network is expected to add branches, standardize addressing and configuration templates from the beginning. The M4850 can then function as a scalable central gateway rather than becoming a collection point for inconsistent rules created site by site.
WatchGuard Firebox M4850 Kuwait
Organizations evaluating the WatchGuard Firebox M4850 in Kuwait are typically looking for a high-capacity rackmount platform for a headquarters, campus, enterprise edge or consolidated branch architecture. The equipment is designed for indoor operation, so installation should be in a properly cooled communications or server room rather than an uncontrolled environment. Rack airflow, conditioned power and service clearance are important because the chassis uses active cooling and redundant hot-swappable components. The 1U format saves rack height, but buyers should still confirm rack depth and rail compatibility.
Kuwait networks that use high-speed fiber uplinks can take advantage of the M4850’s six 10G SFP+ and two 25G SFP28 interfaces, alongside 1G copper and SFP ports. Before purchasing optics, map the exact ISP, core-switch and server connections and verify transceiver requirements. If a data-center or campus design may move beyond 25G, discuss whether the optional OCP expansion path is relevant, while checking current compatibility and bill-of-material details. Capacity should be evaluated against encrypted and inspected traffic, not only raw circuit speed.
Commercially, request separate visibility into hardware cost, subscription term, support entitlement and deployment services. This makes renewal budgeting easier and helps procurement compare equivalent configurations. For a high-availability pair, confirm licensing/support for both units and include redundant switching and power paths in the architecture. If the firewall will serve remote branches, identify expected VPN traffic and failover needs. Organizations should also define who will own WatchGuard Cloud or local-management administration, how configuration changes are approved and how logs are retained for operational or compliance purposes. These questions make the quotation and deployment plan more useful than a simple request for a device price.
WatchGuard Firebox M4850 Ghana
In Ghana, the WatchGuard Firebox M4850 can be evaluated for enterprises that need a robust central firewall for headquarters, branch aggregation, campus security or data-center edge use. The model’s high-speed interface mix is particularly relevant where the core network already uses fiber and where growth is expected beyond ordinary 1G connectivity. A buyer should first document current and planned WAN speeds, server and cloud traffic, remote-user VPN, branch connectivity and the level of security inspection required. This determines whether the M4850 is appropriately sized or whether another Firebox class would be more economical.
For Accra-based headquarters or other central sites, network segmentation should be part of the design from the beginning. Staff, servers, guest Wi-Fi, voice, cameras, operational technology and management networks may need different policies. The M4850 can provide the enforcement point, but the switching environment must carry the VLANs correctly and routing ownership should be clear. If multiple internet providers are used, define failover and route behavior, including how inbound services and VPN tunnels will recover when the primary link changes.
Procurement teams should obtain written confirmation of current availability, exact appliance part, license duration, security bundle, optics, support and warranty handling. Avoid assuming that an online appliance listing includes the subscriptions required for the intended security services. If the deployment is replacing an older firewall, schedule time for configuration review and cleanup. Old rules, unused objects, stale VPN profiles and undocumented NAT entries can create risk if they are transferred automatically. Ghana projects with remote branches should also consider how local support, spare optics, power conditioning and secure remote administration will be handled. A consistent operational plan can be as important as the firewall’s published performance when the goal is dependable security over several years.
WatchGuard Firebox M4850 Nigeria
Nigeria-based organizations considering the WatchGuard Firebox M4850 may be dealing with large user populations, multiple offices, cloud-heavy applications, substantial VPN demand or high-speed data-center connectivity. In Lagos, Abuja or other major business locations, the correct design depends on whether the appliance will be used primarily for internet security, branch aggregation, segmentation, published services or several of these functions at once. The more roles a single firewall performs, the more carefully peak traffic, session load, policy complexity and failure impact need to be assessed.
Resilience planning is especially important for a central gateway. The M4850 provides redundant hot-swappable power supplies and serviceable cooling fans, but organizations should also evaluate UPS capacity, generator or alternate power strategy, dual network paths, carrier redundancy and switch design. A high-availability firewall pair can reduce appliance risk, yet it will not protect against a shared upstream circuit or a single core switch. Design reviews should therefore trace the complete traffic path from ISP to firewall to switching and critical services.
For procurement, compare like-for-like bundles. An appliance-only quotation is not equivalent to a package that includes Basic or Total Security Suite subscriptions, support, optics and implementation. Ask suppliers to identify each component and the renewal date. If thousands of users or many branch tunnels depend on the M4850, include configuration documentation, backup testing, administrator controls and monitoring in the project scope. Before migration, inventory existing VPNs, public IPs, routing, NAT, VLANs and authentication systems. Large Nigerian networks often evolve through many changes; the migration is an opportunity to remove stale access and standardize policy rather than preserve years of accumulated exceptions. The result should be a firewall architecture that is easier to operate as the organization adds sites, circuits and security services.
WatchGuard Firebox M4850 Seychelles
For Seychelles, the WatchGuard Firebox M4850 is most likely to fit a larger organization, central data environment, major hospitality operation, financial or institutional network, or multi-site enterprise that needs a powerful centralized security gateway. Because island logistics can make replacement planning more significant, buyers should evaluate resilience and spare strategy alongside throughput. The M4850 includes redundant power and hot-swappable fans, but a complete continuity plan may also require UPS coverage, backup WAN connectivity, documented configuration backups, spare optics and clear escalation procedures.
Connectivity architecture should be reviewed carefully. If the site has limited upstream bandwidth but a fast internal core, the M4850 may still be useful for segmentation and branch aggregation, but the business case should be based on actual network roles. If 10G or 25G fiber is used internally, verify switch interfaces and transceivers before ordering. For organizations serving guest networks, staff systems, payment platforms, cameras and operational devices, separate VLANs and policy zones can reduce unnecessary lateral access. The firewall should be integrated into that segmentation plan rather than installed only as an internet-edge box.
Seychelles procurement teams should also focus on lifecycle clarity. Request the hardware, security subscription, support term, warranty process, delivery assumptions and any onsite or remote deployment services as separate line items. Determine who will manage the device, who receives license-expiry notices and how firmware updates are scheduled. If a second appliance is required for high availability, include it from the beginning so power, cabling and switch ports are designed correctly. Where remote support is important, ensure secure administrative access is available without exposing management interfaces directly to untrusted networks. These practical controls help the M4850 deliver dependable value even when physical access, shipping or replacement logistics require more advance planning.
Frequently asked questions about the WatchGuard Firebox M4850
What is the WatchGuard Firebox M4850 designed for?
It is a high-rackmount Firebox intended for organizations that need higher security performance, large session capacity, extensive high-speed connectivity and enterprise-oriented resilience. It is suitable for evaluation at headquarters, campuses, larger branches, internet edges, regional hubs and data-center style environments where smaller appliances may not provide enough capacity or interfaces.
Does the M4850 include 10G and 25G ports?
Yes. WatchGuard documents six built-in 10G SFP+ interfaces and two built-in 25G SFP28 interfaces, in addition to four 1G SFP and eight 1G RJ45 ports. Optics are design dependent, so confirm supported transceivers and fiber requirements before ordering.
Can the Firebox M4850 be managed in WatchGuard Cloud?
WatchGuard documents cloud-managed and locally managed deployment methods for this Firebox family. The applicable license and management approach should be selected before deployment because logging, reporting, retention and operational workflows depend on the chosen setup.
Which security subscription should I choose?
Choose based on required security services, support level, cloud visibility, retention needs and budget over the intended term. Standard Support, Basic Security Suite and Total Security Suite are different commercial and functional paths. Ask for the exact entitlements in writing and compare the renewal implications.
Should I buy one M4850 or a high-availability pair?
That depends on the business impact of an appliance outage and the resilience of the rest of the network. A high-availability design is most useful when WAN links, core switching and power paths are also engineered to avoid shared single points of failure. Confirm cluster licensing, subscriptions, cabling and failover procedures before purchase.
What information should I send for an accurate quote?
Send target country and site, quantity, internet speeds, peak inspected traffic, user and device counts, VPN users, branch tunnels, required port media, optics, high-availability requirement, preferred license term, current firewall details, migration scope and whether configuration or installation assistance is required.
Related firewall planning resources
Firewall services
Review configuration, migration, VPN, troubleshooting and support considerations before defining the M4850 deployment scope.
Firewall products
Compare the M4850 requirement with other firewall classes when capacity, budget, licensing or interface needs are still being evaluated.
Perimeter firewall design
Use a structured gateway checklist for user count, WAN links, inspection, VPN, segmentation, licensing and deployment readiness.
Decision recap
Choose the WatchGuard Firebox M4850 only after confirming that its performance class, ports and resilience match your actual workload. Its strongest fit is a demanding headquarters, campus, regional hub or data-center edge where inspected traffic, large session counts, VPN aggregation or high-speed fiber connectivity exceed the practical scope of smaller firewalls. Build the decision around enabled security services, traffic growth and operating procedures rather than headline throughput alone.
Peak inspected traffic, VPN demand, ports, optics, branch count and three-year growth.
Hardware, subscription, support, optics, HA, deployment and renewal ownership.
Rules, NAT, VPNs, routes, public IPs, identity sources, VLANs and rollback plan.
Quotation checklist
- Confirm the exact WatchGuard Firebox M4850 hardware quantity and deployment country.
- State desired Standard Support, Basic Security Suite or Total Security Suite term.
- List required 1G, 10G and 25G optics and the connected switch or carrier interfaces.
- Specify whether the project needs a single appliance or a high-availability pair.
- Provide internet bandwidth, peak inspected traffic, users, devices, VPN users and branch tunnels.
- Include current firewall details and migration scope when replacing an existing gateway.
- Request separate pricing for hardware, subscriptions, support, accessories, deployment and optional ongoing services.
Plan your WatchGuard Firebox M4850 deployment with FourTeck
Share your site location, internet links, user count, inspection requirements, VPN design, interface plan, subscription preference and migration scope. FourTeck can use those inputs to prepare a more useful quotation and identify questions that should be resolved before the appliance, licenses and optics are ordered. Availability, regional delivery, support scope, warranty handling and implementation services should be confirmed in the current quotation.


Reviews
There are no reviews yet.