
Sophos XGS 2100 Firewall in Dubai, UAE
The Sophos XGS 2100 is a versatile 1U rackmount firewall appliance for organizations that need high-speed inspection, secure site connectivity, controlled internet access and room to expand. FourTeck helps UAE buyers evaluate appliance capacity, protection subscriptions, interfaces, VPN requirements, rollout design and ongoing support considerations before purchase.
Quick Information
Sophos
XGS 2100
1U rackmount
8 GE + 2 SFP
1 Flexi Port bay
FourTeck UAE
Overview of the Sophos XGS 2100
The Sophos XGS 2100 sits in the rackmount segment of the XGS Series and is aimed at midsize offices, distributed organizations, branch aggregation points and growing businesses that require more performance and interface flexibility than a typical desktop appliance. Its role is broader than basic internet filtering. Correctly licensed and configured, it can act as the policy enforcement point for internet access, application control, intrusion prevention, site-to-site connectivity, remote-access VPN, SD-WAN routing and inspection of encrypted traffic.
A key design consideration is its Xstream architecture, which combines general-purpose processing with dedicated acceleration intended to help handle security inspection and application traffic efficiently. In real deployments, the result depends on the services switched on, the number of rules, the volume of encrypted traffic, the mix of applications, the firmware release and the way the network is segmented. Published headline throughput should therefore be used as a comparison reference rather than a direct promise of production performance.
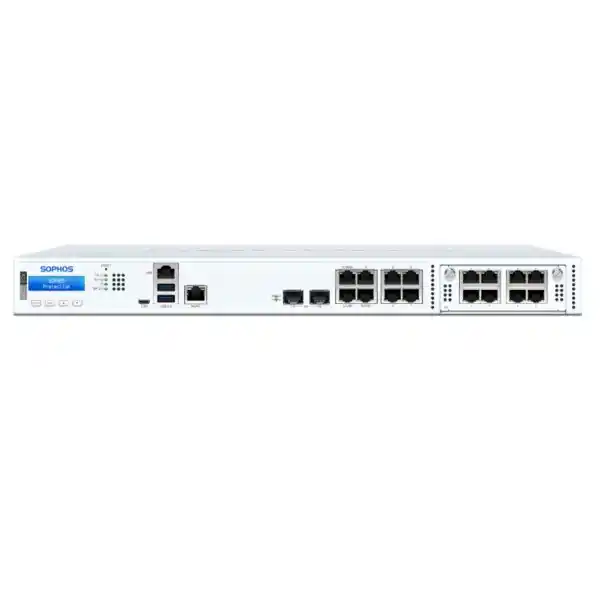
The appliance has eight Gigabit Ethernet interfaces and two SFP interfaces as standard, together with an expansion bay for supported Sophos Flexi Port modules. This makes the XGS 2100 suitable for networks that may begin with copper WAN and LAN links but later require additional fibre, higher-speed uplinks or a revised port layout. Buyers should confirm the exact module, transceiver, cable and switch compatibility needed for their design.
Why This Firewall Matters for Business Security
Modern business traffic is dominated by cloud applications, encrypted sessions, video collaboration, remote users and third-party connections. A firewall that only permits or blocks ports cannot give security teams enough context. The XGS 2100 can support policy decisions based on users, applications, networks and security events, helping organizations move from broad access rules to more controlled and auditable traffic handling.
For businesses with several offices, secure connectivity is equally important. Site-to-site IPsec VPN can link locations, while SSL VPN and other supported remote-access methods can provide controlled access for staff and administrators. SD-WAN features can help organizations use multiple internet links more intelligently, subject to correct licensing, link design and policy configuration. High-availability designs are also possible, but buyers must budget for the second appliance, compatible subscriptions, cabling and deployment work.
The firewall also becomes a source of operational insight. Logging and reporting can help administrators investigate blocked traffic, identify unusual application use, review VPN activity and tune policies. Central management options can simplify administration where several Sophos firewalls are deployed. Reporting depth, retention and advanced management functions may depend on subscription and platform choices.
Key Business Benefits
Consolidated Edge Security
Bring firewall policy, intrusion prevention, application control, web filtering, VPN and routing functions into one managed platform, subject to the selected subscriptions.
Expandable Connectivity
Use the built-in copper and SFP ports, then plan supported Flexi Port expansion when the network needs additional or different interface types.
Secure Multi-Site Links
Build encrypted links between offices and data locations, with routing and SD-WAN policies designed around business-critical applications.
Central Visibility
Monitor firewall health, policy events and selected reporting through available local and cloud management capabilities.
Encrypted Traffic Controls
Apply TLS inspection where legally and operationally appropriate to reduce blind spots in encrypted sessions.
Growth-Oriented Platform
Support a developing network with rackmount deployment, optional interface expansion and a choice of protection bundles.
Product Highlights
Published firewall throughput
Published IPsec VPN throughput
Published threat protection throughput
Published Xstream SSL/TLS inspection throughput
Performance figures are vendor test references. Actual results vary according to traffic profile, packet size, enabled services, policies, encryption, firmware and network design.
Technical Specification Table
| Brand | Sophos |
| Model | XGS 2100 |
| Product Type | Next-generation firewall appliance |
| Form Factor | 1U rackmount |
| Firewall Throughput | Up to 30 Gbps, vendor test reference |
| IPsec VPN Throughput | Up to 17 Gbps, vendor test reference |
| Threat Protection Throughput | Up to 1.25 Gbps, vendor test reference |
| Xstream SSL/TLS Inspection | Up to 1.1 Gbps, vendor test reference |
| Built-in Interfaces | 8 x Gigabit Ethernet and 2 x SFP |
| Expansion | 1 bay for supported Flexi Port module |
| Maximum Port Count | Configuration dependent; contact FourTeck for module guidance |
| High Availability | Supported configuration; second appliance and design required |
| VPN Support | IPsec and supported remote-access VPN options; configuration dependent |
| SD-WAN | Supported; feature and license dependent |
| Security Services | IPS, web and application controls, malware protection, TLS inspection and other services according to subscription |
| Management | Local administration and supported Sophos Central capabilities |
| Logging and Reporting | Feature, storage and subscription dependent |
| Wireless Support | No integrated wireless radio; supported wireless management options are configuration dependent |
| PoE Support | Module and configuration dependent |
| Warranty Guidance | Depends on appliance entitlement and support selection; confirm before ordering |
| Availability | Contact FourTeck for current UAE options, lead time and bundle choices |
Configuration and Buyer Guidance
Start with inspected traffic, not internet speed alone
A common sizing mistake is to compare only the ISP circuit speed with the headline firewall throughput. The more useful figure is the expected traffic after the required security services are enabled. Intrusion prevention, malware scanning, application control and TLS inspection consume resources differently. A 1 Gbps internet connection with broad TLS inspection may require more practical headroom than a faster connection carrying mostly trusted site-to-site traffic.
Count users, devices and simultaneous sessions
User count alone does not describe demand. A business with 150 staff may operate hundreds of phones, cameras, access points, printers, servers and cloud-connected devices. Guest Wi-Fi and unmanaged devices can further increase concurrent sessions. FourTeck can help buyers document device density, peak-hour traffic and expected growth before selecting the appliance and subscriptions.
Map interfaces before purchase
Confirm how many WAN links, switch uplinks, DMZ networks, server zones and management interfaces are required. Identify whether each link uses copper or fibre and whether 1 GbE or higher-speed connectivity is expected. The Flexi Port bay is valuable, but the correct module and optical transceivers must be selected as part of the design.
Choose the protection subscription carefully
The base appliance and a full protection bundle are not the same commercial package. Security services, updates, support level and term length can vary. Buyers should decide whether they require a one-year or multi-year term, which inspection services are mandatory and whether advanced reporting or centralized management is part of the operational plan.
Plan migration and rollback
A firewall replacement affects routing, NAT, VPN, DNS, authentication and application publishing. Before cutover, document the existing rule base, remove obsolete rules, verify public IP dependencies and prepare a rollback path. Testing should include business applications, inbound services, remote access, branch tunnels, voice traffic and monitoring systems.
Ideal Business Use Cases
Growing Head Office
A developing company can use the XGS 2100 as its primary internet edge, separating staff, server, voice, guest and management networks while applying different controls to each zone.
Multi-Branch Organization
Businesses with several locations can terminate site-to-site VPNs, define SD-WAN routes and centralize policy visibility, provided the design accounts for aggregate traffic and resilience.
Education and Training Campus
Institutions can segment administration, students, laboratories, guests and services, then apply web, application and bandwidth policies appropriate to each group.
Hospitality and Retail Operations
The firewall can separate guest access, point-of-sale systems, office users, IoT devices and vendor connections while supporting secure links to other sites.
Professional Services Firm
Legal, consulting, engineering and finance teams can combine controlled remote access, application visibility, web security and encrypted site connectivity.
Warehouse or Light Industrial Site
Organizations can isolate operational systems from corporate users, restrict third-party access and connect remote facilities through managed VPN policies.
Xstream Architecture and Inspection Performance
The XGS platform is designed to accelerate selected traffic handling while maintaining security inspection. This matters because encrypted applications, cloud services and high session counts place sustained pressure on a gateway. The XGS 2100 provides published reference figures for firewall, VPN, threat protection and SSL/TLS inspection, allowing buyers to compare it with adjacent models.
Performance planning should still be conservative. Laboratory tests use controlled conditions that may differ from a production network. Small packets, many short sessions, complex rules, extensive logging and wide TLS inspection can reduce usable throughput. The safest approach is to profile current traffic, identify peak demand, estimate growth and leave operating headroom for firmware updates and new security services.
FourTeck can assist with a sizing discussion that separates internet bandwidth, east-west traffic, branch VPN traffic and remote-user demand. This gives buyers a clearer basis for deciding whether the XGS 2100 is appropriate or whether a smaller or larger model should be evaluated.
Application, Web and Threat Controls
Business networks need more than a list of blocked websites. Application control can identify and manage traffic categories that share common ports, while web policies can apply acceptable-use rules to users and groups. Intrusion prevention can examine traffic for exploit patterns and known attack activity. Malware and sandbox-related capabilities depend on the chosen subscription and service configuration.
Effective policy design begins with business requirements. Finance applications, ERP traffic, voice, video meetings and cloud backups may need different treatment. Security teams should avoid enabling every control globally without testing because aggressive inspection can disrupt applications or create unnecessary load. A staged rollout—observe, classify, pilot and enforce—usually produces a more stable result.
Encrypted traffic inspection requires special care. Organizations need a certificate deployment plan, exclusions for sensitive or incompatible services, legal and privacy review, and testing across managed endpoints. Where decryption is not appropriate, metadata-based controls and other security layers can still contribute to visibility.
VPN, SD-WAN and Business Continuity
The XGS 2100 can support secure connectivity between offices and provide remote-access options for authorized users. Site-to-site IPsec VPN is commonly used to connect branches, warehouses and cloud environments. Remote access should be paired with strong authentication, limited user permissions, endpoint security and clear offboarding procedures.
SD-WAN policies can use multiple links based on performance, availability and business priority. For example, a company may prefer a primary leased line for voice and ERP traffic while keeping broadband or cellular connectivity as a backup. Successful SD-WAN deployment requires meaningful health checks, realistic failover thresholds and testing of return paths, DNS behavior and session persistence.
For environments where downtime carries a high cost, two compatible appliances can be designed as a high-availability pair. HA is not simply a checkbox. The design must consider duplicate power, switch connectivity, synchronization, maintenance procedures, licensing and the failure modes of upstream services. FourTeck can help buyers identify the infrastructure needed around the firewall so that the wider solution does not depend on a single unprotected component.
Buyer Checklist
UAE Availability and Service Support
FourTeck supports businesses evaluating the Sophos XGS 2100 in the UAE. Assistance can include model comparison, specification review, bundle selection, license-term guidance, interface planning, quotation preparation and coordination for deployment services. Current appliance availability, lead time, bundle SKUs and commercial terms should be confirmed at the time of enquiry.
Deployment support can be scoped around the customer environment. Typical activities may include requirements discovery, configuration planning, policy migration, interface setup, VLAN and zone design, NAT, site-to-site VPN, remote access, SD-WAN policy, logging, testing and handover documentation. The exact scope depends on the condition of the existing network and the support package agreed.
Customers can explore the firewall product portfolio, review available firewall services or contact the FourTeck firewall team for a tailored discussion.
Dubai, Abu Dhabi, Sharjah and Ajman Coverage
FourTeck coordinates firewall enquiries and project support for organizations across Dubai, Abu Dhabi, Sharjah and Ajman. The appropriate delivery, remote assistance or site-service arrangement depends on the project scope, location, access requirements and scheduling. Multi-site customers can request a consolidated plan covering appliance selection, policy standards, branch connectivity and phased migration.
For organizations replacing an older firewall, FourTeck can help prepare a structured information list before implementation. This can include WAN details, public IP mappings, internal subnets, VLANs, VPN peers, published services, authentication sources and critical application flows. Better documentation reduces cutover risk and makes future troubleshooting easier.
GCC and Africa Availability
Organizations with regional operations can discuss coordinated firewall requirements across selected GCC and African markets. Product sourcing, licensing, remote configuration, local delivery coordination and on-site service availability vary by country and should be confirmed for each location. FourTeck regional resources include Kuwait, Kenya, Uganda and the broader Africa service network.
A regional standard can simplify rule naming, VPN design, logging and operational handover, but each country may have different connectivity, compliance and support conditions. Buyers should plan local variations rather than assuming that one configuration can be copied without review.
Related FourTeck Products and Services
Protection Subscriptions
Select Standard, Xstream or other available subscription options according to the required inspection, support and reporting features.
Flexi Port Modules
Expand interface choices with a supported module selected for the required copper, fibre and speed profile.
Firewall Migration
Plan the move from a legacy firewall with rule review, NAT mapping, VPN recreation, validation and rollback preparation.
VPN and SD-WAN Setup
Create resilient branch connectivity, health checks and traffic steering policies aligned with application priorities.
High-Availability Planning
Assess dual-appliance design, cabling, switch paths, power and maintenance procedures for improved service continuity.
Policy Review and Support
Improve rule clarity, remove obsolete access, review objects and align logging with operational needs.
Why Buyers Choose FourTeck
Firewall purchasing is most successful when hardware, licensing and deployment are considered together. FourTeck focuses on practical buyer guidance rather than treating the appliance as an isolated box. The team can discuss network size, security services, interfaces, remote access, branch connectivity, growth and migration requirements before preparing a quotation.
Learn more about FourTeck and its approach to business technology projects.
Frequently Asked Questions
Is the Sophos XGS 2100 suitable for a midsize business?
It is positioned for midsize and distributed environments, but suitability depends on inspected throughput, device count, concurrent sessions, VPN load, interfaces and expected growth. FourTeck can help compare these requirements with the appliance capabilities.
What ports are built into the XGS 2100?
The appliance includes eight Gigabit Ethernet ports and two SFP ports. It also has one expansion bay for a compatible Sophos Flexi Port module. Transceivers and optional modules should be selected separately according to the network design.
Does the appliance include all security services?
No. The hardware, base functionality, protection subscriptions, support level and term are separate commercial considerations. The exact services available depend on the selected bundle and active subscriptions.
Can the XGS 2100 inspect encrypted traffic?
It supports SSL/TLS inspection capabilities. Deployment should include certificate planning, application testing, privacy review and appropriate exclusions. Published inspection throughput is a test reference and not a guarantee for every environment.
Can it be configured as a high-availability pair?
Supported HA configurations are possible with two compatible appliances and the correct design. Buyers should also plan duplicate links, switch connectivity, power, subscriptions and maintenance procedures.
Does FourTeck provide installation and migration support?
FourTeck can scope configuration, migration, VPN, policy, testing and handover services. The exact work depends on the existing environment, documentation quality, number of sites and agreed project scope.
How do I choose between one-year and multi-year licensing?
Consider budget planning, expected appliance lifecycle, support requirements and the cost of renewing annually. Current bundle terms and pricing should be compared at quotation stage.
What information is needed for a quotation?
Provide the number of users and devices, internet speed, security services, WAN links, port types, VPN sites, remote users, HA requirement, license term and any migration or installation support needed.
Is the XGS 2100 available in Dubai and the UAE?
Availability, lead time, region-specific part number and bundle options can change. Contact FourTeck for current UAE supply information rather than relying on an unconfirmed stock statement.
How is warranty coverage determined?
Coverage depends on the appliance entitlement, support plan, region and commercial package. FourTeck can clarify the applicable guidance for the quoted configuration before purchase.
Get Buying Assistance for the Sophos XGS 2100
Share your user count, internet speed, interface needs, VPN requirements and preferred subscription term. FourTeck will help you review the configuration and request a current UAE quotation.
