

Direct answer for buyers
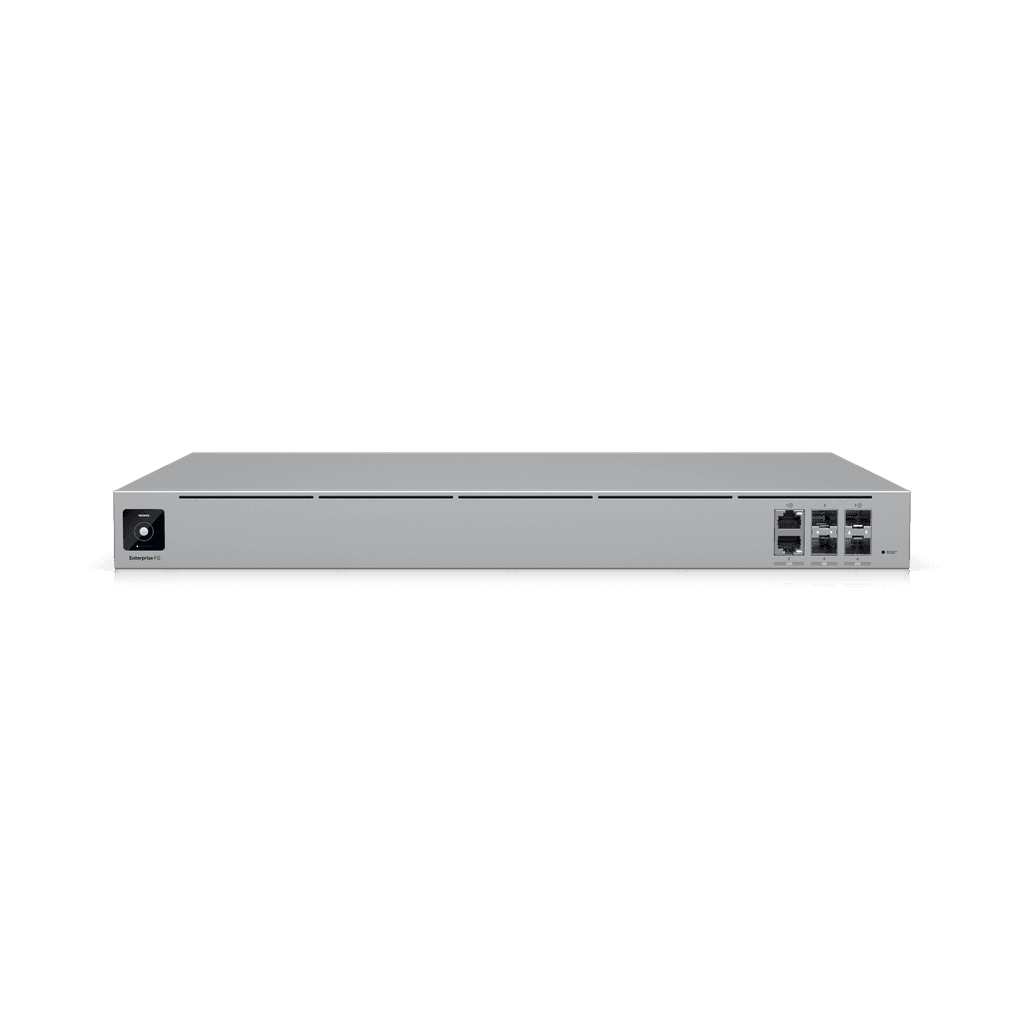
The Ubiquiti Enterprise Fortress Gateway EFG is a 1U enterprise UniFi gateway that combines routing, firewalling, VPN, threat inspection and UniFi Network management. It is mainly used at the network edge of large offices, campuses, hospitality properties, education sites and other environments with substantial device counts, high-speed internet links or demanding segmentation needs. Organisations should consider it when lower-tier UniFi gateways no longer provide enough port speed, inspection capacity or resilience. Before proceeding, confirm actual WAN bandwidth, traffic mix, required security functions, SFP28 or SFP+ media, switch design, application-hosting needs and whether high availability requires two EFG units. Availability, lead time, support scope and regional warranty terms should also be confirmed in the quotation.
What the EFG does
The EFG provides the routing and security boundary between internal networks, internet services, remote users and connected sites. It can identify applications, enforce firewall policy, inspect traffic, create VLAN and subnet boundaries, terminate VPN connections, use policy-based routing and manage multiple WAN links. Because UniFi Network runs directly on the appliance, administrators can manage compatible UniFi switches, access points and the wider network from the same UniFi interface.
Its value is not simply a headline port speed. The practical benefit comes from combining high-capacity interfaces, a large session table, enterprise routing features and a unified operational view. A successful deployment still depends on correct policy design, careful migration, suitable optics or direct-attach cables, properly sized upstream services and realistic performance expectations when multiple inspection features are enabled.
Who should evaluate it
The EFG is suited to IT teams standardising on UniFi across a high-density or multi-building environment. It may fit enterprise offices, school or university campuses, hotels, healthcare administration networks, warehouses, retail groups, technology facilities and managed environments where many access points, switches and users are coordinated through UniFi Network.
It is less appropriate when the requirement is modest, when an organisation needs a gateway that also hosts UniFi Protect or other applications, or when mandatory security functions require a different vendor ecosystem, certification framework or support model. Buyers should compare the EFG against the operational standards, compliance obligations and escalation processes already used by the organisation rather than choosing it from throughput figures alone.
Business challenges the EFG can help address
Gateway throughput pressure
Faster internet services and heavier east-west traffic can expose limitations in smaller gateways. The EFG provides multi-gigabit interfaces and high inspection throughput, but sizing should still account for enabled features, encrypted traffic, VPN use and real application patterns.
Fragmented network management
Separate tools for routing, wireless and switching can slow routine work. The EFG hosts UniFi Network and can centralise visibility and policy for supported UniFi infrastructure, reducing interface changes for day-to-day network administration.
Single gateway dependency
A lone gateway can become a critical failure point. A pair of EFG units can use Shadow Mode for active-passive failover, while dual hot-swappable power supplies reduce the effect of a single power-supply failure within each appliance.
Growing segmentation needs
Guest access, staff networks, voice, building systems, cameras, servers and operational technology often need distinct trust zones. VLAN, subnet and zone-based policies can help create clearer boundaries when they are designed and documented properly.
Core capability band
Product-fit decision matrix
| Requirement | Suitable when | Confirm before ordering |
|---|---|---|
| High-speed WAN or aggregation | The design needs 10G or 25G gateway interfaces and compatible upstream equipment. | Media type, optics, distance, supported speeds, ISP handoff and switch-port configuration. |
| Large UniFi estate | Hundreds of UniFi devices or several thousand clients may need integrated Network management. | Actual device mix, telemetry load, site count, configuration complexity and growth forecast. |
| Gateway high availability | The organisation requires a standby gateway to take over after primary appliance failure. | Two EFG units, supported UniFi OS version, cabling, WAN topology and failover testing plan. |
| Advanced security inspection | Application control, IDS/IPS, filtering and encrypted-traffic inspection align with policy needs. | Certificate deployment, exclusions, privacy obligations, subscription-dependent signatures and performance impact. |
| All-in-one UniFi applications | The requirement is UniFi Network management, routing and security. | The EFG runs Network only; Protect, Access, Talk and other applications need separate suitable consoles. |
Verified technical information
The following values are based on Ubiquiti’s published EFG technical specifications. They describe the appliance platform, not a guaranteed result in every deployment. Effective throughput and capacity vary with traffic composition, enabled inspection features, VPN protocol, rule complexity, software version, transceivers and the design of connected systems.
| Brand | Ubiquiti |
|---|---|
| Product name and model | Enterprise Fortress Gateway, EFG |
| Product type | Enterprise UniFi Cloud Gateway with integrated UniFi Network application |
| Form factor | 1U rack mount |
| Dimensions | 442.4 × 43.7 × 325 mm |
| Weight | 6.5 kg |
| Processor | 18-core ARM v8.2 at 2 GHz |
| Managed UniFi devices | 500+ |
| Simultaneous connected users | 5,000+ |
| Port layout | (2) 2.5GbE RJ45, (2) 10G SFP+, (2) 25G SFP28; ports are role-remappable within supported configuration |
| Maximum WAN port count | 5 |
| Default WAN interfaces | (1) 25G SFP28 and (1) 2.5GbE RJ45 |
| IDS/IPS throughput | 12.5 Gbps published rating |
| Concurrent sessions | 1 million |
| New sessions per second | 71,000 |
| SSL/TLS inspection sessions | 10,000 concurrent sessions |
| Routing | OSPF, BGP, policy-based routing, multi-WAN load balancing, advanced NAT and IPv6 ISP support |
| VPN support | Site Magic, IPsec, OpenVPN, WireGuard, Teleport, L2TP and identity-based options as supported by current software |
| High availability | Shadow Mode using VRRP with a second EFG; software and topology requirements apply |
| Power supplies | Two hot-swappable 150W CRPS units |
| Maximum power consumption | 82W |
| Input power | 100–240V AC, 50/60 Hz |
| Display | 1.3-inch touchscreen |
| Operating temperature | 0 to 40°C |
| Operating humidity | 5% to 95% non-condensing |
| Availability and warranty | Contact FourTeck for current UAE availability, regional warranty guidance and vendor lead time |
Configuration, subscription and compatibility notice
Some EFG capabilities depend on software version, configuration, endpoint certificate deployment or an optional subscription. Ubiquiti lists a larger IDS/IPS signature set with CyberSecure Enterprise, so buyers should not assume every signature or enhanced threat-update feature is included without checking the current licensing policy. SSL/TLS inspection also requires operational planning because managed endpoints may need a trusted certificate, and applications using certificate pinning can require exclusions or alternative handling.
SFP28 and SFP+ ports do not remove the need to select correct modules and cabling. Confirm wavelength, fibre type, connector, distance, direct-attach cable length, supported speed and compatibility at both ends. A 25G port connected to a switch or provider handoff still requires the entire link path to support the chosen media and speed. For Shadow Mode, purchase planning should cover two matching EFG gateways, current UniFi OS, consistent WAN presentation, downstream topology, power diversity, rack space and a documented failover test.
Purchase and deployment journey
Define the edge requirement
Document internet circuits, provider handoffs, public addresses, VLANs, routing protocols, remote sites, user count, device count and expected growth.
Select interfaces and accessories
Choose copper, fibre or direct-attach connectivity based on the ISP, aggregation switch, distance, rack layout and required link speed.
Build the policy plan
Map zones, firewall rules, content controls, VPNs, NAT, routing, logging and administrator access before migration begins.
Prepare migration and rollback
Back up the existing environment, align software versions, schedule a change window and document a practical route back if a dependency is missed.
Validate under real conditions
Test internet access, internal routing, applications, VPNs, inspection, logging, failover and monitoring with representative traffic rather than a single basic speed test.
High-capacity routing without losing operational context
The EFG’s 25G SFP28 and 10G SFP+ interfaces make it relevant to organisations using high-speed internet services, data-centre uplinks or campus aggregation. That does not mean every packet flow will automatically achieve a headline rate. Firewall performance is shaped by packet size, connection count, concurrent services, inspection depth, encrypted traffic, VPN overhead and the ability of connected servers or clients to generate and receive traffic. For that reason, the design process should start with application and risk requirements, not simply the fastest interface on the front panel.
The EFG publishes 12.5 Gbps IDS/IPS throughput, one million concurrent sessions and 71,000 new sessions per second. These figures indicate that it is designed for a heavier workload than standard office gateways. In practice, a hotel with thousands of short-lived guest connections, a campus with many mobile devices and a technology company transferring large datasets place different stresses on the gateway. A sizing review should therefore include session behaviour, peak times, inter-VLAN routing, site-to-site encryption, cloud application use and expected inspection policy.
FourTeck can help translate the business environment into a port and policy design. This may involve separating WAN and LAN roles, deciding where 25G is justified, selecting a compatible aggregation switch, reviewing fibre distances, assigning a management path and identifying which services should be enabled at launch. The goal is to avoid buying expensive optics that do not match the connected equipment or enabling every inspection feature without first understanding the operational effect.
Security visibility, filtering and encrypted traffic
The EFG supports a stateful firewall, application-aware Layer 7 controls, deep packet identification, zone-based policy, content filtering, ad blocking and intrusion detection or prevention. These functions can help administrators understand traffic and apply more specific controls than a traditional source-and-destination rule set. For example, a business may separate guest WiFi from corporate services, restrict building systems from reaching user networks, apply different outbound controls to departments and monitor unusual application categories at the perimeter.
Security effectiveness depends on policy quality and ongoing administration. A large signature library does not replace disciplined rule review, endpoint protection, identity management, patching, logging and incident response. The published figure of more than 95,000 IDS/IPS signatures is associated with CyberSecure Enterprise, making subscription status an important procurement question. Buyers should ask which inspection services are included in the base product, which are optional, how updates are delivered and who will monitor alerts after deployment.
SSL/TLS inspection can provide visibility into encrypted sessions, but it introduces certificate and privacy considerations. Managed endpoints may need a trusted inspection certificate. Some applications use certificate pinning or other mechanisms that prevent normal decryption, creating a need for exclusions and testing. Organisations should involve security, legal, application and endpoint-management stakeholders before enabling broad encrypted-traffic inspection. A phased rollout is usually more manageable than activating it across every network at once.
The EFG can become an important control point, but it should be treated as one component of a layered security design. FourTeck can assist with scope clarification, zone planning, migration sequencing and configuration support, while the customer should define acceptable-use policy, data handling requirements, administrator roles and alert-response ownership.
High availability and business continuity planning
A resilient edge requires more than placing two gateways in a rack. The EFG supports Shadow Mode, an active-passive approach based on VRRP, when paired with another EFG and run on a supported UniFi OS release. The standby gateway synchronises relevant state and can assume the gateway role after a primary failure. This reduces the risk that a single appliance fault interrupts all routed connectivity, but it does not eliminate failures elsewhere in the service chain.
A complete design should examine both WAN handoffs, upstream provider equipment, aggregation switches, power sources, rack PDUs, fibre paths and DNS or authentication dependencies. If both EFG units connect through one switch, one power circuit or one ISP device, those elements can remain single points of failure. Dual hot-swappable power supplies in each EFG provide valuable appliance-level resilience, yet they are most effective when connected to separate protected power paths where the facility design allows it.
Failover should be tested during a controlled maintenance window. The test plan may include primary gateway shutdown, loss of a WAN circuit, restoration of service, VPN continuity, dynamic routing convergence, application behaviour and monitoring alerts. Results should be documented, including any sessions that reconnect rather than remain uninterrupted. Organisations with strict continuity targets should also define recovery responsibilities and escalation contacts instead of treating gateway redundancy as a substitute for an operational plan.
When requesting a quotation for high availability, specify that a pair is required and include the desired cabling, modules, power arrangements, installation, configuration and failover validation. This prevents the quotation from covering only two appliances while omitting the design work and accessories needed to make the pair useful.
Management scope and the UniFi application model
The EFG is a UniFi Cloud Gateway, meaning it combines the gateway function with the UniFi Network control plane. This can simplify the architecture for organisations that want one appliance to route traffic and manage compatible UniFi network devices. Administrators can work with topology views, client information, traffic analytics, switch and access-point settings, firewall policy, VPNs and updates through the UniFi management experience.
A key purchasing detail is that the EFG runs UniFi Network only. It does not host UniFi Protect, Access, Talk or other UniFi applications. A business using UniFi cameras may need a UNVR or another appropriate console. Door access, communications or additional applications likewise require a supported hosting platform. This separation can be beneficial in large deployments because it prevents video or application workloads from competing with the gateway, but it must be reflected in the bill of materials.
Administrator access should be designed with the same care as firewall policy. Define named accounts, multi-factor authentication, role separation, backup procedures, update governance and remote-support permissions. Avoid depending on a single shared administrator credential. Decide who approves configuration changes and how emergency access will work if the normal identity path is unavailable.
Before replacing an existing UniFi gateway, compare software versions and backup compatibility. Migration planning should include exports or backups, a record of WAN addressing, DHCP, VLANs, static routes, VPN secrets, custom NAT and firewall rules. A clean implementation can sometimes be safer than importing years of undocumented configuration, but that choice depends on the site and available change window.
Ideal business environments and use cases
Corporate campuses
A campus may have multiple buildings, dense wireless coverage, corporate and guest networks, voice, meeting-room systems and server segments. The EFG can provide a central routing and policy point when the aggregation, redundancy and fibre design support the required scale.
Hospitality properties
Hotels and serviced residences often serve large numbers of transient clients while maintaining separate operational, payment, staff and guest networks. Session capacity, segmentation and internet resilience are important, although captive-portal, compliance and property-system requirements must be reviewed separately.
Education networks
Schools and universities can have high client density, BYOD traffic, labs, administration services and several trust levels. The EFG may support the routing and inspection load, while policy design should reflect safeguarding, privacy, content-control and academic requirements.
Warehouses and logistics sites
Logistics operations may combine handheld scanners, office systems, cameras, wireless infrastructure, automation and partner access. Clear segmentation and dependable WAN failover matter, especially when business processes rely on cloud platforms and real-time inventory systems.
Technology and data-heavy offices
Software, media, design and engineering organisations may use multi-gigabit internet, high-speed storage and many remote connections. The EFG’s interface options are relevant, but users should separate internet-edge requirements from internal data-centre routing decisions.
Managed multi-site environments
Groups operating many branches may use the EFG at a headquarters or regional hub with Site Magic, IPsec or other VPN options. Tunnel scale, routing design, overlapping subnets and support ownership must be assessed before choosing the hub architecture.
Integration and operational considerations
The EFG should be assessed as part of the whole network, not as an isolated appliance. On the WAN side, confirm the provider interface, addressing method, VLAN tags, routing handoff, bandwidth, failover behaviour and whether the carrier supplies a managed router. On the LAN side, identify the aggregation switch, available SFP28 or SFP+ ports, VLAN trunking, link aggregation needs and whether downstream redundancy is required.
Dynamic routing support for OSPF and BGP can help integrate the gateway with more complex networks. The design should define route ownership, redistribution, filtering, preferred paths and failure behaviour. A feature being available does not automatically make it appropriate; a simpler static route may be safer for a small environment, while a campus with redundant cores may benefit from dynamic routing under experienced administration.
Logging and monitoring need explicit ownership. Decide whether UniFi alerts are sufficient for routine operations or whether logs should also be forwarded to a SIEM, syslog platform or managed service. Set retention expectations, create alert thresholds and establish who investigates repeated IPS events, WAN instability or unusual traffic. Without an operational process, visibility can become a large volume of information that nobody reviews.
Power, cooling and rack planning are equally practical. The appliance occupies 1U and has a published maximum consumption of 82W with heat dissipation of 280 BTU per hour. Confirm rack depth, cable bend radius, airflow, UPS capacity, PDU outlets and access for hot-swapping power modules. In a high-availability pair, allow for two units and diverse power connections rather than assuming the second appliance has no facility impact.
Buyer questions to resolve before ordering
What traffic must pass through the EFG?
List internet, inter-VLAN, VPN, public-service and site-to-site flows. The total interface speed alone does not show the inspection and routing workload.
Which security services will be active?
Clarify IDS/IPS, content filtering, application policy, SSL inspection and enhanced signatures because each affects design, licensing and operation.
Is one gateway acceptable?
A single EFG may fit environments with planned downtime tolerance. Critical sites should evaluate a pair, diverse power and upstream redundancy.
What media connects each port?
Specify RJ45, multimode fibre, single-mode fibre or direct-attach cabling, along with distance and speed, so the correct accessories are quoted.
Which UniFi applications are required?
The EFG hosts Network only. Protect, Access, Talk and other application workloads require suitable separate platforms.
Who will manage the environment?
Define administrator roles, update responsibility, alert review, backup checks, policy changes and escalation before the appliance enters production.
Procurement checklist
✓ Confirm exact model EFG and required quantity.
✓ Record primary and secondary WAN speeds and handoff types.
✓ Define whether 25G, 10G or 2.5GbE is required on each link.
✓ Select compatible optics, adapters or direct-attach cables.
✓ Confirm expected UniFi device and connected-user counts.
✓ Identify required VPN protocols and remote-site topology.
✓ Decide whether CyberSecure Enterprise or other subscriptions are needed.
✓ Confirm whether SSL inspection is in scope and how certificates will be deployed.
✓ Include a second EFG when Shadow Mode high availability is required.
✓ Check rack space, power diversity, UPS capacity and cooling.
✓ Define installation, migration, configuration and testing responsibilities.
✓ Confirm current UAE availability, lead time and regional warranty terms.
How FourTeck can assist
FourTeck can help convert the EFG requirement into a clearer bill of materials and implementation scope. The review can begin with the existing topology, internet circuits, connected UniFi estate, client population, security policy and growth plan. From there, the discussion can cover gateway quantity, port allocation, optics, direct-attach cables, high availability, dynamic routing, VPN design, separate UniFi application consoles and installation expectations.
Quotation coordination is more useful when the request includes the practical details. Share the destination, required quantity, preferred delivery timeline, WAN handoffs, uplink distances, switch models and whether configuration or migration support is needed. FourTeck can then identify questions that must be resolved before procurement rather than quoting only the appliance and leaving accessories or dependencies until deployment day.
For wider planning, review FourTeck’s network security product range, explore installation and configuration services, or send the requirement through the FourTeck contact page. Complex projects may also benefit from a wider infrastructure discussion through FourTeck UAE technology solutions.
UAE availability and support guidance
Contact FourTeck to confirm current UAE availability for the Ubiquiti Enterprise Fortress Gateway EFG. Availability may vary according to quantity, regional supply, vendor lead time, requested accessories and whether a single unit or high-availability pair is required. A quotation should identify the exact model, included items, optional cables or transceivers, subscription requirements, warranty guidance and any professional-service scope.
Delivery and project coordination can be discussed after the requirement is confirmed. Installation and configuration should be included explicitly when needed, especially for migrations, dynamic routing, complex VLAN structures, VPN changes, SSL inspection or Shadow Mode testing. FourTeck can coordinate requirements for organisations in Dubai, Abu Dhabi, Sharjah and Ajman through one combined project discussion, avoiding separate city-based specifications that could produce inconsistent bills of materials.
GCC Availability
FourTeck can assist businesses evaluating the EFG for projects across the GCC by reviewing the technical requirement before quotation and delivery planning. A regional project may involve the United Arab Emirates, Saudi Arabia, Kuwait, Qatar, Bahrain or Oman, but the useful starting point is the destination site, not a general country list. Share the exact gateway quantity, whether a high-availability pair is needed, WAN circuit speeds, interface media, accessories, subscription expectations, installation scope and target deployment window. FourTeck can then help coordinate model confirmation, bill-of-material review, configuration planning and commercial follow-up.
Product availability, licensing terms, delivery schedules, service visits, regional power requirements and vendor lead times can differ by country and project. No fixed delivery or installation date should be assumed until the destination, quantity and scope are confirmed. Organisations planning a Kuwait requirement can also review FourTeck Kuwait technology support. For other GCC locations, use the main contact route and include the destination country, deployment address, expected timeline and any onsite or remote-support requirement.
Africa Availability
Organisations planning enterprise UniFi deployments in Africa can ask FourTeck to review the EFG requirement alongside the wider network architecture. The discussion may cover gateway sizing, switch and access-point counts, internet handoffs, fibre modules, high availability, VPN topology, subscriptions, configuration, migration and support expectations. For East African projects, FourTeck resources for Kenya technology requirements and Uganda technology requirements may be relevant, while broader regional enquiries can use the FourTeck Africa project channel.
Availability and fulfilment depend on the destination, product quantity, vendor lead time, power and regulatory conditions, shipping arrangements, licence region, installation scope and local project circumstances. Buyers should provide the country, exact EFG quantity, required modules or cables, preferred deployment schedule and whether remote or onsite assistance is expected. FourTeck can then provide appropriate guidance without assuming local inventory, customs outcomes, fixed delivery timing or country-wide onsite coverage.
Related products, services and alternatives
High-availability EFG pair
Two matching EFG units may be appropriate when gateway hardware redundancy is required. The quotation should also cover cabling, power diversity, topology and failover validation.
25G and 10G connectivity
SFP28 modules, SFP+ modules, RJ45 adapters and direct-attach cables should be selected according to speed, fibre type, distance and connected switch or provider equipment.
UniFi aggregation switching
A compatible aggregation layer may be required to use high-speed gateway uplinks effectively. Port density, redundancy, LACP and optical requirements should be compared separately.
Separate UniFi application consoles
UNVR, CloudKey or other suitable platforms may be needed for Protect, Access, Talk or application workloads because the EFG hosts UniFi Network only.
Installation and migration support
Planning can include configuration review, policy translation, software alignment, controlled cutover, validation and rollback preparation rather than a simple hardware replacement.
Alternative gateway sizing
Smaller UniFi gateways may be more economical where client counts, inspection throughput and interface speeds are lower. Requirements should determine the model rather than portfolio position alone.
Why businesses contact FourTeck
Enterprise gateway purchases often appear simple until the team starts identifying transceivers, provider handoffs, software dependencies, subscriptions, rack requirements, migration risks and operational ownership. FourTeck helps bring those details into the buying conversation. The objective is not to add unnecessary complexity, but to prevent a technically capable appliance from arriving without the components or planning required for a successful deployment.
Businesses may contact FourTeck for model confirmation, topology review, capacity discussion, compatible accessory selection, quotation coordination, installation planning, configuration scope, migration sequencing, high-availability design and support coordination. The final scope can remain product-only when the customer has an experienced internal team, or it can include implementation assistance where additional support is required.
A useful enquiry includes the current gateway model, network diagram, WAN services, switch platform, number of managed UniFi devices, user count, VPN requirements, target security functions and planned change window. Even a simple written summary is enough to begin. FourTeck can then identify which assumptions need confirmation before a commercial proposal is prepared.
Frequently asked questions
Is the EFG suitable for a small office?
It can technically serve a small office, but it is usually evaluated for enterprise-scale networks, high-speed WAN links, large UniFi estates or resilience requirements. A smaller gateway may offer a better cost and complexity fit when inspection throughput, client count and port-speed needs are modest.
Does the Ubiquiti EFG include 25G ports?
Yes. It has two SFP28 interfaces that support 25G, 10G or 1G operation. Correct modules or direct-attach cables are still required, and the connected switch or provider device must support the selected speed and media.
What is the published IDS/IPS throughput?
Ubiquiti publishes 12.5 Gbps IDS/IPS throughput for the EFG. Real performance depends on traffic characteristics, software, enabled services, packet size, connection behaviour and configuration, so buyers should size around actual workloads rather than a single benchmark.
Can two EFG units provide gateway redundancy?
Yes. Shadow Mode supports active-passive failover using VRRP when two matching EFG gateways run a supported UniFi OS version. The complete design should also consider WAN presentation, downstream switching, cabling, power diversity and failover testing.
Does the EFG run UniFi Protect?
No. The EFG runs UniFi Network only. Deployments using UniFi Protect, Access, Talk or other applications require an appropriate separate console or recorder. This should be included in the architecture and bill of materials.
Are security subscriptions required?
Core gateway functions are available without a traditional per-device licence, but some enhanced threat-update or signature capabilities are subscription dependent. Confirm the current CyberSecure Enterprise terms and any other optional services before ordering.
What information is needed for an accurate quote?
Provide quantity, destination, required delivery timeline, WAN speeds, handoff types, uplink distances, switch models, client and UniFi device counts, VPN needs, security features, high-availability requirement and any installation or migration scope.
Can FourTeck help with installation and configuration?
Installation, configuration, migration and testing can be discussed as part of the quotation. Scope varies according to topology, change window, existing configuration, routing, VPNs, inspection policy and whether high availability must be validated.
Is the EFG currently available in Dubai?
Current UAE availability must be confirmed at the time of enquiry. Supply may vary with quantity, regional allocation, accessories and vendor lead time. FourTeck can coordinate a quotation after the exact requirement is provided.
Confirm whether the EFG fits your network edge
Send FourTeck your WAN speeds, UniFi device count, user estimate, preferred uplinks, security requirements and redundancy expectations. The response can cover product quantity, accessories, configuration scope and current UAE availability.

Reviews
There are no reviews yet.