
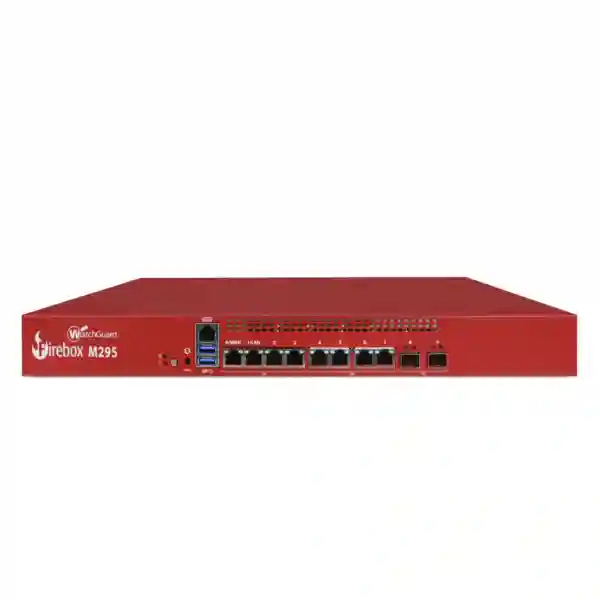
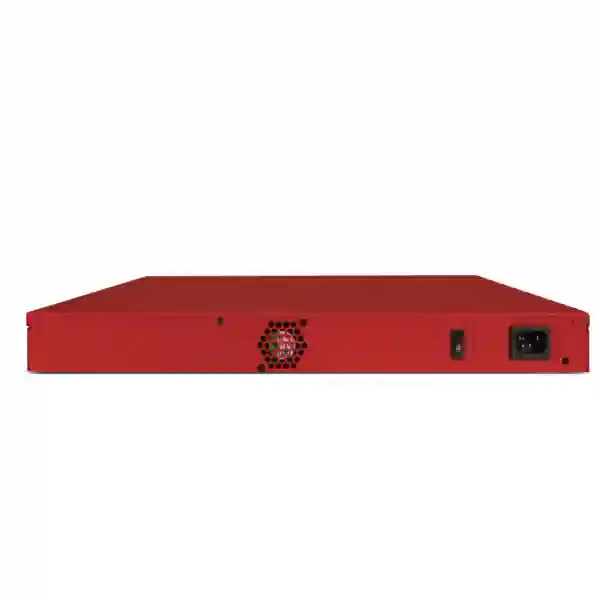
WatchGuard Firebox M295 Dubai
The WatchGuard Firebox M295 is built for small sites, remote offices and growing organizations that need a rackmount security gateway with flexible copper and fiber connectivity. It combines 4 × 1GbE RJ45, 4 × 2.5GbE RJ45 and 2 × 10Gb SFP+/SFP interfaces with WatchGuard Fireware, local or WatchGuard Cloud management options, VPN, traffic control and subscription-based security services. FourTeck can help buyers review whether the M295 matches their real internet bandwidth, encrypted-traffic inspection, VLAN design, branch VPN requirements, rack environment and security-service expectations before an order is placed.
Vendor-published throughput is measured under defined test conditions. Real performance varies with traffic mix, enabled services, policy complexity, encryption and software release.
Direct answer: who should consider the WatchGuard Firebox M295?
The M295 is most relevant to organizations that want a rackmount WatchGuard firewall for a small headquarters, larger branch, remote office, managed customer site or distributed network location where desktop-class connectivity is no longer enough. It offers a useful mixture of Gigabit, 2.5 Gigabit and 10 Gigabit SFP+ interfaces, making it easier to combine ordinary access links with faster switching or fiber uplinks. WatchGuard positions the model for small sites and remote offices, and the published UTM and HTTPS-inspection numbers make it important to size against inspected traffic rather than relying only on the higher raw firewall figure.
Buyers should treat the appliance, security package, support term, optics, rack cabling and deployment service as one solution. Some security capabilities depend on the selected WatchGuard subscription and management design. FourTeck can help turn a product-name request into a practical bill-of-material discussion by checking WAN speed, expected growth, VPN use, number of network zones, SFP+ requirements, remote users, logging expectations and whether the site is replacing another firewall.
WatchGuard Firebox M295 verified specifications
Interfaces
4 × 1GbE RJ45, 4 × 2.5GbE RJ45 and 2 × 10Gb SFP+/SFP ports. The appliance also provides an RJ45 serial console and two USB-A interfaces.
Compute and storage
Intel quad-core x7405C at 2.2 GHz, 8 GB DDR4 memory and 16 GB eMMC storage are listed in WatchGuard’s current hardware guide.
Form factor
Approximately 438 mm deep × 320 mm wide × 44 mm high, with a published weight of 3.5 kg. Rack-ear brackets are included for rack installation.
Management
The Firebox can be locally managed with Fireware Web UI or WatchGuard System Manager, or managed through WatchGuard Cloud depending on the chosen deployment approach.
Important procurement note: power-cord requirements, compatible transceivers, security-service entitlements and support packages should be confirmed for the destination and final quotation. Do not assume that an appliance-only price includes every security service or accessory.
Performance planning matters more than the headline firewall number
WatchGuard publishes 7.90 Gbps raw firewall throughput for the M295 using large UDP frames, but a business buying a next-generation firewall normally enables inspection features. The more decision-useful figures are therefore the published 1.85 Gbps UTM full-scan throughput, 1.12 Gbps HTTPS throughput with IPS enabled and 1.80 Gbps VPN IMIX result. These values are still laboratory measurements, not guaranteed production speeds. Encrypted traffic percentage, packet size, number of concurrent sessions, security services, logging, policy design, VPN encryption, firmware version and the behavior of real applications all influence results.
A sensible sizing conversation therefore starts with the fastest current WAN circuit and the fastest realistic circuit expected during the appliance lifecycle. Add the expected percentage of HTTPS traffic, branch VPN traffic, remote-access users, public-facing services, guest Wi-Fi, cloud applications and internal segmentation traffic that may traverse the firewall. If the requirement sits close to the M295’s inspected-traffic envelope, it can be prudent to review a larger model rather than buying with no margin. FourTeck’s Firewall Dubai solution portal provides a broader starting point for model and architecture discussions.
Before requesting a WatchGuard Firebox M295 quotation
Prepare the user count, internet circuit speed, expected growth, number of WAN links, branch sites, remote users, VLANs, public servers, cloud applications, current firewall model and desired security services. If fiber connectivity is required, identify the switch or carrier handoff and the exact optic type rather than assuming any SFP+ transceiver will work. Also state whether the project needs migration, policy cleanup, VPN recreation, rack installation, configuration documentation or post-cutover support.
For organizations replacing an older device, the most useful input is a sanitized summary of current interfaces, routing, NAT, VPNs, objects and firewall policies. A replacement should not simply reproduce years of obsolete rules. Reviewing purpose, owner and usage before migration can reduce unnecessary exposure and make the new Firebox easier to support.
WatchGuard Firebox M295 Dubai
Customers searching for WatchGuard Firebox M295 Dubai typically want three things answered quickly: whether the model can handle their inspected internet traffic, which license or security package is appropriate, and what is required to deploy it without interrupting the office. Dubai networks can range from a single office using cloud applications to multi-floor environments with guest Wi-Fi, IP telephony, CCTV, servers, remote users and branch connections. The M295 can fit a small headquarters or larger branch when its published performance and interface mix align with the real design. Its four 2.5GbE copper ports are useful where the switching layer or internet service exceeds ordinary Gigabit speeds, while the two 10Gb SFP+ ports can support faster uplinks when compatible transceivers and switching are selected.
For a Dubai deployment, the sizing review should focus on HTTPS inspection because modern business traffic is heavily encrypted. A company may have a 1 Gbps or faster ISP circuit yet see lower usable throughput when multiple security services inspect encrypted sessions. That is why a quote should not be based only on the M295’s 7.9 Gbps firewall figure. The 1.12 Gbps vendor-published HTTPS figure with IPS enabled and the 1.85 Gbps UTM full-scan result provide more relevant reference points for security-enabled planning. Real traffic will differ, so organizations with demanding decryption or rapid growth should leave operating margin.
Dubai buyers should also define branch and remote-access needs. A construction company may need encrypted links to project offices; a retail group may need repeatable branch policy; a professional-services firm may prioritize remote access and segmented guest Wi-Fi; a warehouse may need controlled access for scanners, CCTV and operational systems. The same M295 can support different architectures, but the policy set, subscription, logs and support plan should reflect the business rather than a generic template.
FourTeck can assist with a WatchGuard M295 Dubai quotation that separates appliance, security subscriptions, support, compatible optics and deployment services. Buyers can also review the firewall deployment and support services available for planning, migration, VPN configuration and policy review. Availability and commercial terms should always be confirmed at the time of inquiry rather than assumed from old online listings.
WatchGuard Firebox M295 UAE
A WatchGuard Firebox M295 UAE requirement often involves more than one site. An organization may operate a headquarters in Dubai or Abu Dhabi with branches in Sharjah, Ajman or other emirates, while staff access cloud platforms and internal resources from multiple locations. The M295 is particularly relevant when a branch or compact headquarters needs rackmount hardware, mixed copper and fiber interfaces and centralized administration. Its ability to be managed locally or through WatchGuard Cloud gives IT teams a choice in how they organize operations, but the management model should be decided before rollout so templates, logging, administration and change processes remain consistent.
UAE procurement teams should specify the intended security outcome. If the priority is basic routing and stateful firewalling, a raw throughput number may appear generous. If the requirement includes encrypted-traffic inspection, intrusion prevention, application control and malware scanning, security-enabled throughput becomes the more relevant measure. A solution review should therefore consider the number of active users, the traffic profile at peak periods, site-to-site tunnels, remote VPN sessions, software-as-a-service usage and any published servers or DMZ services. Where an organization plans to increase internet bandwidth during the next refresh cycle, that future bandwidth should be included in the sizing calculation now.
Interface planning is another UAE buying concern. The M295 provides four 1GbE copper, four 2.5GbE copper and two SFP+ interfaces capable of 10Gb operation with supported transceivers. This mix can help when the carrier handoff, distribution switch or server network uses different speeds. However, the presence of a port does not automatically guarantee compatibility with every optic or cabling design. The bill of materials should identify required transceivers, patching, rack position, power arrangement and any switch changes.
For multi-emirate projects, define a standard naming and policy convention before deployment. Consistent interface labels, VPN objects, network zones, backup procedures and administrator roles reduce support time later. FourTeck can help coordinate a UAE-focused sizing and migration discussion through its business firewall product catalogue and quotation process without making unsupported promises about stock or delivery dates.
WatchGuard Firebox M295 Uganda
Organizations researching WatchGuard Firebox M295 Uganda are often balancing central-office security with connectivity to branches, field locations and cloud services. The M295 can be considered for a head office or important regional site where a rackmount firewall is preferred and the network benefits from a mixture of 1GbE, 2.5GbE and 10Gb SFP+ connectivity. A buyer should begin by mapping how much traffic actually crosses the perimeter: ordinary internet access, Microsoft 365 or other cloud applications, VPN traffic, remote administration, web-based business systems, voice services, surveillance access and communications with other offices.
Connectivity resilience deserves specific attention in Uganda. Where a business uses more than one ISP or combines fixed and backup connectivity, the firewall design should document failover behavior, routing priorities, DNS dependencies and which services must remain reachable during an outage. The M295 should be sized for the busiest realistic link, not only the normal average. If the organization uses encrypted site-to-site VPNs between Kampala and regional branches, VPN throughput and tunnel design should be evaluated alongside internet inspection. A well-designed rule base can limit each branch to the applications and subnets it needs rather than creating broad network access simply because sites are connected.
Power quality and installation conditions should also be considered. WatchGuard’s hardware guidance calls for indoor installation in a secure area and conditioned power. For procurement, include the rack, UPS strategy, cable management, environmental conditions and correct regional power cord in the project checklist. The M295’s compact 1U height does not remove the need for ventilation and secure physical access.
Uganda buyers can use the FourTeck Uganda platform for regional technology enquiries while the Firewall Dubai team can help structure the M295 technical requirement. Ask for a quotation that clearly identifies appliance hardware, subscription term, support, optics and any installation or migration service. This keeps the comparison focused on the full deployed solution instead of an incomplete appliance-only price.
WatchGuard Firebox M295 Kampala
A WatchGuard Firebox M295 Kampala deployment is commonly relevant to organizations that concentrate users, servers or administrative systems in one city location and connect outward to remote offices. The correct design depends on what the Kampala site represents: headquarters, data-processing location, branch hub, education campus, service center, warehouse or a shared office. If the location is the hub for multiple tunnels, the firewall must be sized for aggregate encrypted traffic as well as ordinary internet use. Peak use matters more than an average bandwidth number because backup jobs, video meetings, cloud synchronization and software updates can all coincide.
The M295’s 2.5GbE copper and 10Gb SFP+ options can be useful when a Kampala office is upgrading its switching infrastructure or needs a fiber uplink to a core switch. Before specifying SFP+, confirm the supported optic, fiber type and distance. If a service provider hands off connectivity on copper, identify whether the port needs 1GbE or multi-gigabit capability. Documenting this before purchase prevents a technically capable firewall from being delayed by missing optics, incompatible cabling or an unplanned switch dependency.
Policy design should reflect local operational roles. Guest Wi-Fi should not automatically share trust with finance, management, servers, voice systems or building devices. Remote administrators should have controlled management access rather than open interfaces. Site-to-site tunnels should use explicit network definitions and logging. If HTTPS inspection is planned, application compatibility and certificate deployment should be tested so security does not break critical business portals. Because WatchGuard publishes a 1.12 Gbps HTTPS throughput reference for the M295 under its defined test, encrypted inspection should be included in the sizing conversation from the beginning.
For procurement, provide the Kampala site address at quotation stage, but avoid assuming stock, local warehouse presence or a fixed delivery time until confirmed. A useful request includes user count, internet speed, branch count, remote VPN requirement, current firewall, preferred subscription term and whether configuration support is needed. FourTeck can then help turn the WatchGuard M295 Kampala search into a more accurate technical and commercial scope.
WatchGuard Firebox M295 Arua
For buyers searching WatchGuard Firebox M295 Arua, the most important question is usually not whether the model can sit in a rack, but whether the complete design suits a regional site that may depend heavily on WAN links back to a larger office. A branch firewall should continue to protect local internet use while also providing controlled access to central applications. The M295’s multi-gigabit and SFP+ interfaces may provide more interface capacity than a smaller branch needs today, but that headroom can be useful where the site is intended to grow, aggregate several network segments or act as a secure communications hub.
Arua deployments should document what must happen when the primary WAN is unavailable. If a secondary connection exists, define which traffic is allowed to fail over and whether business-critical VPNs, cloud applications, voice or remote management receive priority. If only one WAN is available, local continuity procedures become even more important. The firewall cannot compensate for an unavailable circuit, so buyers should distinguish firewall resilience from carrier resilience when planning the project.
Network segmentation can add value even in a regional office. Staff systems, guest Wi-Fi, CCTV, printers, voice devices, administrative equipment and any locally hosted server do not need unrestricted communication. Building zones and policies around real business relationships reduces the number of pathways an attacker or compromised endpoint can use. The Firebox can enforce these rules, while logs provide a useful trail for troubleshooting. If the site communicates with Kampala or another central location, use narrowly defined tunnel policies and keep a clear inventory of networks on both sides.
Physical deployment is equally practical. Plan rack space, secure access, conditioned power, UPS capacity, patch leads and the correct transceivers. WatchGuard lists the M295 operating range at 0°C to 40°C, so the network room should provide suitable environmental conditions. For an Arua quote, ask FourTeck to separate hardware, license package, support term, optics and optional configuration work so procurement can compare a complete project rather than a single line-item price.
WatchGuard Firebox M295 Mbarara
A WatchGuard Firebox M295 Mbarara project may serve a regional office that links employees, cloud services, branch systems and remote users. The appliance can be appropriate where the site needs a rackmount platform and enough interface flexibility to support multiple internal networks or faster uplinks. Buyers should first decide whether the firewall will be a simple internet edge, a VPN hub, an inter-VLAN security gateway, or a combination of these roles. Each role changes the traffic profile and therefore the sizing decision.
If the Mbarara office has several departments, traffic should be separated according to function. Finance and administration may require access to systems that guest Wi-Fi or operational devices do not. CCTV may need remote viewing without broad access to user networks. Printers and shared devices can be placed in controlled segments. A thoughtful rule set allows required communication and blocks unnecessary paths. This is more useful than creating one trusted LAN simply because it is easier during installation.
The performance plan should include encrypted web traffic and VPN. The M295 is marketed for small sites and remote offices, but the words “small site” do not define workload. A location with fewer users can still generate heavy traffic through cloud backup, video, large file transfers or branch synchronization. Use measured WAN data where possible, identify peak periods and compare those figures with WatchGuard’s inspected-traffic results rather than raw firewall throughput. If the business plans to upgrade its ISP link or add another office, include that future requirement in the current sizing conversation.
For an accurate WatchGuard M295 Mbarara quotation, include the intended security package, support duration, required fiber or copper handoffs, VPN count, rack requirements and whether the project needs migration from an existing firewall. FourTeck can assist with a structured procurement discussion, but actual product availability and logistics should be confirmed when the order is ready. This approach avoids unsupported assumptions and gives the technical team a clearer basis for deployment.
WatchGuard Firebox M295 Gulu
Customers evaluating WatchGuard Firebox M295 Gulu often need dependable security at a location that may be part of a wider organization. The M295 can function as the secure edge for local internet, branch VPNs, remote access and segmented internal networks, but the design should account for the realities of the site. Start with the applications users actually depend on, where those applications are hosted and how much traffic must traverse links to other offices. Cloud-first sites require different policies from sites that frequently reach central servers over VPN.
Bandwidth efficiency is a useful planning topic. Security inspection is valuable, but every enabled service consumes resources and some applications are more latency-sensitive than others. Define which traffic requires deep inspection, which business destinations need special handling and how bandwidth should be prioritized during busy periods. The M295’s published performance provides a planning reference, but the final experience depends on the WAN service and real traffic mix. If a secondary connection is available, document failover rules and test them instead of assuming that a configured backup path will behave correctly during a real outage.
For internal architecture, keep management interfaces restricted and create separate zones for guest, staff, servers and operational devices where appropriate. If cameras, access-control devices or other networked equipment are present, limit their reach to only the systems they require. For VPNs back to Kampala or another site, use descriptive tunnel names and keep the network list current. Documentation should include public IPs, local subnets, routes, tunnel peers, important policies, administrator access and backup procedures.
A Gulu procurement request should also identify physical needs: rack position, power protection, cable type and any SFP+ modules. The M295 uses a 1U form factor and WatchGuard recommends indoor, secure installation with conditioned power. FourTeck can help scope the model, subscription and service components for Gulu without implying a local warehouse, guaranteed stock or fixed delivery time until those details are verified for the transaction.
WatchGuard Firebox M295 Kenya
A WatchGuard Firebox M295 Kenya search often comes from organizations comparing firewall options for Nairobi headquarters, regional branches, logistics facilities, professional offices, education sites or distributed operations. The M295 can be considered where a site needs rackmount deployment and mixed interface speeds, including 2.5GbE copper and 10Gb SFP+. The most important buying step is to translate business usage into a traffic profile. User count alone is not enough: a smaller site using video collaboration, cloud backup, hosted ERP and encrypted branch links can place more load on a firewall than a larger office with lighter applications.
Kenyan multi-site networks should decide whether internet access is local at each branch or centralized through a hub. Local breakout can reduce backhaul demand but requires consistent security policy at each location. Centralized internet access simplifies some controls but increases VPN and hub capacity requirements. If the M295 is intended as the hub, calculate aggregate branch traffic and remote user traffic. If it is a branch appliance, evaluate local inspection, tunnel overhead and growth. WatchGuard Cloud management may help teams maintain common policies across devices, while local management remains an option for organizations that prefer that operational model.
ISP diversity and failover are also worth documenting. Where two providers are available, define routing priorities and business-critical services. Test public services, DNS behavior and VPN recovery after a link switch. For fiber handoffs, match transceivers and fiber type with both the firewall and adjacent switch. For copper handoffs above 1 Gbps, confirm the exact port and speed negotiation needed. These details are small compared with the cost of the firewall but can determine whether installation works on the planned date.
FourTeck’s Kenya technology platform can support regional enquiries, while the firewall team can help define M295 sizing, licensing, optics and deployment requirements. Ask for current availability and commercial terms rather than relying on pricing from another country, an old search result or an appliance listing that excludes the necessary security subscription.
WatchGuard Firebox M295 Kuwait
Organizations looking for WatchGuard Firebox M295 Kuwait may be securing a compact headquarters, a branch, a retail or service environment, or a business with several locations connected by VPN. The M295 provides a rackmount option with a versatile interface layout that can accommodate ordinary Gigabit connections, 2.5GbE copper links and 10Gb SFP+ uplinks. For a Kuwait deployment, interface flexibility is useful only when it is matched to the actual carrier handoff and switching design, so the quote request should state whether WAN and LAN connections are copper or fiber and the required speeds.
Encrypted application traffic should drive capacity planning. Business users increasingly access Microsoft 365, cloud storage, web ERP, banking portals, SaaS tools and video platforms over HTTPS. When inspection is enabled, the firewall performs more work than simple packet forwarding. WatchGuard’s published HTTPS and UTM figures are therefore more relevant to a security-enabled design than the raw firewall figure. Buyers expecting a high percentage of TLS inspection should also plan certificate deployment, exception policies and testing for applications that do not tolerate decryption.
For organizations with several Kuwait sites, create a consistent branch standard. Define VLAN numbering, object naming, tunnel names, administrator roles, logging, backup intervals and change approval. A consistent standard reduces configuration drift and makes troubleshooting easier when an employee reports that one site can reach an application and another cannot. If the M295 is replacing a different vendor, use the migration to clean obsolete rules rather than translating every entry automatically.
The commercial request should identify appliance, chosen WatchGuard security package, support duration, transceivers and any configuration or migration services. Avoid assuming that an online “WatchGuard M295 price Kuwait” includes the same entitlements as another quote. Security features can depend on the package and term. FourTeck can help build a comparable bill of materials and clarify what is included before procurement approval.
WatchGuard Firebox M295 Ghana
A WatchGuard Firebox M295 Ghana requirement may come from a head office, regional branch, service company, school, logistics organization or professional business that needs stronger perimeter security and reliable VPN connectivity. The M295 is best evaluated as part of the network architecture rather than as an isolated appliance. Map internet links, internal VLANs, branch tunnels, remote users, public services and cloud applications first. This shows whether the firewall will mainly inspect north-south internet traffic or also carry significant internal segmentation and inter-site traffic.
For a Ghana deployment, network teams should plan link resilience and power protection explicitly. A firewall can provide policy control and path selection, but business continuity depends on the entire chain: carrier links, modem or handoff equipment, switching, DNS, UPS, rack conditions and configuration backups. WatchGuard recommends a secure indoor location and conditioned power. These requirements belong in the project scope because a well-sized security appliance still cannot deliver dependable service if its installation environment is unstable.
The M295’s interface mix gives flexibility for growth. Four 2.5GbE copper ports can connect to multi-gigabit switches or faster handoffs, while two SFP+ interfaces can be used for supported fiber or DAC scenarios. Confirm the exact transceiver and adjacent device before purchase. On the logical side, create separate zones for staff, guest access, servers and operational devices where appropriate. Enable only the communication paths that the business needs, and log important policy decisions so future support teams understand why a rule exists.
When requesting a WatchGuard M295 Ghana quote, state the subscription term, security services, user count, WAN bandwidth, VPN requirements and deployment assistance needed. If the organization operates multiple regions, identify where centralized management and logging will live. FourTeck can help with product selection and project coordination, while availability, warranty path and logistics should be confirmed for the specific order instead of inferred from another market.
WatchGuard Firebox M295 Nigeria
Businesses researching WatchGuard Firebox M295 Nigeria may be planning for a busy Lagos office, an Abuja location, a regional branch or a distributed environment with multiple providers and cloud-heavy traffic. The M295 offers a strong interface mix for a small rackmount firewall, but suitability should be measured against inspected throughput, session behavior and VPN use. A branch with 100 users is not automatically a better fit than a branch with 60; the decisive factors are what those users do, the speed of the WAN, how much traffic is encrypted and which security services are enabled.
For sites using two internet providers, define failure behavior in advance. Which circuit is primary? Should all traffic move to backup, or only selected business applications? Do site-to-site VPNs re-establish automatically over the alternate path? Are public DNS records or hosted services affected? A written failover design prevents the firewall from becoming the only documented part of a much larger continuity problem. Where remote offices connect to a central Nigeria hub, aggregate VPN traffic should be included in the hub sizing calculation.
Encrypted inspection deserves a separate policy conversation. The M295’s published HTTPS performance is lower than its raw firewall throughput because decryption and inspection add work. Decide whether all eligible traffic will be inspected, which categories require exclusions and how internal devices will trust the inspection certificate. Test finance, banking, healthcare, mobile applications and any pinned-certificate applications before broad deployment. Logging and retention requirements should also be decided because they affect the operational design even when they do not change the firewall’s physical ports.
For a Nigerian procurement team, a useful request lists the current firewall, user count, WAN speeds, branch locations, remote users, security-service expectations, support term and required accessories. Ask the supplier to distinguish the base appliance from subscription and service components. FourTeck can assist with requirement review and regional project discussions, while stock, lead time, delivery and warranty routing should be confirmed in writing for the specific destination and order date.
WatchGuard Firebox M295 Seychelles
A WatchGuard Firebox M295 Seychelles deployment may serve a hospitality business, professional office, government-related environment, service provider customer, retail operation or multi-site organization that depends heavily on reliable internet access. Because island connectivity and logistics can make replacement planning important, buyers should consider not only firewall performance but also support process, configuration backups, spare strategy and the time required to source accessories. The M295’s rackmount design and flexible port set can suit a central site where multiple internal networks and faster uplinks are required.
Bandwidth should be measured carefully. If the site has a high-speed internet service, compare that speed with WatchGuard’s UTM and HTTPS-inspection results instead of the raw 7.9 Gbps firewall figure. If the WAN is lower bandwidth but highly critical, the emphasis may shift toward resilience, policy quality and secure remote administration rather than peak throughput. For organizations serving guest users, separate guest access from business systems and management networks. Hospitality environments in particular should avoid treating guest devices as trusted simply because they share the same physical site.
Remote support should be planned securely. Limit firewall management to approved administrators and networks, use strong authentication practices and keep firmware and configuration backups under a controlled process. If off-island technical staff need access, define exactly what management services are reachable and from where. For site-to-site VPNs, document peer addresses, protected networks and recovery steps. If the business relies on cloud applications, include DNS and internet-failover behavior in continuity testing.
The quotation should also confirm the correct power cord, supported SFP/SFP+ optics and delivery logistics. These are practical details that become especially important when equipment is not sourced locally. FourTeck can help structure the M295 specification, subscription and deployment scope for Seychelles buyers without making assumptions about immediate stock or fixed lead times. A complete written bill of materials is the best basis for comparing suppliers and planning installation.
Security services, licensing and management choices
WatchGuard sells Firebox security in packages rather than treating every capability as permanently included with the appliance. The exact bundle names, features and terms can change, so the safest procurement method is to request the current package comparison for the M295 at quotation time. Define which outcomes matter: intrusion prevention, gateway anti-malware, web or DNS protection, application visibility, sandboxing, endpoint integration, cloud logging, support entitlement and other services. Do not assume that two M295 quotes are equivalent simply because the hardware model is identical.
Management is also a design choice. WatchGuard documentation states that the Firebox can be managed locally with Fireware Web UI or WatchGuard System Manager, or through WatchGuard Cloud. Cloud management can be useful for distributed fleets and centralized templates, while locally managed deployments may be preferred where teams already operate that way or require specific configuration practices. The choice should consider administrator workflow, logging, change control, support responsibilities and how many Fireboxes will be managed together.
Firmware planning should be included in operational handover. A new firewall project is not complete when traffic starts flowing. Record the installed Fireware version, backup configuration, administrator roles, update process, maintenance window and recovery plan. WatchGuard continues to publish software updates for the M295 family, so long-term ownership should include a process for reviewing release notes and applying supported firmware rather than leaving the device on its launch version indefinitely.
Deployment and migration checklist
1. Discover
Document WAN circuits, public IPs, LANs, VLANs, switches, servers, Wi-Fi, voice, cameras, branches, remote users and cloud dependencies.
2. Size
Compare real and future bandwidth with security-enabled throughput. Include TLS inspection, VPN traffic, peak sessions and future growth.
3. Build the bill of materials
Specify the appliance, security package, support term, optics, cables, power cord and any rack or switching accessories that are genuinely required.
4. Design policy
Define zones, routing, NAT, VPN, allowed applications, guest isolation, management access, logging, web controls and exception processes before cutover.
5. Test migration
Validate critical applications, internet access, public services, site-to-site VPNs, remote users, DNS, printing and voice. Keep a rollback path for the change window.
6. Hand over
Store configuration backups, record administrator ownership, document important policies, define firmware review and confirm who handles future security changes.
Frequently asked questions about the WatchGuard Firebox M295
What is the WatchGuard Firebox M295 designed for?
WatchGuard positions the M295 for small sites and remote offices that need enterprise-grade security services in a rackmount platform. It is also relevant to smaller headquarters when its inspected throughput, interfaces and management model fit the requirement.
How many network interfaces does the M295 have?
The current WatchGuard hardware guide lists four 1GbE RJ45 interfaces, four 2.5GbE RJ45 interfaces and two SFP+/SFP interfaces capable of 10Gb with supported transceivers. It also has an RJ45 serial console and two USB-A interfaces.
What throughput should I use for sizing?
Do not size only from the 7.90 Gbps raw firewall figure. WatchGuard also publishes 1.85 Gbps UTM full-scan, 1.12 Gbps HTTPS with IPS enabled and 1.80 Gbps VPN IMIX results. Real-world performance varies, so use the metric that resembles your intended security workload and leave margin.
Can the M295 be managed through WatchGuard Cloud?
Yes. WatchGuard documents both cloud-managed and locally managed approaches. The correct choice depends on operational requirements, existing WatchGuard practices, logging, administrator workflow and fleet size.
Does an M295 appliance quote include every security service?
Not necessarily. WatchGuard security capabilities are packaged with subscriptions and support options. Ask the supplier to list the exact hardware, security package, term, support and accessories so quotes can be compared correctly.
Can FourTeck help migrate an existing firewall to the M295?
FourTeck can discuss migration scope including interface mapping, policy review, routing, NAT, VPN recreation, testing and documentation. The exact work depends on the source firewall, configuration quality and agreed project scope.
Decision recap: is the M295 the right size?
Strong reasons to evaluate it
You need a 1U WatchGuard firewall, want mixed 1GbE/2.5GbE/10Gb SFP+ connectivity, require centralized or local management options, and your security-enabled traffic fits comfortably within the M295’s published performance with growth margin.
Reasons to review a larger model
Your inspected internet demand approaches the M295’s UTM or HTTPS reference figures, the site is a heavy VPN hub, you need more high-speed interfaces, or forecast traffic growth could consume the available performance margin during the intended lifecycle.
Quotation checklist for WatchGuard Firebox M295
Providing these details lets the sales and technical teams prepare a more accurate recommendation. For related models or alternative firewall platforms, review FourTeck’s firewall product range before finalizing the bill of materials.
Talk to FourTeck about the WatchGuard Firebox M295
Share your country, site type, internet bandwidth, user count, VPN requirements, current firewall and expected security services. FourTeck can help review whether the M295 is appropriately sized, identify the subscription and accessories that should be quoted, and discuss installation or migration needs. Current stock, commercial terms, delivery arrangements and warranty routing should be confirmed in the final quotation.
For broader planning around perimeter security, VPN, segmentation and migration, start with FourTeck’s firewall resources and support team rather than selecting a model on price alone. A firewall is most useful when the hardware, security license and configuration are designed as one working system.


Reviews
There are no reviews yet.