
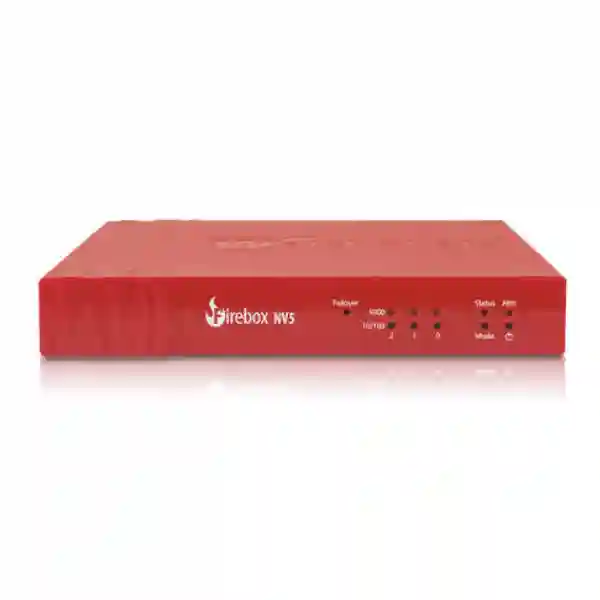
WatchGuard Firebox NV5 Dubai
The WatchGuard Firebox NV5 is a compact VPN gateway built for distributed sites that need secure connectivity to a corporate office or data centre without deploying a larger full-featured security appliance at every edge location. Typical uses include kiosks, ATMs, unattended equipment, remote offices and small operational sites. For Dubai and UAE projects, the NV5 is especially relevant when the requirement is controlled branch-to-head-office connectivity, centrally managed configuration, a small physical footprint and a repeatable rollout model.
Direct buyer answer
Choose the Firebox NV5 when the main job is secure edge connectivity and BOVPN for a remote site or device. Do not treat it as a general replacement for a larger Firebox that must run subscription security services, FireCluster, load balancing or link aggregation. Confirm the final architecture before ordering.
Primary Role
Secure VPN gateway for remote workers, small offices and remote devices connecting to a corporate Firebox environment.
Connectivity
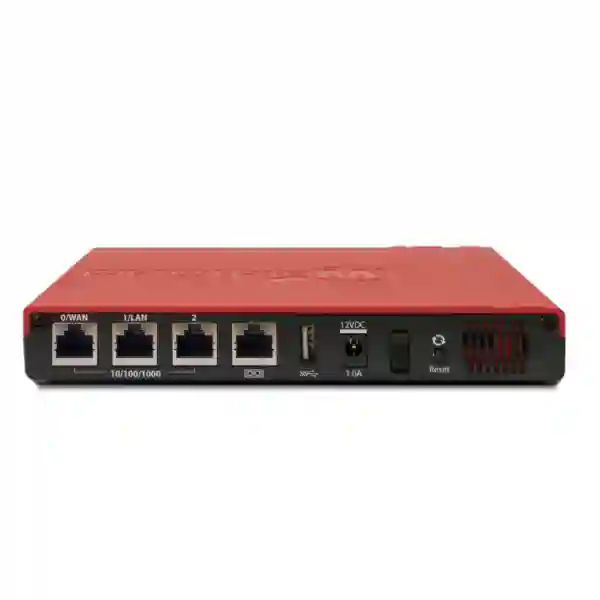
Three 1000Base-TX RJ45 network interfaces, plus USB 3.0 and an RJ45 serial port for supported operational needs.
Management
WatchGuard Cloud can support centralized deployment and management, including repeatable configuration for distributed sites.
Important Limit
The NV5 is intended as a VPN gateway with Standard Support and does not support Firebox subscription security services.
What the WatchGuard Firebox NV5 Is Designed to Do
The Firebox NV5 is best understood as a specialised edge-connectivity appliance rather than a small version of every other WatchGuard firewall. WatchGuard positions it for remote applications such as kiosks, ATMs and remote office equipment that need secure connectivity to a Firebox environment. It can establish Branch Office VPN connectivity and participate in an architecture where traffic is securely transported toward a larger corporate Firebox or data-centre security gateway. This makes the NV5 useful for organisations that have many physically separated locations but do not need a full local UTM stack at each site.
For a Dubai business, this distinction matters during procurement. A buyer searching for a “WatchGuard NV5 firewall” may assume the appliance should provide the same subscription security services found on broader Firebox platforms. The NV5 does not support Firebox subscription security services. It also does not support FireCluster, server load balancing or link aggregation. The right question is therefore not only whether the appliance can pass traffic; it is whether the intended branch architecture matches the NV5 purpose. If the remote site needs local advanced inspection, full security subscriptions, high-availability clustering or broader local edge functions, another Firebox model may be more appropriate.
Where the NV5 fits, its simplicity is valuable. The compact hardware, WatchGuard Cloud capability, SD-WAN routing support and BOVPN workflow can help IT teams standardise remote connectivity. A centrally prepared configuration can reduce manual work at each location, while a consistent branch template can help control addressing, VPN settings, policy structure and support procedures. FourTeck can review the number of sites, ISP handoff, expected traffic, head-office Firebox model, routing requirements and operational ownership before the commercial quotation is finalised.
Verified Firebox NV5 Hardware Details
| Item | WatchGuard NV5 specification | Buyer relevance |
|---|---|---|
| Processor | NXP LS1012A, 1 GHz | Purpose-built for the NV5 edge gateway role; do not size only from CPU naming. |
| Memory | 1 GB DDR3L | Supports the appliance design; capacity planning should focus on supported deployment purpose. |
| Storage | 4 GB eMMC | Compact embedded storage suited to the appliance platform. |
| Network interfaces | 3 x 1000Base-TX RJ45 | Useful for WAN/LAN and branch topology planning; confirm actual interface mapping before installation. |
| I/O | 1 x USB 3.0, 1 x RJ45 serial port | Relevant for supported modem or service scenarios and local administration requirements. |
| Dimensions | 190 x 152 x 32 mm | Small tabletop footprint for compact remote locations. |
| Weight | 0.285 kg | Lightweight for edge deployments where rack space is not available. |
| Power supply output | 12 V, 1 A, 12 W | Confirm clean, conditioned power and installation environment at each remote site. |
| Platform security | TPM included | Used for secure WatchGuard Cloud registration of the device. |
Specifications should be reconfirmed against the current manufacturer documentation and the exact bill of materials at quotation time. Product availability, regional power accessories, support entitlement and firmware eligibility can vary with order timing and channel.
Key Benefits for Distributed Branch and Edge Networks
Branch Office VPN
BOVPN lets the NV5 form secure site-to-site connectivity with the wider WatchGuard environment. This is useful for a branch that needs access to ERP, file services, central applications, monitoring systems or management resources without exposing those services directly to the public internet.
Cloud-Based Rollout
WatchGuard Cloud can support centrally managed deployment. For organisations opening or maintaining many similar remote sites, pre-planned templates and controlled onboarding can reduce configuration variation and make support handover more consistent.
SD-WAN Routing
The NV5 supports SD-WAN routing capabilities that can be used within a correctly designed WatchGuard network. Path selection and failover objectives should be mapped to the actual links, latency sensitivity and service priorities of each remote site.
Compact Remote Placement
At 190 x 152 x 32 mm, the NV5 fits locations where a full rack appliance is unnecessary. Installation still needs suitable indoor placement, reliable power, secure physical access and correct cabling.
Important Licensing and Feature Boundaries
The Firebox NV5 is intended as a secure VPN gateway with a Standard Support license. WatchGuard documentation states that it does not support Firebox subscription security services, FireCluster, load balancing or link aggregation. These boundaries are central to model selection. A procurement team should not buy an NV5 assuming it will later be upgraded into a full local UTM platform through the same subscription bundle used on larger Firebox appliances.
A good NV5 design normally starts by defining where security inspection and internet breakout will occur, what traffic must traverse the BOVPN, whether direct internet traffic is allowed, how branch routes are handled, whether a secondary WAN or supported modem is required, and how the device will be monitored. If the remote site requires local subscription-based threat inspection, clustered high availability, larger port density or a different performance profile, FourTeck can help compare the NV5 with another WatchGuard Firebox model before a purchase order is raised.
Deployment Planning for WatchGuard Firebox NV5
An NV5 rollout should be treated as a network project, not only a hardware shipment. The implementation team should document the internet handoff, public or private WAN addressing, local subnet, DHCP role, DNS requirements, routes to corporate networks, VPN peer details, VLAN expectations, local device dependencies and any services that must continue during link changes. When many branches use similar designs, a standard site template can simplify rollout while still allowing location-specific addressing and ISP details.
The head-office or data-centre side is equally important. The central Firebox must have the correct BOVPN and routing design, adequate capacity for the combined branch traffic and suitable policy controls for resources accessed from remote locations. Logging and monitoring should make it possible to distinguish branch connectivity problems from ISP outages, DNS issues or application failures. The organisation should also define who owns cloud administration, configuration backups, firmware planning and change approval.
For Dubai projects, FourTeck can help structure the rollout around site readiness, ISP details, branch numbering, device activation, WatchGuard Cloud onboarding, BOVPN testing and handover. Buyers can review broader firewall deployment guidance for Dubai to prepare the network information required before installation.
Who Should Consider the NV5?
Retail & Kiosks
Remote transaction points, digital kiosks and small retail locations that need encrypted connectivity to central systems.
ATM & Financial Edge
Purpose-driven remote devices where secure network transport and centrally governed connectivity are more important than local UTM features.
Remote Offices
Small branches that primarily consume corporate applications through a secure branch VPN and do not need a larger local firewall platform.
Operational Equipment
Remote network-connected equipment that needs controlled access to central management, telemetry or business applications.
WatchGuard Firebox NV5 Dubai
For customers searching for WatchGuard Firebox NV5 Dubai, the most important buying question is whether the remote location truly needs a purpose-built VPN edge gateway. Dubai organisations often operate a mix of headquarters, satellite offices, showrooms, service counters, warehouses, temporary project locations and unattended operational endpoints. An NV5 can be considered where these sites need secure connectivity back to a central WatchGuard environment and the local requirement does not call for full subscription security services. This distinction helps avoid buying a compact device for the wrong job simply because it carries the Firebox name.
A Dubai deployment should begin with the ISP and topology. Confirm whether the branch receives a static public IP, dynamic public IP or private address behind an upstream router; whether the NV5 will terminate the internet connection directly; whether the local LAN uses a single subnet or VLANs; and which applications must cross the BOVPN. Retail systems, building-management devices, payment-related equipment, CCTV management and business workstations can have very different routing and access needs. The network team should specify which traffic must remain local and which traffic should be sent to headquarters for central control.
Physical deployment also deserves attention. The NV5 is a tabletop appliance, but it should still be installed indoors in a secure location with stable conditioned power, organised cabling and restricted access. If a branch is in a cabinet, kiosk enclosure or back-office room, check ventilation and make sure the site staff can identify power and WAN connections without needing administrator credentials. For multi-site projects, label each device and document its serial number, location, ISP circuit, local subnet and VPN peer.
FourTeck can help Dubai buyers review model fit, WatchGuard Cloud onboarding, BOVPN requirements and deployment scope. For a broader edge-security design, compare the NV5 requirement with the perimeter firewall planning guidance so the role of the remote gateway and the role of the main security firewall are clearly separated before quotation.
WatchGuard Firebox NV5 UAE
UAE buyers evaluating the WatchGuard Firebox NV5 typically need consistency across more than one location. A company may have its main IT team in Dubai or Abu Dhabi while operating smaller branches, service locations, warehouses, kiosks or remote equipment across several emirates. In this scenario, the value of the NV5 comes from using a repeatable remote-connectivity design: consistent WatchGuard Cloud registration, a standard BOVPN structure, controlled local addressing and clear support ownership. The appliance should be part of a broader architecture rather than treated as an isolated firewall purchase.
Procurement teams should request the exact appliance and support entitlement required for the deployment and should avoid assuming that subscription security bundles available for other Firebox models apply to the NV5. The NV5 does not support Firebox subscription security services. If a UAE branch needs local intrusion prevention, web filtering, malware inspection or other subscription-driven UTM functions, confirm a different Firebox platform. Where a branch primarily needs encrypted transport to a central location, the NV5 can provide a simpler fit.
Network readiness differs between sites. Some UAE locations may use fibre handoff from a business ISP, while others may depend on an upstream router, managed circuit or wireless backup. Document the actual interface handoff and public addressing instead of assuming every site will be identical. If failover is required, confirm supported modem options, data plans and changeover behaviour before rollout. The device’s three Gigabit Ethernet ports provide flexibility, but the interface design must still match the WAN, LAN and optional secondary path requirements.
For a multi-emirate project, create a branch schedule that includes site name, contact person, ISP circuit, local subnet, activation status, cloud registration, tunnel status and test results. This operational discipline can be more important than the hardware specification itself. FourTeck can help UAE buyers prepare a bill of materials, define deployment assumptions and coordinate technical review through the main Firewall Dubai solution portal.
WatchGuard Firebox NV5 Uganda
For Uganda deployments, the WatchGuard Firebox NV5 can be relevant to organisations that need a controlled VPN path between a central IT environment and small branch or edge sites. The decision should start with connectivity conditions at each location. Business-grade fibre may be available at one site while another uses wireless, LTE or a provider-managed router. Because the NV5 is designed around secure remote connectivity, the organisation should document whether the branch can establish outbound VPN reliably, whether public addressing is required, and how failover will work if the primary link becomes unavailable.
A common procurement risk is to focus on the low physical footprint and overlook feature boundaries. The NV5 is not the correct choice when the branch requires local Firebox subscription security services or a clustered high-availability pair. It is better suited to a controlled edge design where security policy and corporate resources are reached through BOVPN. Uganda buyers should therefore define the business application path before ordering. If a branch needs access to ERP, finance systems, VoIP management, remote monitoring or central file services, note the expected traffic and the tolerance for link interruption.
Power quality and physical security are practical site factors. Remote devices should be installed with stable power protection, secure access and labelled cabling. If a branch has non-technical staff, deployment documentation should allow them to identify power, WAN and LAN connections without changing configuration. WatchGuard Cloud can help reduce on-site configuration effort where the organisation has a consistent activation and onboarding process.
For organisations operating across Uganda, a standard branch template can reduce support complexity. Keep a central record of each appliance, ISP, local subnet, VPN peer, activation date and responsible support contact. FourTeck can help assess whether the NV5 or a broader Firebox model better fits the required security scope, while regional procurement discussions can also be coordinated through FourTeck’s wider Africa-facing business channels where appropriate.
WatchGuard Firebox NV5 Kampala
Kampala organisations searching for a WatchGuard Firebox NV5 often have a practical branch-connectivity requirement: a small office, retail point, finance counter, clinic, service site or remote operational location needs secure access to systems hosted at headquarters or in a data centre. The NV5 can serve this purpose when the project is built around BOVPN and centralised management. The first planning task is to list exactly which central resources the Kampala site needs and whether the branch requires direct internet breakout or should send selected traffic through the corporate network.
The ISP handoff should be verified on site before deployment. Record whether the provider equipment uses bridge mode or routing, what IP information is provided, whether there is carrier-grade NAT, and whether the organisation has any secondary connectivity. These details affect tunnel establishment and troubleshooting. If a backup modem or alternative link is part of the design, confirm compatibility and operating procedure rather than assuming all cellular devices will work in the same way.
Kampala deployments may also benefit from careful remote-support preparation. Create a simple branch pack containing the site diagram, device label, WAN details, local subnet, support contact, activation record and approved reboot procedure. The NV5 supports WatchGuard Cloud management, which can reduce the need for local configuration access, but physical troubleshooting may still require a person on site to verify cabling and power. The appliance should be secured so unauthorised users cannot disconnect or tamper with it.
Before purchase, confirm that the NV5 feature set matches the security requirement. It does not support Firebox subscription security services, FireCluster, load balancing or link aggregation. If the Kampala branch is expected to perform local advanced threat inspection or act as a larger internet security gateway, another model should be evaluated. FourTeck can help structure the requirement around branch role, VPN topology, support ownership and future rollout plans rather than selecting on model name alone.
WatchGuard Firebox NV5 Arua
For an Arua branch or remote operational site, the WatchGuard Firebox NV5 should be considered mainly for secure, manageable connectivity to a central WatchGuard environment. The business case may be a small regional office, field support location, remote administrative point, kiosk or equipment site that needs to reach central applications without hosting a full security stack locally. In these scenarios, the NV5’s compact hardware and BOVPN role can be attractive, but network reliability and support logistics deserve as much attention as the appliance itself.
Start by documenting the available internet services at the intended Arua location. If the primary circuit is wireless or mobile rather than fixed fibre, measure real stability and latency during business hours and confirm whether the provider uses NAT that could affect inbound services. Branch Office VPN can work across common internet connections, but the operational experience depends heavily on the link. If the application is sensitive to interruption, define a backup connectivity option and who is responsible for restoring service when the primary circuit fails.
Because remote support travel may be less convenient than in a major metropolitan site, installation discipline becomes important. Place the NV5 indoors in a secure, accessible cabinet or office area with conditioned power. Label power and Ethernet connections. Keep the local ISP device and NV5 power adapters distinguishable. Record device activation, software version, local network range and tunnel peer. A short handover note for branch staff can explain what lights and cables may be checked without exposing administrator credentials.
The NV5 should not be selected if the Arua location requires local subscription security services, high availability clustering or extensive interface aggregation. Its value is in a simple, centralised edge design. FourTeck can help an organisation compare that design with a larger Firebox alternative and define a quotation that includes the correct appliance, support entitlement, rollout assumptions and any required configuration assistance.
WatchGuard Firebox NV5 Mbarara
Mbarara businesses and institutions may use the WatchGuard Firebox NV5 where a remote branch needs an encrypted path to headquarters but has only a small local network. Examples can include a sales office, service desk, healthcare branch, education administration point, retail site or logistics office. The technical fit depends on whether the branch is primarily consuming centrally hosted services through VPN. If the branch must provide full local next-generation firewall security services, the NV5’s feature limits make another Firebox model more suitable.
A useful planning exercise is to separate business-critical traffic from ordinary internet use. Identify systems such as ERP, inventory, billing, VoIP control, remote desktop or internal web applications that must reach central infrastructure. Decide whether internet browsing should exit locally or follow the BOVPN to a central firewall. This design choice affects bandwidth consumption at both the branch and head office. The central environment also needs enough capacity to receive traffic from all deployed branches, especially if multiple NV5 sites operate at the same time.
Mbarara deployments should include a practical support plan for ISP outages and equipment resets. The NV5 has three Gigabit RJ45 interfaces and a compact tabletop chassis, but a clean installation still needs stable power, secure placement and correctly documented cabling. Where the organisation uses WatchGuard Cloud, branch configuration can be managed centrally, reducing reliance on local technical staff. However, the business should still identify someone who can physically inspect the site when required.
For procurement, request a model-specific quote and describe the exact site role rather than using a generic “firewall” line item. Include the number of Mbarara locations, ISP type, local network range, head-office peer, required support term and target deployment schedule. FourTeck can then help review whether the NV5 matches the architecture or whether another WatchGuard appliance is a better long-term fit.
WatchGuard Firebox NV5 Gulu
A Gulu deployment of the WatchGuard Firebox NV5 can make sense for a small branch, field location or remote service point that needs secure access to central corporate resources. The appliance is particularly suited to purpose-driven remote connectivity rather than a broad local security stack. Before buying, identify whether the site needs BOVPN to a WatchGuard headquarters environment, what applications will use the tunnel, and whether the branch should maintain limited local internet access if the VPN becomes unavailable.
Connectivity resilience is an important design topic for remote locations. If the Gulu site relies on a single provider, the organisation should define what happens during an outage: does the branch stop processing, switch to a mobile connection, or use an alternate circuit? Supported modem capabilities can be considered where appropriate, but the exact modem, carrier service and Fireware compatibility should be checked before procurement. A backup path only adds value if it is tested and the branch staff know when it should be used.
Centralised WatchGuard Cloud administration can simplify a distributed deployment. A standard template can reduce variation between Gulu and other sites, while location-specific settings such as IP addressing and ISP details remain unique. Maintain a site inventory with device serial number, activation information, assigned configuration, local subnet and contact details. This makes remote troubleshooting faster when an issue occurs months after initial installation.
The feature boundary should remain clear: the Firebox NV5 does not support Firebox subscription security services, FireCluster, load balancing or link aggregation. It should therefore be chosen for the right role rather than because it is physically small. FourTeck can assist with a requirement review that compares the NV5 against other Firebox options and considers central firewall capacity, branch bandwidth, VPN policy and support responsibility for a Gulu deployment.
WatchGuard Firebox NV5 Kenya
Kenya organisations with distributed branches can use the WatchGuard Firebox NV5 as part of a standardised remote connectivity architecture. A typical design might place a larger WatchGuard Firebox at a central office or data centre and use NV5 gateways at small sites that need secure BOVPN access to business applications. This can reduce the need to deploy a full local security appliance where the branch role is narrow and predictable. The suitability depends on traffic, internet design and the organisation’s decision about where inspection and internet security policies are enforced.
For a national rollout, site categorisation is useful. Separate locations into groups such as office branches, retail outlets, kiosks, warehouses and unattended equipment. Define a standard LAN range, DHCP policy, VPN naming convention and support process for each group. Kenya deployments may use different ISP technologies between urban and regional sites, so record whether each location uses fibre, fixed wireless, LTE or an upstream managed router. Avoid a single template that assumes the same public addressing at every branch.
The WatchGuard Cloud capability can help central teams maintain consistent configuration and visibility, while SD-WAN routing can support path decisions within a correctly designed network. Where redundancy matters, the project should define supported alternate links and test failover behaviour. Do not confuse WAN failover planning with unsupported FireCluster or server load-balancing features; these are different architectural functions.
Kenya procurement teams should request clear commercial information covering the exact NV5 appliance, Standard Support entitlement, quantity, regional logistics and configuration scope. If local advanced security services are required at the branch, another Firebox model should be evaluated. FourTeck can help with the technical questionnaire before pricing so the requested hardware matches the intended role and the central WatchGuard environment is ready to terminate and manage the branch VPNs.
WatchGuard Firebox NV5 Kuwait
Kuwait buyers may consider the WatchGuard Firebox NV5 for compact remote branches, service counters, kiosks and connected operational equipment that require secure communication with a corporate WatchGuard environment. The key is to preserve the NV5’s intended role as a VPN gateway. It is not designed to replace a larger branch firewall that must provide subscription security services locally. Before quotation, identify whether the site’s applications can operate through BOVPN and where the organisation wants web security, threat inspection and internet policy enforcement to occur.
Branch connectivity in Kuwait can be straightforward when business-grade fibre is available, but the project should still document ISP handoff, public addressing and any upstream routing. If a branch uses a provider router or managed service, check whether VPN traffic can pass without unexpected NAT or port restrictions. For backup connectivity, verify the exact supported method rather than assuming a consumer mobile router will integrate with the NV5 design. The three Gigabit RJ45 interfaces provide a compact foundation for the network layout, while USB and serial connectivity may support defined operational needs.
Heat outside a building does not remove the need to follow the vendor’s indoor installation guidance. The NV5 should be placed in a conditioned, protected space with stable power and restricted physical access. For kiosks or back-room cabinets, ensure the enclosure does not create an unsuitable operating environment. Label cabling and document the device so support staff can distinguish the ISP handoff, LAN connection and power adapter.
For multi-branch Kuwait deployments, central configuration and repeatable activation can reduce field engineering effort. Use WatchGuard Cloud to support the management workflow and keep records of each site’s local subnet, tunnel peer and support contact. FourTeck can review the architecture, confirm whether the NV5 or another Firebox model is appropriate and prepare a quotation aligned with the exact deployment scope.
WatchGuard Firebox NV5 Ghana
Ghana organisations evaluating the WatchGuard Firebox NV5 should focus on remote-site connectivity rather than generic firewall feature lists. The appliance is intended for small offices, remote workers and remote devices that need secure communication with a corporate or data-centre Firebox. That makes it relevant to distributed retail, financial services, service counters, logistics locations, administrative branches and other sites where a controlled VPN path is the main requirement. If the local branch must run subscription-based security services itself, the model selection should be reconsidered.
Connectivity quality can vary by location, so the rollout plan should include real ISP information for every Ghana site. Record the service type, addressing method, provider equipment, expected bandwidth, backup link and escalation contact. A BOVPN architecture can centralise access to internal applications, but branch performance will still depend on the underlying circuit. If the business uses cloud applications directly from the site, decide whether that traffic should break out locally or traverse the corporate VPN based on the security architecture and available bandwidth.
A central configuration process can improve consistency. WatchGuard Cloud support allows the IT team to manage the NV5 within a broader WatchGuard environment and can reduce repetitive on-site setup. For multiple Ghana locations, use a site naming standard, pre-assign local subnets, document tunnel peers and test each branch against the same acceptance checklist. Tests should include DNS, required internal applications, management reachability, VPN recovery and any failover behaviour.
Procurement should include the exact model, support entitlement, quantity and any required deployment services. Avoid unsupported assumptions about security subscriptions, clustering or load balancing. FourTeck can help compare the requested branch role with the NV5 capabilities and determine whether a larger Firebox model is needed for sites with broader local security or performance requirements.
WatchGuard Firebox NV5 Nigeria
Nigeria enterprises often operate a wide geographic mix of headquarters, regional offices, retail outlets, service sites and remote equipment, which makes branch standardisation an important security and support objective. The WatchGuard Firebox NV5 can be useful where smaller sites need a secure BOVPN path to a central WatchGuard Firebox without the cost and complexity of a full local UTM appliance. The design should start by grouping sites according to business role and connectivity rather than trying to force every location into one template.
Internet reliability, provider NAT and backup connectivity can influence the user experience. For each Nigeria site, document the ISP, service type, public addressing, upstream router, expected bandwidth and fallback plan. Where a branch relies on a mobile or wireless secondary path, test the actual failover workflow before the system is declared complete. The NV5 supports SD-WAN routing capabilities, but routing policy should reflect business priorities such as transaction traffic, remote desktop, voice or management connectivity.
Central security architecture is another procurement factor. If the branch sends corporate traffic through BOVPN, the head-office firewall and upstream internet services must be sized for the aggregate load. The network team should define which applications are accessible from each branch and should avoid broad tunnel policies that expose more resources than necessary. Central logging should make it possible to identify the source branch when troubleshooting or reviewing incidents.
The NV5’s limits remain important: no Firebox subscription security services, FireCluster, load balancing or link aggregation. Some Nigeria branches may therefore need a different Firebox model even if others can use NV5. FourTeck can help create a site-by-site requirement matrix, separate NV5-appropriate branches from higher-demand locations and prepare commercial options that match the organisation’s actual rollout rather than using one appliance everywhere.
WatchGuard Firebox NV5 Seychelles
In Seychelles, the WatchGuard Firebox NV5 can be considered for a remote office, hospitality administration point, retail outlet, service counter or connected operational site that needs secure access to systems hosted at another location. Island geography can make remote support and connectivity planning especially important, so the appliance should be selected as part of an operational model that includes ISP resilience, cloud management, clear configuration records and a realistic replacement or support process.
The first question is whether the site has a stable primary connection and whether a secondary path is required. If the branch depends on a single internet service, define what happens when that link fails. If a backup modem or alternative circuit is planned, verify supported hardware and test recovery. The NV5’s SD-WAN routing and BOVPN functions can support a structured edge design, but they cannot compensate for a poorly understood ISP handoff or an untested backup service.
The physical appliance is small, but remote installation should still be professional. Place it indoors in a secure, ventilated and power-protected location. Keep cabling labelled and maintain a local diagram so non-specialist site staff can report the status of WAN, LAN and power connections. WatchGuard Cloud can reduce the need for local administrative access, which is valuable when central IT staff are not on the same island or site. Standardised configuration also helps when several properties or branches use similar networks.
Before ordering, confirm whether the branch needs local subscription security services. The NV5 does not support those services and is best used for secure edge connectivity. If the Seychelles site hosts many users, requires local advanced threat protection or needs a broader high-availability design, another Firebox model may be more suitable. FourTeck can help review the topology, branch purpose, central Firebox capacity, support term and logistics before quotation.
WatchGuard Cloud, Zero-Touch Thinking and Multi-Site Operations
One of the strongest reasons to consider the NV5 for distributed operations is the ability to standardise how branches are brought online. WatchGuard has positioned the platform for centrally managed deployment, and WatchGuard Cloud can reduce the amount of manual configuration required at the remote site. The practical goal is not simply “zero touch” as a marketing phrase; it is to make each site predictable. The IT team should know which configuration belongs to which serial number, what the expected local subnet is, which BOVPN peer will be used, and what acceptance tests must pass before a branch is handed over.
For larger rollouts, maintain a deployment register. Useful fields include site code, physical address, local contact, ISP circuit, WAN addressing, NV5 serial number, WatchGuard Cloud status, local network range, tunnel peer, activation date, test result and support owner. This helps when a device is replaced, an ISP changes, or a branch reports a connectivity problem long after installation. A clean naming convention for policies and tunnels also makes central administration easier.
Central management does not remove the need for secure operational controls. Administrator roles should be limited, multi-factor authentication should be used where supported by the management platform and change procedures should be documented. Firmware should be maintained within supported versions, and WatchGuard currently recommends not running Fireware versions below the minimum guidance published for NV5. Before a rollout, confirm the approved software baseline and validate that the central Firebox environment is compatible with the planned branch configuration.
NV5 Selection Checklist Before You Request a Quote
Choose NV5 when
- The remote site primarily needs secure BOVPN connectivity to a corporate WatchGuard environment.
- A small tabletop appliance suits the physical location.
- Central management and repeatable remote rollout are priorities.
- The branch does not require Firebox subscription security services locally.
Consider another model when
- The branch needs local subscription-based threat protection services.
- FireCluster high availability is required.
- Load balancing or link aggregation is a design requirement.
- The site needs a broader port, performance or security profile than the NV5 is designed to provide.
Frequently Asked Questions
Is the WatchGuard Firebox NV5 a full UTM firewall?
The NV5 runs Fireware and is part of the Firebox family, but WatchGuard specifically positions it as a VPN gateway for remote sites and devices. It does not support Firebox subscription security services. If your site needs local subscription-based threat inspection, web filtering or similar services, confirm another Firebox model.
What is the main use of the Firebox NV5?
Its primary use is secure connectivity for remote workers, small offices and remote devices through BOVPN to a corporate office or data centre. WatchGuard also identifies use cases such as kiosks, ATMs and remote office equipment.
How many Ethernet ports does the NV5 have?
The hardware guide lists three 1000Base-TX RJ45 network interfaces. The appliance also includes one USB 3.0 port and one RJ45 serial port.
Does the NV5 support WatchGuard Cloud?
Yes. WatchGuard documentation supports NV5 connection to WatchGuard Cloud, which can be used for central management and deployment workflows. The exact configuration process should follow the currently supported Fireware and WatchGuard Cloud documentation.
Does the NV5 support SD-WAN?
WatchGuard lists SD-WAN routing as supported for the NV5. The practical configuration should be designed around the available WAN links, link monitoring and application priorities rather than enabling SD-WAN without a traffic policy.
Can I use FireCluster with two NV5 appliances?
No. WatchGuard documentation states that FireCluster is not supported on the NV5. If high availability through FireCluster is a requirement, evaluate a supported Firebox model.
Can the NV5 use link aggregation?
No. Link aggregation is listed as unsupported for the NV5. The three Gigabit Ethernet interfaces should be planned within the supported topology.
Can FourTeck help configure BOVPN?
FourTeck can discuss deployment and configuration scope for a quotation, including branch VPN planning, central peer requirements, addressing, routing and acceptance testing. The final service scope should be confirmed before purchase.
What information should I provide for a Dubai quote?
Provide the number of sites, location, ISP details, local subnet, head-office Firebox model, required applications, VPN topology, expected support term, deployment target and whether configuration assistance is required. This helps determine whether the NV5 is the correct appliance and what should be included in the bill of materials.
Is the NV5 suitable for every small branch?
No. A small physical site can still need advanced local security services, greater port density, different performance or high availability. Select the appliance according to network requirements, not only branch size.
Related FourTeck Firewall Resources
Firewall Deployment DubaiPrepare internet, VPN, policy, routing and handover information before scheduling an NV5 rollout.
Perimeter Firewall PlanningUnderstand where the main security gateway belongs when NV5 devices connect remote sites back to a central environment.
About FourTeck Firewall DubaiReview FourTeck’s firewall consultation, configuration, migration and support approach for UAE business networks.
Firewall Dubai HomeExplore the wider FourTeck firewall portfolio and service information for Dubai and UAE projects.
Decision Recap: Is the Firebox NV5 the Right Fit?
The WatchGuard Firebox NV5 is a focused remote-edge VPN gateway. It is strongest when a small or unattended site needs BOVPN connectivity, central WatchGuard management and a compact deployment footprint. It should not be chosen when the branch requires local Firebox subscription security services, FireCluster, load balancing or link aggregation. A correct decision therefore depends on the site role, central Firebox design, internet connection and support model.
Remote office, kiosk, ATM or edge equipment needing secure connection to corporate resources.
Site needs local subscription security, clustering, broad NGFW functionality or more complex interface requirements.
Share branch count, ISP details, corporate Firebox model, network ranges and required applications for a fit review.
Quotation Checklist
For a useful WatchGuard Firebox NV5 quotation, prepare the information below. This reduces back-and-forth and helps ensure the quoted appliance and service scope match the actual branch design.
- Number of NV5 sites and delivery destinations.
- Primary and backup ISP type for each location.
- WAN addressing and upstream router information.
- Local subnet or VLAN plan.
- Central WatchGuard Firebox model and management method.
- Applications and networks that must be reachable through BOVPN.
- Required support term and target deployment schedule.
- Whether FourTeck configuration, rollout coordination or migration assistance is required.
Plan Your WatchGuard Firebox NV5 Deployment with FourTeck
Share your branch topology, existing WatchGuard environment, ISP details and required business applications. FourTeck can help review whether the NV5 is the correct gateway, identify feature limitations before purchase, prepare the deployment scope and coordinate a commercial quotation for Dubai, UAE and supported regional projects.


Reviews
There are no reviews yet.