
WatchGuard Firebox T125 in Dubai, UAE and Regional Markets
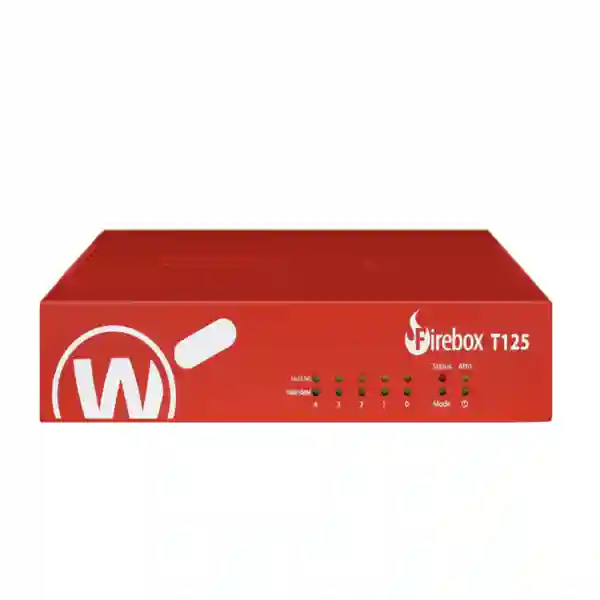
The WatchGuard Firebox T125 is a compact next-generation tabletop firewall built for small offices, branch locations and remote sites that need business-grade traffic control without moving to a large rackmount platform. WatchGuard positions the T125 for environments of about 25 users, with one 2.5 GbE interface, four 1 GbE interfaces, SD-WAN support, local or cloud management, and performance figures designed for realistic small-site security workloads. FourTeck helps buyers turn those specifications into a practical deployment plan by reviewing internet bandwidth, inspection requirements, VPN demand, network segmentation, licensing, migration scope and support expectations before a quotation is prepared.
Quick buyer check
Before ordering, confirm the real inspected traffic rather than relying only on the ISP headline speed. HTTPS inspection, IPS, antivirus, VPN, logging and policy complexity all influence sizing.
Also confirm whether the requirement is the wired T125 or the separate T125-W wireless model. The T125-W adds Wi-Fi 7; wireless capability should not be assumed for the standard T125.
Vendor UDP 1518 test figure; production results depend on enabled services and traffic.
Useful sizing reference when multiple security inspection functions are active.
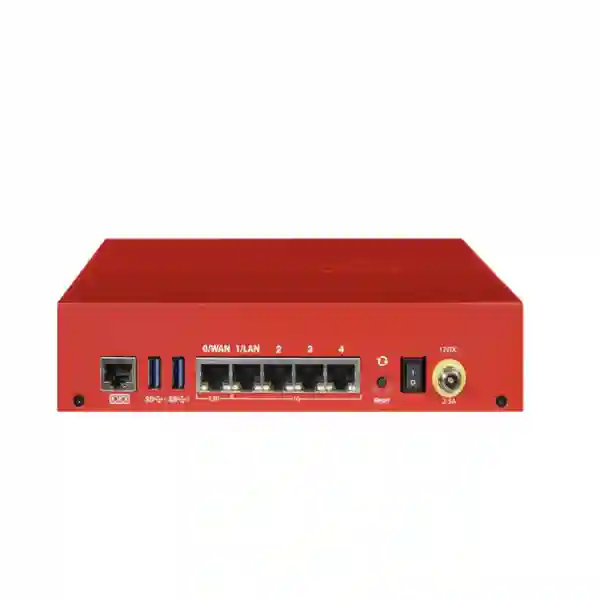
Five copper Ethernet interfaces provide practical WAN, LAN, VLAN and branch options.
WatchGuard positions the model for small sites; final sizing must consider devices and applications too.
What the WatchGuard Firebox T125 is designed to solve
A small office does not necessarily have a small security requirement. Even a twenty-person site may run cloud accounting, CRM, Microsoft 365 or Google Workspace, remote desktop, voice systems, CCTV, guest Wi-Fi, online banking, file sharing and site-to-site VPN connections. The T125 is intended to place a dedicated security enforcement point between those business systems and external networks. It can control inbound and outbound traffic, separate network zones, apply security policies, provide VPN connectivity and feed operational visibility into WatchGuard management and reporting tools.
For procurement teams, the important point is that the appliance is only one part of the solution. Security subscriptions, support entitlement, firmware planning, deployment services and renewal terms can materially change the commercial package. A quotation should therefore identify the appliance model, license bundle and term, support scope, any rack-mount requirement, migration work, VPN configuration, testing and documentation. That avoids comparing a hardware-only offer with a complete security bundle as though they were equivalent.
For IT teams, sizing should use inspected throughput and real traffic patterns. WatchGuard publishes 510 Mbps UTM full-scan throughput, 270 Mbps HTTPS throughput with IPS enabled, 725 Mbps IPS full-scan throughput, 880 Mbps antivirus throughput, 660 Mbps firewall IMIX and 480 Mbps VPN IMIX figures for the T125. The higher 2.28 Gbps firewall and 1.44 Gbps VPN figures are vendor UDP 1518 test measurements. These numbers are useful comparison inputs, but production performance varies with packet size, TLS inspection, policies, logging, concurrent sessions, software version and the selected security services.
Verified WatchGuard Firebox T125 specifications
| Item | Published detail | Buyer relevance |
|---|---|---|
| Platform | WatchGuard Firebox T125, Fireware | Tabletop firewall for small sites and branch networks. |
| Interfaces | 1 × 2.5 GbE RJ45, 4 × 1 GbE RJ45 | Suitable for WAN/LAN separation, VLAN trunks and multiple network zones. |
| I/O | 2 × USB-A 3.2, 1 × RJ45 serial | Useful for maintenance, support snapshots, backup/restore and console access. |
| Firewall | 2.28 Gbps UDP 1518; 660 Mbps IMIX | Use IMIX and inspected figures for more conservative planning. |
| UTM | 510 Mbps full scan | A practical reference for offices enabling multiple security controls. |
| HTTPS | 270 Mbps with IPS enabled, full scan | Important where encrypted traffic inspection is part of policy. |
| IPS / Antivirus | 725 Mbps IPS; 880 Mbps antivirus | Security service performance should be matched to actual internet usage. |
| VPN | 1.44 Gbps UDP 1518; 480 Mbps IMIX | Relevant to branch tunnels and remote connectivity planning. |
| VPN tunnels | 10 branch-office VPN tunnels; up to 25 mobile VPN users in WatchGuard comparison data | Confirm the intended VPN type and concurrent user requirement before purchase. |
| Hardware | Quad-core 1.1 GHz CPU, 4 GB DDR4, 16 GB eMMC | Platform resources support Fireware operations and small-site security workloads. |
| Power | 30 W adapter, 20 W maximum published consumption | Plan conditioned power and appropriate UPS protection where required. |
| Physical | 230 × 210 × 44 mm; 2.06 kg | Desktop, wall or optional rack-mount placement can be considered. |
Performance values are manufacturer-published test results, not a guarantee for every production deployment. Actual results depend on configuration, security services, traffic composition, firmware and network design.
T125 or T125-W?
Choose the standard T125 when the firewall will connect to existing switches and access points through Ethernet. Choose the separate T125-W model only when integrated wireless is required and the wireless design has been reviewed. WatchGuard lists Wi-Fi 7 capability for the T125-W, using external antennas. Do not assume the wired T125 includes Wi-Fi simply because both models belong to the same family.
Cloud or local management?
The Firebox can be locally managed with Fireware tools or managed through WatchGuard Cloud. The choice should reflect who administers policy, how many sites are involved, reporting needs, change-control practices and the organization’s support model. Multi-site deployments may benefit from centralized policy consistency, while some customers prefer locally managed workflows for existing operational reasons.
Licensing, subscriptions and procurement
A WatchGuard Firebox quotation can include different security and support packages, so buyers should compare like with like. A hardware-only listing does not provide the same commercial scope as an appliance bundled with Standard Support, Basic Security Suite or Total Security Suite for a defined term. The exact services and feature entitlement should be checked against the current WatchGuard offer at the time of purchase. Where malware analysis, DNS security, advanced threat services, richer reporting or other subscription-dependent capabilities are required, they should appear explicitly in the bill of materials.
FourTeck can help build a quotation around the required appliance, subscription term, installation work and support scope. Buyers in the UAE can also review broader technology and cybersecurity services through FourTeck UAE. For a useful comparison exercise, ask for the appliance SKU or bundle reference, license term, security suite, hardware support entitlement, renewal date, optional rack kit, professional services, configuration deliverables and handover documentation.
Deployment design for a WatchGuard Firebox T125
A clean T125 deployment starts with network discovery. Identify the ISP handoff, public IP requirements, current router or firewall, switching design, VLANs, wireless networks, servers, printers, voice systems, CCTV, guest access, remote users, branches and cloud applications. That inventory determines which interfaces and zones are required and which traffic flows must be preserved during cutover. It also prevents a common mistake: copying an old firewall configuration into a new appliance without checking whether every rule is still needed.
The single 2.5 GbE interface can be useful where an ISP, core switch or trunk supports a multi-gigabit connection, but the security throughput figures still determine the realistic inspected workload. Four 1 GbE interfaces can be assigned to WAN, LAN, DMZ, dedicated server, guest or other physical zones, while VLANs provide logical segmentation when more networks are required. The exact topology should be based on the switch infrastructure and failure model rather than using every physical port simply because it is available.
Before production cutover, the configuration should be backed up and key tests should be documented: internet browsing, DNS, email, cloud applications, inbound published services, site-to-site VPN, remote VPN, printing, voice, business applications and management access. Logging should be checked so the team can distinguish a policy block from a routing or DNS issue. FourTeck’s Firewall Dubai security practice can be used as a regional starting point for firewall planning and consultation.
WatchGuard Firebox T125 Dubai
Businesses searching for WatchGuard Firebox T125 Dubai are usually trying to solve one of four problems: secure a new office internet connection, replace an aging firewall, connect a branch safely to headquarters, or add stronger inspection and reporting than a basic router can provide. Dubai sites often combine cloud applications, IP telephony, CCTV, guest Wi-Fi, wireless access points and remote work in a compact office footprint, so the firewall needs a clear segmentation plan even when the headcount is modest. The T125 is relevant to this type of branch requirement because WatchGuard positions it for around 25 users and provides a mix of 2.5 GbE and Gigabit Ethernet connectivity in a tabletop appliance.
For a Dubai quotation, buyers should provide the internet circuit speed, expected peak traffic, number of users and devices, VPN requirement, VLAN list, public services, existing firewall brand, subscription term and whether onsite installation is required. A 1 Gbps or faster ISP link does not automatically mean every security feature will inspect traffic at line rate. If HTTPS inspection, IPS, antivirus and application controls are required, the published 510 Mbps UTM and 270 Mbps HTTPS inspection figures are more useful planning references than the maximum firewall packet test.
Physical installation also deserves attention. The T125 is an indoor appliance with a published operating range of 0°C to 40°C, so it should be placed in a conditioned, secure communications area rather than an exposed store room or outdoor cabinet. Dubai offices that rely on UPS systems should include the firewall, ISP equipment and core switching in the protected power design. If the device will be rack mounted, confirm the optional rack kit and keep adequate airflow around the appliance.
FourTeck can help a Dubai buyer define appliance, security suite, VPN configuration, VLAN design, migration tasks, testing and documentation in one scope. This is especially useful where procurement wants a complete landed solution rather than an online hardware listing. The objective is to obtain a configuration that supports the site’s real applications, not merely to purchase a model number.
WatchGuard Firebox T125 UAE
For customers searching WatchGuard Firebox T125 UAE, the key question is often whether one standardized firewall can secure multiple small locations such as sales offices, clinics, warehouses, retail outlets or professional-service branches. The T125 can support a branch design where each location uses common security policy, VPN connectivity and centralized oversight while retaining local interfaces for WAN, LAN and segmented networks. WatchGuard Cloud management is available as an alternative to locally managed Fireware workflows, which can be useful when an IT team must maintain consistent rules across geographically separate sites.
UAE sizing should consider more than staff count. A twenty-user branch with cloud backup, high-definition video meetings, guest Wi-Fi and large file transfers can create more inspected traffic than a larger administrative office with lighter application use. Procurement should therefore collect peak bandwidth, concurrent devices, number of VLANs, site-to-site VPN demand, remote users and security services to be enabled. If the organization expects internet upgrades during the service life of the firewall, that growth should be part of the initial model review.
For multi-emirate deployments, policy consistency is another buying factor. Naming conventions for address objects, VLANs, branch tunnels and security rules should be standardized before the second or third device is deployed. A common configuration framework reduces support effort and makes troubleshooting faster when branches connect to shared applications or data-center resources. Where a site has a separate guest network, CCTV devices, IP phones or building systems, those networks should be segmented based on required communication rather than placed in one flat LAN.
Commercially, UAE buyers should request a quote that separates hardware, WatchGuard subscription or support term, optional accessories and professional services. That makes future renewals easier to understand and helps avoid the common situation where a low initial hardware price excludes the security services expected by the IT team. FourTeck can coordinate the technical checklist and quotation scope for UAE firewall projects.
WatchGuard Firebox T125 Uganda
Customers researching WatchGuard Firebox T125 Uganda commonly need a secure edge appliance for a head office, branch, clinic, school, NGO site, retail location or distributed business network. The decision should start with internet availability at each site, the applications that must remain accessible and the importance of branch-to-head-office connectivity. A T125 can be considered where a small site needs a dedicated firewall, VPN connectivity, segmentation and central visibility without moving to a larger rack platform.
In Uganda, network designs may need to accommodate different ISP technologies and variable link characteristics between locations. If a branch has a primary fixed connection and a separate backup path through another router or provider, the firewall policy and routing design should define which business applications must continue during failover. SD-WAN capability can support path-selection strategies, but the actual WAN architecture, modem handoff and failover testing must be designed for the customer’s providers and equipment rather than assumed from the firewall specification alone.
A remote branch may also need tighter control over bandwidth. Cloud backup, operating-system updates and video traffic can consume capacity needed by ERP, voice or point-of-sale applications. Firewall policies can contribute to a more disciplined network, but the project should first identify critical traffic and expected usage. VPN tunnels should be tested under realistic conditions so latency, packet loss and route dependencies are understood before the site becomes dependent on the tunnel.
Uganda buyers can review broader FourTeck regional services through FourTeck Uganda. When requesting a T125 quotation, provide the site city, user count, internet links, branch connections, required security suite, desired subscription term, existing firewall details and whether remote or onsite implementation is expected. This gives sales and engineering teams enough information to discuss a complete deployment instead of quoting an appliance in isolation.
WatchGuard Firebox T125 Kampala
A search for WatchGuard Firebox T125 Kampala often comes from organizations that have a main office or busy branch with more application traffic than smaller regional sites. Kampala businesses may combine staff browsing, cloud productivity suites, accounting systems, IP telephony, video meetings, CCTV access and remote users on the same internet service. In that situation, a firewall purchase should be treated as an application and segmentation project rather than a simple router replacement.
The T125 provides five copper Ethernet interfaces, including a 2.5 GbE port, which gives a network designer flexibility for ISP, core switch and dedicated zone connections. The right port map depends on the existing switching environment. Where multiple VLANs already terminate on a managed switch, a trunk to the firewall may be more scalable than dedicating one physical port to every department. Typical Kampala office designs may separate staff, guest Wi-Fi, voice, CCTV, servers and management networks, then permit only the traffic required between them.
If the Kampala office is the hub for other Ugandan branches, branch-office VPN capacity becomes an important design point. WatchGuard publishes support for 10 branch-office VPN tunnels on the T125. The number alone does not prove the model is suitable: traffic volume, concurrent encrypted throughput, routing, failover, application sensitivity and expected growth must also be checked. A branch hub that will aggregate heavy traffic from many sites may justify a larger model even if the tunnel count appears sufficient.
Procurement teams should request a bill of materials that clearly identifies the T125, security licensing term, support entitlement, optional rack hardware, deployment services and documentation. If migrating from another firewall, provide the current configuration or a sanitized rule and object summary so migration complexity can be estimated. This reduces change-window surprises and allows the implementation plan to include validation of internet, VPN, cloud, voice and published application traffic.
WatchGuard Firebox T125 Arua
For WatchGuard Firebox T125 Arua requirements, buyers are often evaluating security for a regional office, service point, NGO location, educational site, clinic, warehouse or branch that must connect reliably to systems hosted elsewhere. The T125 can serve as the security gateway for a modest site, but the deployment should reflect the realities of the local connectivity and the importance of remote applications. Before selecting the firewall, identify which functions must continue if bandwidth is constrained: business systems, voice, VPN, email, web applications, cloud identity or remote support.
Branch networks are easier to support when they use simple, well-documented segmentation. A small Arua office may still need separate networks for staff, guest access, CCTV and infrastructure management. VLAN-based separation can reduce unnecessary exposure between device groups while preserving a straightforward cabling design. The firewall rulebase should use meaningful names and avoid broad any-to-any permissions, because remote troubleshooting becomes much harder when policy intent is unclear.
Power quality and equipment placement also matter for regional branches. WatchGuard specifies indoor use and a 0°C to 40°C operating range for the T125. The firewall should be kept in a secure, ventilated location and connected through suitable conditioned power or UPS protection where required. The ISP handoff, firewall and core switch should ideally share a power-protection strategy so a brief outage does not leave only part of the network running.
For an Arua quote, include the WAN type, expected bandwidth, number of users and endpoints, head-office VPN requirement, local VLANs, remote-support method and preferred license term. If the site will be managed from Kampala or another central IT location, clarify whether WatchGuard Cloud or locally managed Fireware workflows fit the support team better. The goal is a branch appliance that can be administered consistently without unnecessary travel or complex local intervention.
WatchGuard Firebox T125 Mbarara
Businesses looking for WatchGuard Firebox T125 Mbarara may be securing a growing office, branch, hospitality site, clinic, retail location, educational institution or distribution operation. These environments often mix business computers with guest devices, payment systems, cameras, printers, access points and cloud services. Even when the user count fits a small-firewall profile, the number and type of connected devices can justify stronger segmentation and logging than a consumer or ISP-supplied router provides.
The T125’s 2.5 GbE and four Gigabit interfaces give a designer options for separating WAN, LAN and selected physical zones, while VLANs can extend the design across managed switches. A Mbarara site that operates guest Wi-Fi should normally keep guest traffic away from internal business resources. CCTV recorders and cameras may also be placed in a dedicated segment with limited access from authorized workstations. These are policy-design decisions; the firewall does not create a secure architecture automatically simply because it supports VLANs.
Where the location depends on a VPN back to another office, verify the actual application requirement. Simple web applications behave differently from file shares or real-time voice across higher-latency links. WatchGuard’s published VPN throughput is useful for sizing, but the WAN service itself may be the limiting factor. Testing should include route failover, DNS resolution, authentication and the specific business applications that staff use every day.
A complete procurement request should specify whether the T125 is a new installation or replacement, current internet speed, backup connectivity, VLAN count, VPN peers, remote users, license bundle, support term and required implementation services. If an older firewall is being replaced, provide a summary of public IP mappings, site-to-site tunnels and important access rules. This helps estimate migration work and reduces the risk that a required service is discovered only during cutover.
WatchGuard Firebox T125 Gulu
A WatchGuard Firebox T125 Gulu project is often less about maximum headline throughput and more about creating a manageable, supportable branch security platform. Regional offices can have limited onsite IT resources, so configuration clarity is important. Interfaces, VLANs, address objects, VPN tunnels and policy rules should be named consistently, and the support team should maintain current backups and documentation. That discipline makes it easier to resolve issues remotely when a user reports that an application is blocked or a tunnel is unavailable.
The T125 can be cloud-managed or locally managed, giving organizations flexibility in how they operate the branch. If several Uganda sites use WatchGuard, a common management approach may simplify policy deployment and visibility. If the organization already has established local Fireware procedures, retaining that operational model may be appropriate. The decision should consider who approves changes, where logs are reviewed, whether templates are useful and how emergency access will be handled if the primary management path is unavailable.
Connectivity design should also consider business continuity. If the Gulu site has two possible internet paths, define the failover behavior for VPN and cloud traffic before deployment. A second link is not useful if routes, DNS or tunnel policies prevent critical applications from recovering after the primary link fails. Planned tests should simulate the failure and restoration of the primary connection, not just confirm that both links work independently.
When requesting pricing, avoid comparing only the hardware line item. Ask for the T125 with the intended WatchGuard subscription or support package, the required term, configuration work, VPN setup, migration assistance, test plan and handover documentation. If a wireless firewall is required, specify T125-W rather than assuming Wi-Fi is included in the standard T125. This small distinction prevents a common procurement mismatch and ensures the supplied device matches the site design.
WatchGuard Firebox T125 Kenya
For WatchGuard Firebox T125 Kenya buyers, the appliance can be evaluated as a small-site firewall for professional offices, retail branches, logistics locations, clinics, schools and distributed organizations. Kenya businesses increasingly depend on cloud applications, online payment workflows, remote access and inter-branch connectivity, so the firewall should be sized around actual application use and inspection requirements. A compact branch with many cloud-connected devices may generate more security workload than its employee count suggests.
The T125’s 510 Mbps published UTM full-scan figure is a useful planning reference for a site where multiple security services are active. If the internet service is significantly faster, buyers should decide whether all traffic will receive the same inspection policy and whether future bandwidth upgrades are likely. HTTPS inspection deserves particular attention because WatchGuard publishes a lower 270 Mbps figure with IPS enabled and full scan. Organizations that expect extensive TLS inspection should size conservatively and test the applications that are sensitive to certificate or inspection behavior.
A Kenya deployment may also require secure tunnels between Nairobi and regional branches or between a local office and systems hosted outside the country. VPN design should document tunnel peers, routing, encryption settings, failover and which internal networks are permitted. If remote users also connect, mobile VPN demand should be counted separately from site-to-site tunnels. WatchGuard’s comparison data lists 10 branch-office VPN tunnels and up to 25 mobile VPN users for the T125, but real workload and performance remain key sizing factors.
Buyers can review local technology services through FourTeck Kenya. A useful quotation request should include city, bandwidth, user and device count, VPN sites, VLANs, security subscription preference, renewal term and required installation scope. This allows a technical and commercial comparison that goes beyond basic online hardware pricing.
WatchGuard Firebox T125 Kuwait
Customers searching WatchGuard Firebox T125 Kuwait are often evaluating a compact firewall for an office, branch, retail point, clinic, service company or remote facility. The model can be appropriate when a site needs controlled internet access, segmentation, VPN and security inspection but does not require the port density or aggregate performance of a larger rackmount appliance. The selection should be based on inspected throughput and expected growth rather than choosing the smallest appliance that meets today’s user count.
Environmental placement is particularly important in Gulf deployments. The T125 is specified for indoor use with an operating temperature up to 40°C. It should be installed in an air-conditioned communications area with unobstructed airflow, not an outdoor telecom enclosure or unconditioned room. Power protection should include the firewall, ISP termination and key switching equipment so the security gateway does not reboot repeatedly during power disturbances while other network devices remain online.
Kuwait offices that use multiple internal networks should define segmentation before the firewall is configured. Guest wireless, staff devices, servers, cameras, voice systems and management interfaces do not need unrestricted communication with each other. A concise zone and VLAN matrix makes firewall rule creation easier and helps future support engineers understand why access was allowed. Logging should be enabled in a way that supports troubleshooting without creating unnecessary noise.
For procurement, ask suppliers to state the exact WatchGuard bundle, subscription or support term and professional-service scope. Clarify whether configuration, migration, VPN, policy tuning, firmware update, testing and documentation are included. If the T125 will replace another brand, provide a sanitized summary of the current rulebase and tunnels so the migration effort can be reviewed in advance. The goal is a controlled cutover rather than an improvised one-for-one hardware swap.
WatchGuard Firebox T125 Ghana
A WatchGuard Firebox T125 Ghana requirement can arise in professional offices, schools, clinics, NGOs, retail branches, logistics operations and growing businesses that want stronger control than a standard router provides. The first step should be to define what the firewall must protect: user internet access, cloud services, finance systems, CCTV, guest Wi-Fi, local servers, remote workers or links to other branches. That application inventory is more useful for sizing and policy design than a simple employee count.
Where bandwidth is shared across many services, security policy should support business priorities. Large updates or backup tasks can compete with cloud applications and interactive traffic even when the firewall itself has sufficient capacity. The network design should therefore consider ISP speed, congestion patterns, application criticality and whether a backup path is available. SD-WAN support can form part of a multi-link design, but link performance and failover behavior must be tested with the actual providers and upstream equipment.
For organizations with several Ghana locations, standardization can reduce support effort. Using consistent VLAN numbers where practical, common object naming, repeatable VPN templates and documented change procedures helps engineers troubleshoot branches without relearning each configuration. WatchGuard Cloud may be considered for centralized management and visibility, while locally managed Fireware remains available for organizations that prefer that approach. The operating model should match the IT team’s skills and support responsibilities.
When requesting a quote, provide the intended site, internet bandwidth, number of users and devices, required VPNs, network segments, existing firewall details, desired security suite and subscription term. Also state whether remote configuration, onsite installation or migration support is needed. Buyers should avoid assuming that a retailer’s listed price includes the security services, support entitlement or implementation work needed for production use.
WatchGuard Firebox T125 Nigeria
For WatchGuard Firebox T125 Nigeria buyers, a common use case is securing a small corporate branch or service location that depends heavily on cloud applications and needs a controlled VPN path back to a head office or hosted environment. The T125’s compact format, 2.5 GbE uplink option and four Gigabit interfaces make it flexible for branch designs, but the final model choice should reflect bandwidth, inspection services, concurrent devices and future growth. A branch with many cameras, guest devices or cloud backup jobs can create substantial traffic even if staff headcount is modest.
Multi-WAN planning can be important where organizations use more than one connectivity provider for resilience. The firewall design should identify how default routes, health checks, VPN tunnels and DNS behavior respond when one path fails. If an application is hosted through a fixed public IP or a tunnel is tied to a specific provider, failover may require additional configuration. These dependencies should be documented and tested in a maintenance window rather than discovered during an outage.
Security subscriptions should be included in the commercial discussion from the beginning. Buyers may encounter hardware-only, Standard Support, Basic Security Suite and Total Security Suite offers with very different prices. The quotation should state exactly which bundle and term is being supplied, which advanced security capabilities are expected, and what happens at renewal. This makes competing quotes easier to compare and helps the IT team budget for the full lifecycle instead of only the first purchase.
Organizations with regional operations can also review broader cybersecurity and infrastructure support through FourTeck Africa. For a Nigeria T125 quotation, provide the city, WAN design, user and device count, VLANs, VPN peers, security-service requirement, subscription term, existing firewall and implementation scope. A well-prepared request speeds up sizing and reduces ambiguity around what is included.
WatchGuard Firebox T125 Seychelles
A WatchGuard Firebox T125 Seychelles project may suit a small office, hospitality back office, professional-service location, retail point, remote administration site or branch that requires secure internet access and controlled connectivity to systems hosted elsewhere. Island connectivity can make bandwidth planning especially important, so the firewall should be sized alongside the WAN service rather than independently. The project team should identify which applications are interactive, which can tolerate delay and which must remain available if the primary connection is degraded.
For hospitality or visitor-facing environments, segmentation deserves early attention. Guest traffic should normally be separated from business administration, finance, CCTV, building systems and staff devices. A managed switch and VLAN-based design can allow the T125 to enforce those boundaries without requiring a separate physical firewall interface for every network. Policy should permit only the communication required for business operation, and remote administrative access should be restricted and logged.
Remote support planning is also valuable. If technical staff are not permanently onsite, the organization should define how the firewall can be managed securely, how backups are retained, how console access would be provided during a serious incident and who has authority to approve policy changes. WatchGuard Cloud can be evaluated for centralized management, while local management remains an option. The chosen method should support reliable troubleshooting without creating unnecessary exposure of administrative interfaces.
A Seychelles buyer should request a quote that includes the exact appliance, licensing term, support entitlement, logistics assumptions, deployment scope and renewal information. If migration is required, provide existing VPN and public-service details before the device is shipped or configured. That allows the implementation team to prepare rules, objects and testing steps in advance and reduces the amount of troubleshooting required during the final cutover.
How to decide whether the T125 is large enough
1. Measure inspected traffic
Use realistic busy-hour traffic with the security features you intend to enable. The ISP package speed alone is not a sizing result.
2. Count devices, not only people
Phones, cameras, printers, access points, servers, guest devices and IoT endpoints add sessions and traffic.
3. Include VPN growth
Document branch tunnels, remote users, application traffic and whether this appliance will act as a central hub.
4. Plan the next bandwidth upgrade
If the ISP circuit is likely to double during the license term, size for that expected lifecycle rather than only today.
Common WatchGuard Firebox T125 questions
Is the Firebox T125 suitable for 25 users?
WatchGuard positions the T125 for about 25 users. Treat that as a portfolio guide rather than a hard capacity limit. The more important factors are inspected bandwidth, number of devices, VPN traffic, TLS inspection, security services, logging and growth.
Does the standard T125 include Wi-Fi?
No wireless capability should be assumed for the standard T125. WatchGuard offers the separate T125-W model with Wi-Fi 7 and external antennas. Confirm the exact model on the quotation.
Can the T125 use WatchGuard Cloud?
Yes. WatchGuard documentation states that the T125 can be managed through WatchGuard Cloud or locally through Fireware management tools. The best approach depends on the organization’s operational model and number of sites.
What is the UTM throughput?
WatchGuard publishes 510 Mbps UTM full-scan throughput for the T125. Actual production performance can differ based on traffic composition, enabled security functions, software version, logging and policy design.
How many Ethernet ports are included?
The appliance has five copper Ethernet interfaces: one 2.5 GbE RJ45 and four 1 GbE RJ45 ports. It also includes two USB-A 3.2 ports and an RJ45 serial console port.
Can it connect branch offices by VPN?
Yes. WatchGuard lists branch-office VPN capability and publishes a limit of 10 branch-office VPN tunnels for this model. Suitability also depends on encrypted traffic volume, routing design and whether the appliance is a spoke or central hub.
Does the price include security subscriptions?
Not necessarily. Market listings can represent hardware-only, Standard Support, Basic Security Suite or Total Security Suite offers with different terms. Always request the exact bundle reference, term and included services in writing.
Can FourTeck help migrate from another firewall?
Migration assistance can be scoped as a professional service. A proper migration reviews interfaces, routes, NAT, policies, address objects, VPNs, authentication, security profiles and unused rules rather than blindly copying the old configuration.
Quotation checklist
Network information
Internet speed, ISP handoff, public IPs, user and device count, switches, VLANs, Wi-Fi, servers and expected bandwidth growth.
Security requirement
HTTPS inspection, IPS, antivirus, DNS security, web filtering, application control, logging, reporting and segmentation goals.
Connectivity
Branch VPN peers, remote VPN users, secondary WAN, SD-WAN requirements, cloud applications and inbound published services.
Commercial scope
T125 or T125-W, security suite, subscription term, support entitlement, rack kit, installation, migration, testing, documentation and renewal planning.
Why contact FourTeck for the WatchGuard Firebox T125?
A useful firewall quote should connect the product to the network it will protect. FourTeck can help buyers turn a model request into a clearer deployment scope by checking bandwidth, security inspection, VPN, segmentation, support, licensing and migration questions before the order is finalized. That reduces the risk of buying the right brand but the wrong capacity, license bundle or implementation package.
FourTeck can also help organizations compare the T125 with larger or smaller WatchGuard models when traffic, interface requirements or branch design suggest a different fit. The objective is not to force one appliance into every location. A repeatable small-branch standard is valuable only when it remains within the performance and feature needs of each site.
For multi-country procurement, share the destination, quantity, required subscription term and deployment expectations. Availability, commercial terms, logistics and implementation should be confirmed in the quotation rather than assumed from online listings. This approach gives procurement, IT and management one documented reference for the purchase and deployment decision.
Decision recap
The WatchGuard Firebox T125 is a strong candidate for a small office or branch that needs business firewall controls, VPN connectivity, network segmentation, SD-WAN support and a choice of local or cloud management. Its 2.5 GbE uplink and four 1 GbE interfaces offer useful physical flexibility, while WatchGuard’s published 510 Mbps UTM and 270 Mbps HTTPS-inspection figures provide more realistic planning anchors than the maximum packet firewall figure.
Before placing an order, confirm the workload, security suite, license term, VPN demand, wired versus wireless model, management method, accessories and implementation scope. A precise requirement produces a more accurate quotation and a smoother cutover.
Related regional FourTeck resources
Organizations evaluating firewall and infrastructure projects across multiple markets can use FourTeck’s regional network for broader planning. In addition to the UAE and Uganda resources linked above, FourTeck Kuwait provides a regional reference for Kuwait technology requirements. These regional sites can help buyers frame country-specific procurement discussions while the final WatchGuard model, license, support and service scope is confirmed in the quotation.

Reviews
There are no reviews yet.