
WatchGuard Firebox M5850 Firewall
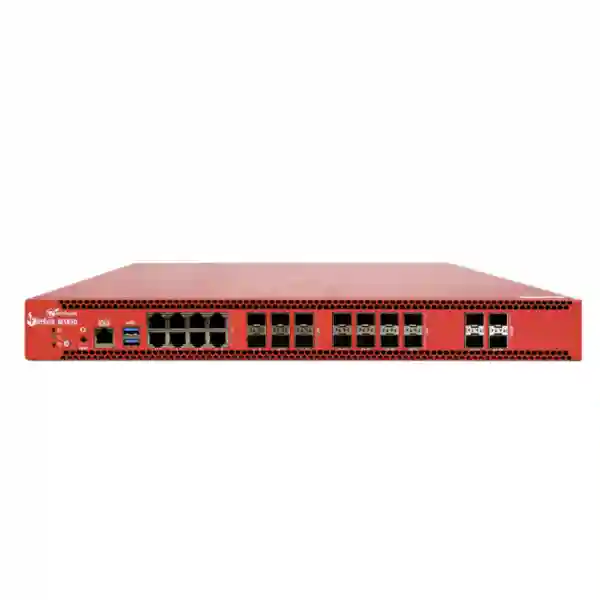
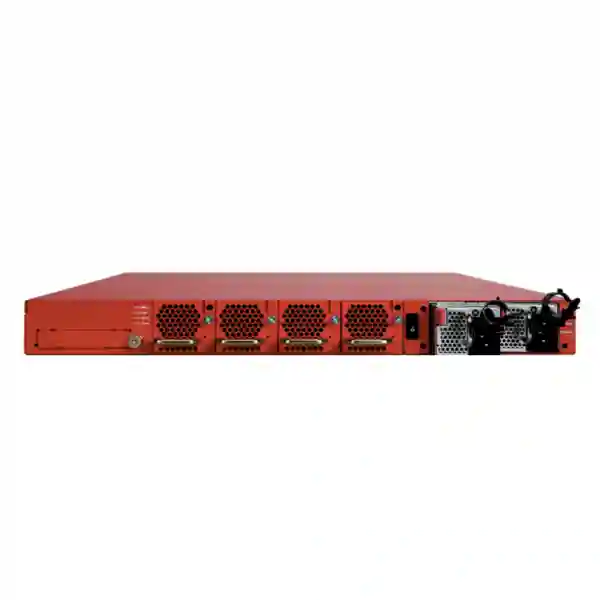
The WatchGuard Firebox M5850 is built for campus, core, headquarters, data-centre-edge and high-demand regional networks where encrypted traffic, branch connectivity, application access and security inspection must share a fast, resilient platform. Its 1U rackmount design combines a 20-core Intel Granite Rapids-D processor, 32 GB of DDR5 ECC memory, 128 GB PCIe SSD storage, a broad mix of copper and fibre interfaces and redundant hot-swappable power supplies. FourTeck supports buyers with requirement review, quotation coordination, license and subscription guidance, migration planning, deployment scope and lifecycle support across Dubai, the UAE and selected regional markets.
Direct answer for buyers
Choose the Firebox M5850 when the project needs a high-throughput WatchGuard platform with dense 1G/10G/25G connectivity and enterprise resilience. Do not size it from internet speed alone. Include inspected traffic, TLS decryption, VPN load, concurrent sessions, branch traffic, high availability, optics, logging and subscription services in the design review.
WatchGuard Firebox M5850 overview
The Firebox M5850 sits in WatchGuard’s current high-rackmount M-series and is intended for organizations that need substantially more headroom than a branch appliance. Manufacturer documentation positions the M4850, M5850 and M6850 family around high performance, scalability, enterprise reliability and flexible connectivity. For the M5850 specifically, WatchGuard documents a 20-core sixth-generation Intel Xeon-class Granite Rapids-D processor, 32 GB of DDR5 ECC memory and a 128 GB M.2 PCIe SSD. This hardware profile matters because modern firewall workloads are not limited to basic stateful packet filtering. Real environments ask the gateway to inspect encrypted sessions, apply intrusion prevention, enforce application and web policies, terminate VPN connections, segment internal networks, log events and maintain consistent policy under periods of heavy traffic.
Published WatchGuard performance information lists up to 79 Gbps firewall throughput and 27 Gbps UTM throughput for the Firebox M5850 under the vendor’s stated test conditions. These figures are useful for comparing platforms, but they should not be read as guaranteed production rates. Packet size, traffic direction, encrypted-session inspection, enabled security services, rule complexity, logging, VPN use, firmware release and network architecture all influence realized throughput. A useful purchasing discussion therefore begins with the workload rather than a headline number. FourTeck can help translate user count, internet circuits, east-west traffic, branch tunnels, remote access, application mix and future growth into a practical sizing conversation.
Connectivity is one of the M5850’s strongest design advantages. The chassis provides eight 1G RJ45 ports, six 1G SFP ports, eight 10G SFP+ ports and four 25G SFP28 ports. WatchGuard also documents an OCP 3.0 PCIe Gen 5 x8 module bay, with current network-card options including additional 25G or 100G connectivity. That mix allows the appliance to sit between internet edges, core switching, server zones, data-centre segments, WAN providers and management networks without forcing every connection through a single speed class. Optical transceivers and cabling should still be checked against the vendor-supported list and the switch architecture before an order is finalized.
Published maximum firewall throughput under stated vendor test conditions.
Published UTM throughput reference; production results vary by enabled controls and traffic.
Built-in copper and fibre interface mix for flexible campus, edge and core designs.
Rackmount form factor with redundant hot-swappable power supplies and four hot-swappable fans.
Verified hardware specification snapshot
Specifications can change with hardware revisions or vendor documentation updates. The quotation should confirm the exact appliance, support term, security services, power cords, rail kit expectations, optics, cables, interface cards and deployment accessories required for the project.
Security, management and deployment planning
WatchGuard supports both local and cloud-oriented management models for this platform. A locally managed Firebox can be administered through Fireware Web UI or WatchGuard System Manager, while WatchGuard Cloud can provide centralized monitoring and, for eligible cloud-managed designs, configuration and template-driven policy administration. The correct management approach depends on operational ownership. A single data-centre team may prefer a different workflow from an MSP or a business with many distributed sites. Before deployment, decide who will approve policy changes, who needs reporting access, where configuration backups will be stored, how administrator authentication will be protected and how emergency access will be handled.
Licensing and subscriptions should be treated as part of the architecture, not as an afterthought. The base appliance and the required security outcome are not necessarily the same thing. Threat prevention, content controls, malware inspection, reputation services, support entitlement and other capabilities depend on the selected WatchGuard package and current licensing policy. Procurement teams should ask for a bill of materials that clearly separates hardware, subscriptions, support, optics, power accessories and professional services. This makes renewal planning easier and avoids discovering after installation that an expected feature was not included in the purchased bundle.
High availability, migration and change control also need project-level planning. When the M5850 replaces an older firewall, the safest approach is not to copy every historical rule without review. Existing NAT entries, site-to-site tunnels, published services, web policies, address objects, routes, VLANs and remote-access permissions should be classified as required, obsolete or in need of redesign. This is the point to remove abandoned rules, tighten broad access, document business owners and prepare a rollback plan. FourTeck’s firewall deployment guidance explains why discovery, testing and documentation matter as much as the physical appliance.
Best-fit environments
Large headquarters, campus networks, high-bandwidth internet edges, regional hubs, data-centre perimeter roles, VPN concentration and organizations standardizing WatchGuard across multiple sites.
Sizing inputs
Inspected throughput, TLS decryption, user count, application mix, tunnels, concurrent sessions, peak packet rate, internal segmentation, logging, HA, future circuit upgrades and support model.
Procurement inputs
Destination country, quantity, license term, required power cord, rail and rack details, optics, interface-card requirements, support entitlement, configuration scope and target deployment window.
FourTeck resources for a complete firewall project
The M5850 should be evaluated within the wider network design. Use the Firewall Dubai services page for installation, configuration, migration, VPN and support scope; the perimeter firewall planning page for edge-security design; and the FourTeck firewall capability overview for information about the support approach. Buyers reviewing broader alternatives can also use the verified same-site compact firewall product example, branch firewall product page, SMB firewall product page and enterprise firewall family guide to understand how capacity, licensing and deployment requirements change across firewall classes. These links are supplied as related buying resources rather than direct performance equivalents to the M5850.
WatchGuard Firebox M5850 Dubai
Organizations searching for WatchGuard Firebox M5850 Dubai are usually not looking for a small branch firewall. The model is relevant to enterprises, campuses, large offices, regional headquarters and high-bandwidth environments that need a rackmount security gateway with dense fibre connectivity and enough processing headroom for substantial inspection workloads. In Dubai, a useful M5850 discussion should start with the actual role of the appliance: internet edge, data-centre perimeter, VPN concentrator, inter-zone segmentation point, regional hub or a combination of these. That role determines how many interfaces are needed, whether 10G or 25G uplinks are required, how traffic will be distributed across zones and what redundancy is expected. FourTeck can help Dubai buyers turn those questions into a structured bill of materials and implementation scope rather than treating the purchase as a single hardware line item.
Dubai networks often combine high-speed internet, cloud applications, voice, CCTV, guest wireless, remote access and private application traffic. An M5850 can provide a central policy point for these flows, but the design must preserve business performance when security controls are active. Buyers should provide peak internet usage, internal uplink speeds, expected VPN traffic, decryption requirements, public services, branch counts, user authentication methods and logging expectations. If a business plans to upgrade from 1G or 10G switching toward 25G, the appliance’s built-in SFP28 ports may reduce the need for immediate interface expansion, while the OCP 3.0 bay gives another design option when additional high-speed connectivity is justified. Optics, patching and switch compatibility must still be confirmed.
Procurement for WatchGuard Firebox M5850 UAE projects based in Dubai should also cover power and rack readiness. The appliance is a 1U platform with redundant hot-swappable power supplies and four hot-swappable fans, so the rack should provide suitable depth, grounding, ventilation and conditioned power. A four-post rack is the vendor’s intended rail-kit scenario. Before ordering, confirm power-cord region, available PDU outlets, fibre transceiver types and whether the project requires a second appliance for resilience. For broader UAE technology planning, buyers can review FourTeck UAE infrastructure and cybersecurity solutions or use the Firewall Dubai security portal for firewall-specific guidance.
A quotation request should state whether FourTeck is expected to provide hardware only, licensing, migration, installation, firewall policy design, VPN setup, testing, documentation or ongoing support. Sharing the existing firewall model and a sanitized configuration summary can make the discussion more efficient. FourTeck does not treat a web page as proof of immediate stock or a guaranteed delivery date; availability, licensing and project timing should be confirmed in the formal quotation. That is especially important for enterprise appliances, where the correct support term, optics and professional services can matter as much as the chassis itself.
WatchGuard Firebox M5850 UAE
For buyers researching WatchGuard Firebox M5850 UAE, the main challenge is matching a high-capacity security platform to a network that may span several emirates, internet providers and business sites. A UAE organization may use the M5850 at a head office or data-centre edge while smaller firewalls protect branches. In that design, the M5850 can become the aggregation point for site-to-site connectivity, security policy, public services and centralized traffic inspection. The architecture should be documented before purchasing: primary and secondary WAN circuits, routed or transparent requirements, VLAN and zone structure, branch prefixes, cloud destinations, remote-user access, public IP use and the operational team responsible for policy changes.
UAE enterprise networks frequently need a mix of copper and optical connections. The M5850’s eight 1G RJ45, six 1G SFP, eight 10G SFP+ and four 25G SFP28 interfaces provide flexibility, but not every port is automatically the right fit for every switch or service-provider handoff. Procurement should verify supported transceivers, fibre type, connector standards and the expected link speed at both ends. If the network is moving toward 25G core links, confirm whether the built-in ports are sufficient before adding an OCP card. If 100G is required, validate the specific optional card and the surrounding switch design. These checks prevent a common enterprise procurement problem: receiving the correct firewall chassis but missing the optics or interface capability needed for deployment day.
The licensing conversation is equally important. Buyers should define whether they need only firewall and VPN functions or a broader WatchGuard security service package. Support entitlement, security subscriptions, cloud management requirements and renewal period should be written into the commercial request. For organizations with formal change-control or compliance processes, logging retention and reporting should be planned alongside the firewall because storage and central reporting architecture affect operations after deployment. The latest supported Fireware release for the platform should also be checked before installation, especially when integrating with existing management, authentication or monitoring systems.
FourTeck can support UAE buyers with requirement review, model fit, quotation preparation, migration planning and deployment discussions. A useful inquiry includes the number of sites, internet bandwidth, inspection goals, VPN design, user counts, internal link speeds, rack and power details, target license term, preferred management approach and whether a high-availability pair is being considered. For wider regional infrastructure context, visit FourTeck integrated IT and networking solutions. Availability and service scope vary by project, so the final quotation should be treated as the authoritative source for part numbers, entitlements and commercial terms.
WatchGuard Firebox M5850 Uganda
Customers searching for WatchGuard Firebox M5850 Uganda typically have a larger requirement than a single small office. The platform is more relevant to national organizations, financial institutions, education networks, service providers, large hospitality groups, healthcare networks, NGOs, government-related projects, regional headquarters and businesses that aggregate many branches through one security edge. The first buying question should therefore be whether the M5850 is intended for the primary internet gateway, a data-centre boundary, a regional VPN hub, segmentation between critical network zones or a resilient pair protecting multiple functions. Clear role definition helps avoid oversizing or placing a powerful appliance where a different architecture would be more efficient.
Uganda deployments should be planned around connectivity realities at every site. A headquarters may have high-capacity fibre, while branch locations use different carriers or lower-speed circuits. The central firewall must be sized not only for the sum of branch traffic, but also for inspection, encrypted sessions, application access, backup links and growth. If branches terminate site-to-site VPNs on the M5850, document tunnel ownership, routing, failover behavior and how remote sites will be monitored. If the firewall protects server or cloud-access networks, identify which services require inbound publishing, which need private VPN access and which should be isolated behind stricter policy. This produces a more useful configuration than a collection of broad allow rules.
Power and environmental planning deserves attention for Uganda projects. The M5850 is an indoor rackmount platform rated by WatchGuard for operation from 0°C to 40°C. The vendor recommends conditioned power, and the appliance uses redundant hot-swappable power supplies. A project team should confirm rack depth, ventilation, UPS capacity, PDU outlets and grounding at the installation location. If the firewall is deployed in a data room that also houses core switches, servers and storage, total heat and power design matters. Spare optics, supported transceivers and clearly labeled fibre paths can also reduce troubleshooting time when the site is far from a major support center.
FourTeck can coordinate requirement and quotation discussions for Uganda buyers through its wider African technology channel. The FourTeck Africa platform provides regional context for firewall, networking and infrastructure projects. Before requesting a WatchGuard Firebox M5850 Uganda price, prepare user and site counts, primary and backup bandwidth, VPN requirements, switch uplink speeds, license term, security services, rack details, destination city and expected professional services. Availability, warranty handling, logistics and implementation scope should be confirmed for the actual project rather than assumed from a regional product page.
WatchGuard Firebox M5850 Kampala
A WatchGuard Firebox M5850 Kampala requirement is most credible when it is tied to a defined enterprise role. Kampala hosts organizations with headquarters functions, data rooms, service centers, branch aggregation, cloud connectivity and security operations that can justify a platform with dense fibre interfaces and substantial processing capacity. Instead of beginning with a generic request for the appliance, IT and procurement teams should identify the traffic path that the M5850 will control. Is it replacing a legacy firewall at the main office, protecting internet access for hundreds or thousands of users, consolidating branch VPNs, segmenting server networks, or supporting a high-availability perimeter? That answer shapes the number of interfaces, optics, security subscriptions and implementation work required.
Kampala projects should document both current bandwidth and the planned network roadmap. An organization may order the M5850 because today’s 1G or 10G edge is approaching capacity, but the stronger business case often comes from future fibre upgrades, increased SaaS use, video traffic, remote users, branch growth and deeper security inspection. The appliance’s 10G SFP+ and 25G SFP28 ports can support faster core and WAN designs, while the built-in 1G ports provide flexibility for management, auxiliary networks or lower-speed handoffs. The exact port mapping should be designed before installation so that the firewall does not become a patching experiment during cutover.
Operational ownership is another key factor for Kampala organizations. Decide whether the firewall will be locally managed or integrated with WatchGuard Cloud, who receives alerts, how backups are retained, who approves policy changes and how emergency access is protected. If the organization operates branches outside Kampala, establish a consistent naming convention for tunnels, zones, address objects and policies. Consistency makes troubleshooting easier when a remote site reports that an application or VPN is unavailable. It also reduces the risk of temporary rules remaining in place after urgent changes.
For procurement, include the Kampala delivery destination, quantity, required support term, subscription package, interface requirements, transceivers, power-cord requirement, rack availability, desired configuration scope and target cutover window. Ask separately for hardware, licenses, optics and professional services so stakeholders can see the full project cost. FourTeck can assist with sizing discussions and regional sourcing coordination, but stock position and lead time should be confirmed at quotation. A well-prepared inquiry produces a faster and more accurate commercial response than simply asking for the lowest M5850 price.
WatchGuard Firebox M5850 Arua
WatchGuard Firebox M5850 Arua searches are likely to come from organizations planning a regional hub, a high-value institutional network or a distributed environment rather than a conventional small branch. In Arua, the important question is whether the firewall belongs locally at the site or centrally at a larger hub with Arua connected through secure WAN or VPN links. The M5850 has capacity and interface density designed for major traffic aggregation, so a network with modest local bandwidth may gain more value from a smaller branch firewall connected to an M5850 at a regional core. FourTeck can help buyers evaluate this architecture instead of assuming that every location needs the same hardware class.
Where an Arua deployment does justify the M5850, planning should prioritize resilience and serviceability. The appliance includes redundant hot-swappable power supplies and hot-swappable fans, but those features are most useful when the site has proper rack power, UPS protection, ventilation and support procedures. Organizations should document who can access the equipment room, how spare optics are stored, whether there is a secondary internet circuit and how configuration backups can be retrieved if a local hardware or connectivity issue occurs. For remote or regionally distributed operations, these practical details often have more impact on uptime than the maximum firewall throughput figure.
Connectivity planning should also be realistic. The M5850 offers multiple 1G copper and fibre ports plus 10G and 25G fibre interfaces. If the local WAN handoff is lower speed, the higher-speed ports may still be valuable for internal core switching, server networks or future upgrades, but there is no benefit in buying optics that the current switches cannot use. Confirm transceiver compatibility, fibre type and link budgets. If the project includes a primary link and a different backup technology, define routing and failover behavior before deployment. Branch VPNs should be built with clear subnets and policy ownership so route overlap or broad access does not create a support problem later.
An Arua quotation request should specify the business role of the site, local and upstream bandwidth, number of remote locations, required inspection services, management preference, rack and power environment, delivery details and whether deployment assistance is needed onsite or remotely. FourTeck can use these inputs to determine whether the requested M5850 is appropriate and to prepare a clearer commercial scope. Availability, logistics and support coverage are project dependent, so the final purchase decision should follow a confirmed bill of materials and implementation plan rather than an unverified online assumption.
WatchGuard Firebox M5850 Mbarara
For organizations evaluating WatchGuard Firebox M5850 Mbarara, the strongest use cases involve a regional headquarters, institutional campus, large healthcare or education network, enterprise distribution operation, financial network, service provider environment or another site that carries significant traffic for multiple users and locations. A buyer should first separate the firewall’s security role from the general network design. The M5850 can enforce policy, inspect traffic, terminate VPNs and connect high-speed zones, but it still depends on well-designed switching, routing, power, authentication and monitoring around it. Treating the firewall as the entire security solution can leave important dependencies unplanned.
Mbarara environments may have a combination of local business applications, cloud platforms, voice, video, guest access and branch connections. These services should not all receive identical access. Before implementation, define trusted user networks, guest or public networks, server segments, management interfaces, CCTV or IoT zones and any partner connectivity. The M5850’s interface density supports physical separation where appropriate, while VLAN and policy design can provide logical segmentation. The right mix depends on the switch architecture and the operational need. Security teams should avoid broad any-to-any policies simply because the platform has ample performance; clear segmentation is a design discipline, not a throughput constraint.
Migration deserves special care when the new firewall replaces an older gateway. Collect the current rulebase, NAT entries, VPN definitions, routing table, DHCP or DNS dependencies, public services and administrative accounts. Classify each item before rebuilding it. Legacy firewalls often contain temporary troubleshooting rules, retired server objects or outdated vendor access that should not be carried forward. A staged migration plan with application testing and rollback steps can reduce disruption. If the M5850 will become a central VPN hub for Mbarara and other sites, tunnel naming, route summarization and monitoring should be standardized from the start.
For a useful quotation, provide quantity, destination, business role, user count, WAN bandwidth, internal uplink speeds, required security services, support term, VPN details, optics and rack requirements. State whether you need appliance supply only or also configuration, migration, testing, documentation and handover. FourTeck can coordinate these requirements within a regional project framework. Commercial availability, support eligibility and delivery arrangements should be confirmed in writing because they can vary by destination and license package.
WatchGuard Firebox M5850 Gulu
A WatchGuard Firebox M5850 Gulu project should be approached as an enterprise infrastructure decision. The appliance is capable of serving as a major security gateway, and that makes requirement clarity essential. A regional organization may use it to protect a large campus, aggregate remote sites, secure a server environment or provide a resilient internet edge. Another organization may discover that a smaller local firewall paired with a central M5850 elsewhere is more appropriate. The sizing process should therefore compare the requested model with the actual volume of inspected traffic, number of users, VPN responsibilities, link speeds and future growth rather than assuming the most powerful available option is automatically the best purchase.
For a Gulu deployment, continuity planning can be particularly important. The M5850 provides redundant hot-swappable power supplies, but a complete design also needs conditioned power, UPS capacity, proper grounding and a suitable rack. The vendor specifies indoor installation and an operating range up to 40°C, so the equipment room should be ventilated and protected from uncontrolled heat, dust and unauthorized access. Project teams should also keep clear records of serial numbers, support entitlements, installed transceivers, interface assignments and configuration backups. These records reduce the time needed to troubleshoot a fault or coordinate vendor support.
Network design should anticipate communications between Gulu and other business locations. If the firewall terminates branch VPNs, define which resources each branch can access and avoid flat network policies. If remote administrators connect to the appliance, restrict management access and use strong authentication according to the organization’s security policy. If internet links from more than one provider are used, design the routing and failover behavior before cutover. The M5850’s multiple fibre interfaces can support diverse uplinks and core connections, but interface abundance does not replace the need for a clear routing plan.
A Gulu buyer should send FourTeck a structured requirement containing the expected site role, traffic profile, security-service needs, VPN count, management preference, optics, power and rack conditions, support term and delivery location. For multi-site projects, include all branches so the central design can be reviewed as one system. FourTeck can then help prepare a model-fit discussion and quotation. Lead time, delivery method and regional service scope are not assumed and should be agreed as part of the final commercial process.
WatchGuard Firebox M5850 Kenya
WatchGuard Firebox M5850 Kenya buyers are likely to be enterprises, financial services organizations, universities, healthcare groups, logistics networks, service providers, large hospitality operators, technology companies and institutions with substantial internet or branch traffic. The M5850 can fit a Nairobi headquarters, data-centre perimeter or central VPN hub, while other Kenyan sites connect through appropriately sized branch appliances. This hub-and-spoke or regional-core design can be more cost-effective than deploying the same high-end model everywhere. The correct architecture depends on traffic patterns, resilience objectives and whether security inspection is performed centrally or at each site.
Kenya projects should account for high-speed fibre growth. If the current environment already uses 10G core links or plans to move toward 25G, the M5850’s built-in SFP+ and SFP28 interfaces are directly relevant. Confirm switch-side capabilities and supported transceivers before purchase. If traffic arrives from multiple carriers, map each WAN to the intended physical interface and define failover or policy routing. If branches in Mombasa, Kisumu, Nakuru, Eldoret or other locations connect to the same security edge, document bandwidth per tunnel, route advertisements, authentication and monitoring. A central firewall can become operationally complex unless naming and policy structure are standardized.
Security subscriptions and management should be included in the Kenyan procurement plan. Decide which inspection services are required, how long support and security services should run, who will administer the platform and whether WatchGuard Cloud is part of the operating model. Procurement teams should also ask for the complete landed project scope: appliance, power cords, optics, interface cards if required, support entitlement, subscriptions, installation, migration and training or handover. Separating these items helps compare offers on a like-for-like basis and reduces the risk of approving an apparently low hardware price that excludes critical services.
FourTeck provides a dedicated Kenya technology and network-security channel for regional buyers. When requesting a WatchGuard Firebox M5850 Kenya quote, include the delivery city, quantity, internet links, user count, branch list, VPN needs, inspection profile, rack and power information, desired license term and implementation scope. Current availability and project logistics should be confirmed before approval. For enterprise migrations, schedule discovery and testing separately from the procurement date so the hardware can arrive with a configuration plan already defined.
WatchGuard Firebox M5850 Kuwait
Businesses researching WatchGuard Firebox M5850 Kuwait may be planning a high-capacity enterprise edge for a headquarters, campus, data centre, energy-related environment, financial institution, hospitality group or multi-site organization. The M5850’s combination of 10G and 25G fibre ports is particularly relevant where internal network speeds are already above basic Gigabit Ethernet and where multiple high-bandwidth WAN or core links must be secured. A Kuwait project should begin with an interface and traffic map showing carrier handoffs, core switches, server zones, management networks, VPN paths and any public-facing services. This makes the hardware choice and optic list much easier to validate.
Environmental and power planning should be explicit. WatchGuard specifies indoor deployment, redundant hot-swappable power supplies and an operating range up to 40°C. The firewall should therefore be installed in a controlled equipment room with adequate cooling, conditioned power, grounding and rack space. The presence of redundant PSUs does not create full resilience if both feeds are connected to the same unprotected power source. For higher-availability requirements, consider separate PDU paths, UPS design and whether a second firewall is required. These infrastructure choices should be discussed before the unit is delivered, not discovered during rack installation.
Licensing is another procurement variable. Buyers should ask which WatchGuard security services and support rights are included, which are optional, how long the term runs and what renewal will be required. If the firewall is managed centrally or integrated into a broader WatchGuard environment, confirm software and management compatibility. If the project includes migration from another platform, provide sanitized details of current rules, NAT, VPN, routing, authentication and public services so the scope can be estimated. A controlled migration with a rollback plan is preferable to rebuilding complex enterprise policies during a short maintenance window.
FourTeck’s Kuwait IT and network-security portal supports regional requirement and quotation discussions. For a useful M5850 request, include quantity, delivery location, link speeds, VPN use, required inspection services, optic types, desired support period, rack and power information, and whether installation or remote configuration is needed. Product availability, licensing region, warranty handling and logistics can depend on the final bill of materials, so these items should be confirmed in the written quotation before purchase approval.
WatchGuard Firebox M5850 Ghana
WatchGuard Firebox M5850 Ghana projects are most relevant to organizations with substantial central security requirements: large corporate headquarters, financial networks, public institutions, universities, healthcare groups, service providers, regional hubs, industrial organizations and multi-branch businesses. The model can operate as a high-capacity security edge, but buyers should verify whether the traffic volume and growth plan justify this class of appliance. A smaller site with limited bandwidth may be better protected by a branch model connected securely to an M5850 at the central site. A proper design exercise therefore maps where inspection should occur and how traffic between branches, cloud services and internal applications should flow.
For Ghana deployments, resilient connectivity is often as important as firewall horsepower. If the organization uses multiple internet providers, define which links carry normal traffic, which provide failover and how inbound services behave when a circuit changes. If the M5850 terminates site-to-site VPNs for Accra and other locations, document route ownership and application dependencies. Avoid using a single flat security zone for branch traffic simply because the sites belong to the same organization. Finance, administration, servers, guest networks, CCTV, voice and operational systems may need separate controls even when they share the same WAN.
Hardware readiness should also be reviewed. The M5850 is a 1U device weighing about 9 kg and includes redundant hot-swappable power supplies and four hot-swappable fans. Confirm rack depth, rail compatibility, UPS capacity, conditioned power, cooling and physical access controls. Fibre projects should list required SFP, SFP+ or SFP28 transceivers and confirm switch-side compatibility. If 100G expansion is being considered, validate the optional OCP card and the business case for the additional interface speed. Purchasing optics without checking both ends of the link is a common and avoidable source of deployment delay.
Ghana buyers can use FourTeck’s African technology channel for regional project coordination. A strong quotation request should identify the destination city, number of sites, internet and core speeds, inspection goals, VPN design, security subscriptions, desired support term, management preference and professional services required. Ask the proposal to distinguish hardware, licenses, optics, logistics and deployment work. FourTeck can assist with requirement review, but current stock, warranty route, lead time and onsite service arrangements should be verified for the final project rather than inferred from general regional coverage.
WatchGuard Firebox M5850 Nigeria
For WatchGuard Firebox M5850 Nigeria requirements, the appliance is best considered for environments where security traffic is concentrated at a large office, data centre, campus or regional hub. Nigerian enterprises may operate many branches, cloud-connected business applications, payment or ERP systems, remote-user VPNs, public services and high-capacity internet circuits. The M5850 can provide the processing and interface density needed for these responsibilities, but it should be sized against measured traffic and planned growth. Procurement teams should collect peak throughput, session behavior, encrypted traffic percentage, tunnel counts, user populations and expected core-link speeds before finalizing the model.
Nigeria’s distributed business environments make network architecture especially important. If Lagos or another major hub hosts the M5850 while remote offices connect over VPN or private WAN, define which security policies are enforced centrally and which remain local. Avoid sending unnecessary traffic through the hub simply because the central firewall has spare capacity; routing should reflect application location, cloud access and resilience. Multi-provider connectivity should have documented failover behavior. Public-facing services should be isolated in appropriate zones, and administrative access to the firewall should be restricted to trusted management paths.
The commercial package should be reviewed as carefully as the technical design. An enterprise firewall project can include the appliance, support entitlement, security subscriptions, power accessories, optics, rack hardware, optional interface cards, migration services, configuration, testing and handover. Ask for these line items explicitly so approval teams understand the full solution. If the existing firewall uses many NAT rules or VPN tunnels, provide a configuration summary early. This allows migration effort to be estimated and helps identify old policies that should be retired instead of copied.
FourTeck can coordinate Nigeria inquiries through its wider regional supply and project-support framework. When requesting pricing, include delivery city, quantity, required term, network role, link speeds, number of branches, VPN needs, optics, high-availability expectations and whether you need onsite or remote professional services. Local availability, import or logistics arrangements, warranty path and schedule depend on the specific order and should be confirmed in the formal quotation. A structured requirement will normally produce a more useful answer than a bare request for a WatchGuard Firebox M5850 Nigeria price.
WatchGuard Firebox M5850 Seychelles
A WatchGuard Firebox M5850 Seychelles deployment is likely to be associated with a larger enterprise, hospitality group, government or institutional network, service provider, financial organization or a central site that aggregates several locations. Because Seychelles projects can have stronger logistics constraints than large mainland markets, the design should consider not only firewall capacity but also serviceability, spare planning and remote administration. The M5850 includes redundant power supplies and hot-swappable fans, but organizations should still plan how support incidents will be handled, where compatible optics are sourced and how configuration backups can be accessed if a hardware replacement becomes necessary.
Connectivity can include a combination of local fibre, internet services, inter-site links and cloud traffic. The M5850’s 1G, 10G and 25G ports provide flexibility for different handoffs, but an island deployment should avoid unnecessary complexity. Use the minimum number of interface types that meet the design, keep spare transceivers for critical links when justified and label every fibre path clearly. If the firewall protects several resorts, offices or operational sites, define VPN routes, allowed applications and management access for each location. Centralized visibility is valuable, but branch traffic should still be segmented according to business function rather than treated as one trusted network.
Environmental controls are essential for reliability. The appliance is intended for indoor installation and WatchGuard recommends a secure location with conditioned power. A Seychelles equipment room should provide adequate cooling, UPS support, grounding and physical access control. If the site is exposed to higher ambient heat or humidity outside the controlled room, that makes proper enclosure and air conditioning more important. Rack depth and rail installation should be checked before shipment because resolving a mounting mismatch after arrival can slow a project unnecessarily.
For procurement, provide FourTeck with the delivery island or city, quantity, internet and core bandwidth, firewall role, branch count, security services, support term, optics, rack and power information, and any installation or migration needs. Ask for logistics, warranty handling and deployment scope to be written clearly into the offer. For African and Indian Ocean regional technology context, the FourTeck Africa technology platform can be used as an additional inquiry route. Availability and scheduling should be confirmed for the specific project rather than assumed from general regional coverage.
How to size the M5850 before ordering
Sizing should be based on the traffic that will actually pass through security services. Start with peak WAN and internal throughput, then identify how much traffic will be inspected, decrypted, tunneled or logged. Estimate growth over the intended service life rather than selecting a platform that only meets today’s utilization. Review concurrent users and sessions, new-connection rates, branch VPN demand, remote-access use, east-west segmentation and any large data transfers that could pass through the firewall. If the organization uses high-bandwidth backup, replication, video or data-centre traffic, determine whether those flows should traverse the firewall and under what inspection policy.
Interface planning is part of sizing. A firewall with strong processor capacity can still become the wrong choice if the required physical links are missing. Map each WAN, core, HA, management and server-zone connection to a port speed and media type. Confirm optics and cabling. Then decide whether the built-in interface mix is sufficient or whether an OCP expansion card is justified. Finally, review high availability, because a resilient pair doubles some hardware and licensing considerations even when the traffic capacity requirement remains unchanged.
Frequently asked questions
Is the M5850 suitable for a small office?
Usually it is evaluated for larger, higher-throughput environments. A small office should be sized from users, internet speed, inspection needs and growth rather than choosing an enterprise platform by name.
Does it support 25G fibre?
Yes. WatchGuard documents four built-in 25G SFP28 interfaces on the M5850. Compatible optics and switch-side capabilities still need confirmation.
Can it be managed in WatchGuard Cloud?
WatchGuard documentation supports cloud-managed and locally managed workflows for this platform. The best choice depends on operations, entitlement and the wider WatchGuard estate.
Are subscriptions required?
The appliance can provide core firewall capabilities, while many advanced security services and support functions depend on the selected license or subscription package. Confirm the bundle in the quotation.
Should we buy one or two appliances?
That depends on uptime requirements and the network design. A high-availability architecture requires a separate design review covering peer hardware, links, licenses, failure behavior and maintenance procedures.
What should be sent for a quote?
Send quantity, destination, internet and core speeds, user count, VPN needs, security services, license term, optics, rack and power details, HA requirement and professional-service scope.
Decision recap
The WatchGuard Firebox M5850 is a strong candidate when an organization needs an enterprise 1U firewall with substantial processing capacity, a wide range of built-in fibre interfaces, redundant power and flexible local or cloud-oriented management. Its published performance figures and 10G/25G connectivity make it relevant to campus, headquarters, data-centre-edge and aggregation roles, but the correct decision depends on inspected traffic, security services, VPN load, interface design, high availability and operational ownership.
Before approval, confirm that the M5850 is neither undersized for full inspection nor unnecessarily oversized for the actual workload. Verify the exact WatchGuard license bundle, support term, power cords, optics, rails, OCP card requirements, management design and migration scope. A complete project quotation should make every one of those items visible.
Quotation checklist
Peak WAN, inspected traffic, decryption, branch flows, backup traffic and growth.
WAN links, switch uplinks, copper/fibre mix, optics, 10G/25G needs and expansion.
IPS, web controls, malware inspection, VPN, authentication, logging and subscriptions.
HA, power feeds, UPS, rack, cooling, rollback plan and support coverage.
Related product and service area
For a broader model-selection process, start with the verified Firewall Dubai product catalogue and the firewall implementation and support services. Organizations designing an internet edge can review the perimeter firewall planning resource, while teams preparing a cutover can use the deployment and migration guide. These same-site resources help procurement and technical teams separate model choice from implementation scope.
If the M5850 request is part of a wider procurement review, compare architecture rather than headline throughput alone. Different firewall families have different licensing, management and interface models, so the correct alternative should be selected from the actual workload and operational requirements. FourTeck can help document those requirements and prepare a quotation shortlist without assuming direct equivalence between unrelated platforms.
Plan your WatchGuard Firebox M5850 project with FourTeck
Send the deployment country, quantity, internet links, user count, branch topology, security services, VPN requirement, switch uplink speeds, optics, support term, high-availability objective and migration scope. FourTeck can use this information to prepare a more accurate commercial and technical discussion. For corporate background and regional IT integration, the approved FourTeck network resources used on this page include FourTeck UAE, FourTeck regional IT solutions, FourTeck Kenya, FourTeck Africa and FourTeck Kuwait.

Reviews
There are no reviews yet.